healthcarereimagined

Envisioning healthcare for the 21st century

  • About
  • Economics

A quick guide to the most important AI law you’ve never heard of – MIT Tech Review

Posted by timmreardon on 05/13/2022
Posted in: Uncategorized. Leave a comment

By Melissa Heikkiläarchive page May 13, 2022

The European Union is planning new legislation aimed at curbing the worst harms associated with artificial intelligence.
It’s a Wild West out there for artificial intelligence. AI applications are increasingly used to make important decisions about humans’ lives with little to no oversight or accountability. This can have devastating consequences: wrongful arrests, incorrect grades for students, and even financial ruin. Women, marginalized groups, and people of color often bear the brunt of AI’s propensity for error and overreach. 

The European Union thinks it has a solution: the mother of all AI laws, called the AI Act. It is the first law that aims to curb these harms by regulating the whole sector. If the EU succeeds, it could set a new global standard for AI oversight around the world.

But the world of EU legislation can be complicated and opaque. Here’s a quick guide to everything you need to know about the EU’s AI Act. The bill is currently being amended by members of the European Parliament and EU countries. 

What’s the big deal?

The AI Act is hugely ambitious. It would require extra checks for “high risk” uses of AI that have the most potential to harm people. This could include systems used for grading exams, recruiting employees, or helping judges make decisions about law and justice. The first draft of the bill also includes bans on uses of AI deemed “unacceptable,” such as scoring people on the basis of their perceived trustworthiness. 

The bill would also restrict law enforcement agencies’ use of facial recognition in public places. There is a loud group of power players, including members of the European Parliament and countries such as Germany, that want a full ban or moratorium on its use in public by both law enforcement and private companies, arguing that the technology enables mass surveillance. 

If the EU manages to pull this off, it would be one of the strongest curbs yet on the technology. Some US states and cities, such as San Francisco and Virginia, have introduced restrictions on facial recognition, but the EU’s ban would apply to 27 countries and a population of over 447 million people.

How will it affect citizens? 

In theory, it should protect humans from the worst side effects of AI by ensuring that applications face at least some level of scrutiny and accountability. 

People can trust that they will be protected from the most harmful forms of AI, says Brando Benifei, an Italian member of the European Parliament, who is a key member of the team amending the bill. 

Related Story

Deepfake porn is ruining women’s lives. Now the law may finally ban it.

After years of activists fighting to protect victims of image-based sexual violence, deepfakes are finally forcing lawmakers to pay attention.

The bill requires people to be notified when they encounter deepfakes, biometric recognition systems, or AI applications that claim to be able to read their emotions. Lawmakers are also debating whether the law should set up a mechanism for people to complain and seek redress when they have been harmed by an AI system. 

The European Parliament, one of the EU institutions working on amending the bill, is also pushing for a ban on predictive policing systems. Such systems use AI to analyze large data sets in the interest of preemptively deploying police to crime-prone areas or to trying to predict a person’s potential criminality. These systems are highly controversial, and critics saythey are often racist and lack transparency.

What about outside the EU?

The GDPR, the EU’s data protection regulation, is the bloc’s most famous tech export, and it has been copied everywhere from California to India. 

The approach to AI the EU has taken, which targets the riskiest AI, is one that most developed countries agree on. If Europeans can create a coherent way to regulate the technology, it could work as a template for other countries hoping to do so too. 

“US companies, in their compliance with the EU AI Act, will also end up raising their standards for American consumers with regard to transparency and accountability,” says Marc Rotenberg, who heads the Center for AI and Digital Policy, a nonprofit that tracks AI policy.

The bill is also being watched closely by the Biden administration. The US is home to some of the world’s biggest AI labs, such as those at Google AI, Meta, and OpenAI, and leads multiple different global rankings in AI research, so the White House wants to know how any regulation might apply to these companies. For now, influential US government figures such as National Security Advisor Jake Sullivan, Secretary of Commerce Gina Raimondo, and Lynne Parker, who is leading the White House’s AI effort, have welcomed Europe’s effort to regulate AI.

“This is a sharp contrast to how the US viewed the development of GDPR, which at the time people in the US said would end the internet, eclipse the sun, and end life on the planet as we know it,” says Rotenberg.

Despite some inevitable caution, the US has good reasons to welcome the legislation. It’s extremely anxious about China’s growing influence in tech. For America, the official stance is that retaining Western dominance of tech is a matter of whether “democratic values” prevail. It wants to keep the EU, a “like-minded ally,” close. 

What are the biggest challenges? 

Some of the bill’s requirements are technically impossible to comply with at present. The first draft of the bill requires that data sets be free of errors and that humans be able to “fully understand” how AI systems work. The data sets that are used to train AI systems are vast, and having a human check that they are completely error free would require thousands of hours of work, if verifying such a thing were even possible. And today’s neural networks are so complex even their creators don’t fully understand how they arrive at their conclusions. 

Tech companies are also deeply uncomfortable about requirements to give external auditors or regulators access to their source code and algorithms in order to enforce the law.

“The current drafting is creating a lot of discomfort because people feel that they actually can’t comply with the regulations as currently drafted,” says Miriam Vogel, who is the president and CEO of EqualAI, a nonprofit working on reducing unconscious bias in AI systems. She also chairs the newly founded National AI Advisory Committee, which advises the White House on AI policy. 

There’s also a giant fight brewing over whether the AI Act should ban the use of facial recognition outright. It’s contentious because EU countries hate it when Brussels tries to dictate how they should handle matters of national security or law enforcement. Several countries, such as France, want to make exceptions for using facial recognition to protect national security. In contrast, the new government of Germany, another big European country and an influential voice in EU decision making, has said it supports a full ban on the use of facial recognition in public places. 

Another big fight will be over what kinds of AI get classified as “high risk.” The AI Act has a list that ranges from lie detection tests to systems used to allocate welfare payments. There are two opposing political camps—one fearing that the vast scope of the regulation will slow down innovation, and the other arguing that the bill as written will not do enough to protect people from serious harm. 

Won’t this stifle innovation? 

A common criticism from Silicon Valley lobbyists is that the regulation will create extra red tape for AI companies. Europe disagrees. The EU counters that the AI Act will only apply to the riskiest set of AI uses, which the European Commission, the EU’s executive arm, estimates would apply to just 5 to 15% of all AI applications.

Tech companies “should be reassured that we want to give them a stable, clear, legally sound set of rules so that they can develop most of AI with very limited regulation,” says Benifei. 

Organizations that don’t comply face fines of up to €30 million ($31 million) or, for companies, up to 6% of total worldwide annual revenue. And experience shows that Europe is not afraid to dish out fines to tech companies. Amazon was fined €746 million ($775 million) in 2021 for breaching the GDPR, and Google was fined €4.3 billion ($4.5 billion) in 2018 for breaching the bloc’s antitrust laws. 

When will it come into effect? 

It will be at least another year before a final text is set in stone, and a couple more years before businesses will have to comply. There is a chance that hammering out the details of such a comprehensive bill with so many contentious elements could drag on for much longer. The GDPR took more than four years to negotiate, and it was six years before it entered into force. In the world of EU lawmaking, anything is possible.

Article link: https://www.technologyreview.com/2022/05/13/1052223/guide-ai-act-europe/
Why the USAF’s IT chief is ‘bullish’ on open source – FCW

Posted by timmreardon on 05/12/2022
Posted in: Uncategorized. Leave a comment

By LAUREN C. WILLIAMSMAY 11, 2022 06:03 PM ET

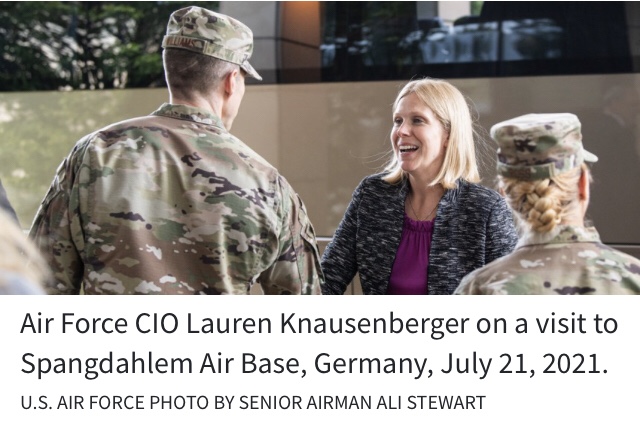
While there’s no such thing as completely secure software, open source can make it stronger through the “power of the crowd,” said Lauren Knausenberger, the Air Force’s chief information officer.

The future of warfare could depend on the Defense Department’s ability to update weapons or communications systems with a software patch, and embracing open source software could help make that a reality. 

That was a key point Lauren Knausenberger, the Air Force’s chief information officer, stressed Wednesday when testifying about the benefits of open source software. 

“It is entirely possible that a future conflict to preserve our way of life is decided by features, fixes, and updates to software intensive systems that must take place in minutes or hours. And this means that we must learn quickly as a department and leverage the knowledge and best practices of the entire development community,” Knausenberger told the House Committee on Science, Space, and Technology Subcommittees on Investigations and Oversight And Subcommittee on Research and Technology on May 11.

While there’s no such thing as completely secure software, open source makes it stronger through the “power of the crowd,” Knausenberger said.

“The same concerns are there whether it’s commercial software or open source. But if it’s open source software, you have the power of the crowd looking at it and then you can also run your own tests internally because it is open code…you can redo the work yourself if you so choose,” she said. 

Knausenberger prefaced her testimony on May 11, saying she was “bullish” on open source technology and noted that fewer eyes on commercial software’s source code could mean significant cybersecurity breaches go undetected for longer periods of time. 

“With commercial software, you can’t see the source code. You do have situations where like with SolarWinds, you could have a sophisticated adversary come in, inject malware, and have it be months before anyone knows that there’s a problem,” the tech chief said. 

“Whereas in the open source community we’ve seen with a number of examples that we just catch it faster, we can push it faster, we have more people trying to fix it faster and spread the word. Whereas the commercial side, you have some really smart companies working on it, but we might not know about it as soon.”

Brian Behlendorf, the general manager for the Open Source Security Foundation, a Linux Foundation project, testified that the open source community previously had a “buyer beware” reputation when it came to software security. And while things have changed culturally, resources will be needed to ensure proper oversight. 

“Culturally speaking, there’s a greater emphasis on security in the open source software community. There used to be very much a perspective of caveat emptor: I’m just throwing this out there anyone who wants it is welcome to it, but buyer beware and let us know if you find any bugs,” Behlendorf said. 

Now, he said, open source foundations formalize structured security or incident response teams  for projects, sometimes using paid part-time or full-time security researchers dedicated to improving the underlying code, or utilize third-party audits before a product release. 

“So it gives me a lot of hope. But there also is a very long tail that is getting longer and longer of very, very small components that … aggregated together create interesting things, but [are] where there’s perhaps less oversight.”

Behlendorf said there often aren’t enough “eyeballs” on open source projects, even the ones that are highly relied on, “so one thing we’re really trying to do is just make sure that we find the pieces that are critical, find the ones that are under-resourced then where we can direct resources of whatever form are required to increase the level of trust that we might have in that component.” 

While it’s been discussed (if not urged) for many years, the Defense Department has been more vocal recently about embracing open source software. In January, DOD chief information officer John Sherman issued guidance on how to use open source software and the department’s security concerns, including the potential to create “a path for adversaries to introduce malicious code into DoD systems” alongside the “imprudent sharing of code developed for DOD systems.”

During her testimony, Knasuenberger said vulnerabilities are a fact of life in software design.

“If there are no bugs found in a particular piece of software, it’s because no one’s looking,” she said. “It’s not because it’s perfect.”

Article link: https://fcw.com/security/2022/05/why-usafs-it-chief-bullish-open-source/366836/

US Signs on to New Electronic Evidence Protocol in International Cybercrime Agreement – Nextgov

Posted by timmreardon on 05/12/2022
Posted in: Uncategorized. Leave a comment

By MARIAM BAKSHMAY 12, 2022 02:04 PM ET

The new protocol is officially being added to the Budapest Convention—an arrangement between 66 member-states—after four years of negotiations.

The United States has signed onto a new protocol under the first international treaty on the prevention of cybercrime that would, among other things, allow law enforcement to seek information directly from service providers with access to electronic evidence that can be used to catch criminals. 

The new protocol is “specifically designed to help law enforcement authorities obtain access to such electronic evidence, with new tools including direct cooperation with service providers and registrars, expedited means to obtain subscriber information and traffic data associated with criminal activity, and expedited cooperation in obtaining stored computer data in emergencies,” reads a press release from the Justice Department Thursday. “All these tools are subject to a system of human rights and rule of law safeguards.”

Representatives are signing onto the “second additional protocol” to the convention Thursday at the Council of Europe, amid an international conference on enhanced cooperation and disclosure of electronic evidence in Strasbourg, France. According to the press release, officials from the U.S. departments of Justice and State spent almost four years negotiating the addition to the convention, which was adopted back in November, 2021.

“The Budapest Convention is a truly remarkable international instrument. Its technology-neutral approach to cybercrime has created an enduring framework for cooperation that ensures law enforcement has the tools they need to respond to new criminal methods,” said Deputy Assistant Attorney General Richard Downing, who signed the agreement on behalf of the U.S. government. “It is our collective vision that every country that is serious about fighting cybercrime and that provides for the protection of human rights should become party to the Budapest Convention. The Convention strikes the right balance between imposing obligations on nations to have robust laws and capabilities and providing the flexibility necessary for nations with different legal systems to join.”

China and Russia, are notably not signed on to the Budapest Convention. The Justice Department release noted that the State Department’s Bureau of International Narcotics and Law Enforcement Affairs majorly funds the Council of Europe Cybercrime Program to increase the ranks of the treaty’s member countries.

The Budapest Convention was established in 2001. The first additional protocol added to the treaty concerned “the criminalisation of acts of a racist and xenophobic nature committed through computer systems.” 

“As cybercrime proliferates, electronic evidence is increasingly stored in different jurisdictions,” Justice said. “The United States remains committed to the Budapest Convention as the premier international legal instrument for fighting cybercrime.”

Article link: https://www.nextgov.com/cybersecurity/2022/05/us-signs-new-electronic-evidence-protocol-international-cybercrime-agreement/366874/

Kubernetes Adopts Sigstore for Supply Chain Security – TheNewStack

Posted by timmreardon on 05/12/2022
Posted in: Uncategorized. Leave a comment

6 May 2022 10:39am, by Steven J. Vaughan-Nichols

With the release of Kubernetes 1.24 on May 4, for the first time, over five million Kubernetes developers can verify that the distributions they’re using are what they claim to be. That’s because with this release Kubernetes is adopting Sigstore for signing artifacts and verifying signatures. This is a major move forward for Kubernetes security.

As we all know, container supply chain security has become a critical issue. All too often software components are poisoned, and every program built on them wither and die with them. Introduced last year, Sigstore is a free software signing service. It improves software supply chain security by making it easy to cryptographically sign release files, container images, and binaries. Once signed, the signing record is kept in a tamper-proof public log. The sigstore will be free to use by all developers and software providers. This gives software artifacts a safer chain of custody that can be secured and traced back to their source.

A Huge Step

One reason this is such a big deal, Tracy Miranda, developer security company Chainguard‘s head of open source, explained is that it’s “a huge step in protecting the integrity of the Kubernetes ecosystem and demonstrates that code signing at an enormous scale is possible and frankly necessary due to the increase in supply chain attacks.”

It’s the ease of use that’s important here. We’ve long known that it was good security to cryptographically sign and verify programming elements, but most earlier cryptographic signature tools have either been too cumbersome or too confusing to use. Without easy-to-use tools to digitally sign their code, few developers are going to bother. That’s where Sigstore came in.

As Bob Callaway, a Google Staff Software Engineer and Sigstore project founder, said “We built Sigstore to be easy, free, and seamless so that it would be massively adopted and protect us all from supply chain attacks. Kubernetes’ choice to use Sigstore is a testament to that work.”

SLSA Compliance

The Kubernetes release team saw the importance of this effort. In early 2021, the crew began exploring Supply chain Levels for Software Artifacts, (SLSA, pronounced salsa) compliance to improve Kubernetes software supply chain security. SLSA is a security framework that includes a checklist of standards and controls to prevent tampering, improve the integrity, and secure the packages and infrastructure of your projects. Sigstore was a key project in achieving SLSA level 2 status and getting a head start towards achieving SLSA level 3 compliance, which the Kubernetes community expects to reach this August.

Sigstore Benefits

Sigstore also delivers a variety of benefits to the Kubernetes community, including:

  • Sigstore’s keyless signing gives a great developer experience and removes the need for painful key management.
  • Sigstore’s public transparency log (Rekor) and APIs mean Kubernetes consumers may easily verify signed artifacts.
  • Sigstore’s use of standards, such as support for any Open Container Initiative (OCI) artifact (including containers, Helm Charts, configuration files, and policy bundles) and OpenID Connect (OIDC), meant it could integrate seamlessly with other tools and services.
  • The active, open source, vendor-neutral Sigstore community gives confidence that the project will be rapidly adopted and become a de-facto industry standard.

“Security is a never-ending journey, but each step delivered to decrease attackers’ ability to undermine the integrity of our supply chains is an important one,” said Tim Pepper, VMware’s Head of Open Source Technology Center and Kubernetes Steering Committee. Sigstore’s adoption by Kubernetes in its next release is a big step forward.

Article link: https://thenewstack.io/kubernetes-adopts-sigstore-for-supply-chain-security/

Featured image by Steve Buissinne from Pixabay

Planning Doesn’t Have to Be the Enemy of Agile – HBR

Posted by timmreardon on 05/10/2022
Posted in: Uncategorized. Leave a comment

by Alessandro Di Fiore

September 13, 2018

Summary. Planning was one of the cornerstones of management, but it’s now fallen out of fashion. It seems rigid, bureaucratic, and ill-suited to a volatile, unpredictable world. However, organizations still need some form of planning. And so, universally valuable, but desperately unfashionable, planning waits like a spinster in a Jane Austen novel for someone to recognize her worth. The answer is agile planning, a process that can coordinate and align with today’s agile-based teams. Agile planning also helps to resolve the tension between traditional planning’s focus on hard numbers, and the need for “soft data,” or human judgment.

Planning has long been one of the cornerstones of management. Early in the twentieth century Henri Fayol identified the job of managers as to plan, organize, command, coordinate, and control. The capacity and willingness of managers to plan developed throughout the century. Management by Objectives (MBO) became the height of corporate fashion in the late 1950s. The world appeared predictable. The future could be planned. It seemed sensible, therefore, for executives to identify their objectives. They could then focus on managing in such a way that these objectives were achieved.

This was the capitalist equivalent of the Communist system’s five-year plans. In fact, one management theorist of the 1960s suggested that the best managed organizations in the world were the Standard Oil Company of New Jersey, the Roman Catholic Church and the Communist Party. The belief was that if the future was mapped out, it would happen.

Later, MBO evolved into strategic planning. Corporations developed large corporate units dedicated to it. They were deliberately detached from the day-to-day realities of the business and emphasized formal procedures around numbers. Henry Mintzberg defined strategic planning as “a formalized system for codifying, elaborating and operationalizing the strategies which companies already have.” The fundamental belief was still that the future could largely be predicted.

Now, strategic planning has fallen out of favor. In the face of relentless technological change, disruptive forces in industry after industry, global competition, and so on, planning seems like pointless wishful thinking.

And yet, planning is clearly essential for any company of any size. Look around your own organization. The fact that you have a place to work which is equipped for the job, and you and your colleagues are working on a particular project at a particular time and place, requires some sort of planning. The reality is that plans have to be made about the use of a company’s resources all of the time. Some are short-term, others stretch into an imagined future.

Universally valuable, but desperately unfashionable, planning waits like a spinster in a Jane Austen novel for someone to recognize her worth.

But executives are wary of planning because it feels rigid, slow, and bureaucratic. The Fayol legacy lingers. A 2016 HBR Analytics survey of 385 managers revealed that most executives were frustrated with planning because they believed that speed was important and that plans frequently changed anyway. Why engage in a slow, painful planning exercise when you’re not even going to follow the plan?

The frustrations with current planning practices intersect with another fundamental managerial trend: organizational agility. Reorganizing around small self-managing teams — enhanced by agility methods like Scrum and LeSS — is emerging as the route to the organizational agility required to compete in the fast-changing business reality. One of the key principles underpinning team-based agility is that teams autonomously decide their priorities and where to allocate their own resources.

The logic of centralized long-term strategic planning (done once a year at a fixed time) is the antithesis of an organization redesigned around teams who define their own priorities and resources allocation on a weekly basis.

But if planning and agility are both necessary, organizations have to make them work. They have to create a Venn diagram with planning on one side, agility on the other, and a practical and workable sweet-spot in the middle.  This is why the quest to rethink strategic planning has never been more urgent and critical. Planning twenty-first century style should be reconceived as agile planning.

Agile planning has a number of characteristics:

  • frameworks and tools able to deal with a future that will be different;
  • the ability to cope with more frequent and dynamic changes;
  • the need for quality time to be invested for a true strategic conversation rather than simply being a numbers game;
  • resources and funds are available in a flexible way for emerging opportunities.

The intersection of planning with organizational agility generates two other paramount requirements:

A process able to coordinate and align with agile teams

Agile organizations face the challenge of managing the local autonomy of squads (bottom-up input) consistently with a bigger picture represented by the tribe’s goals and by cross-tribe interdependencies and the strategic priorities of the organization (top-down view). Governing this tension requires new processes and routines for planning and coordination.

Consider the Dutch financial services firm ING Bank. It restructured its operations in the Netherlands by reorganizing 3,500 employees into agile squads. These are autonomous multidisciplinary teams (up to nine people per team) able to define their work and make business decisions quickly and flexibly. Squads are organized into a Tribe (of no more than 150 people), a collection of squads working on related areas.

ING Bank revisited its process and introduced routine meetings and formats to create alignment between and within tribes. Each tribe develops a QBR (Quarterly Business Review), a six-page document outlining tribe-level priorities, objectives and key results.   This is then discussed in a large alignment meeting (labelled the QBR Marketplace) attended by tribe leads and other relevant leaders. At this meeting one fundamental question is addressed: when we add up everything, does this contribute to our company’s strategic goals?

The alignment within a tribe happens at what is called a Portfolio Marketplace event: representatives of each of the squads which make up the tribe come together to agree on how the set goals are going to be achieved and to address opportunities for synergies.

The ING Bank example shows how the planning process is still necessary and essential to an agile company although in a different fashion with different processes, mechanisms and routines.

As more and more companies transform into agile organizations, agile planning will likely become the new normal replacing the traditional centralized planning approach.

A process that makes use of both limitless hard data and human judgment

Planners have traditionally been obsessed with gathering hard data on their industry, markets, competitors. Soft data — networks of contacts, talking with customers, suppliers and employees, using intuition and using the grapevine — have all but been ignored.

From the 1960s onwards, planning was built around analysis.  Now, thanks to Big Data, the ability to generate data is pretty well limitless.  This does not necessarily allow us to create better plans for the future.

Soft data is also vital. “While hard data may inform the intellect, it is largely soft data that generate wisdom. They may be difficult to ‘analyze’, but they are indispensable for synthesis — the key to strategy making,” saysHenry Mintzberg.

Companies need first to imagine possibilities and second, pick the one for which the most compelling argument can be made.  In deciding which is backed by the most compelling argument, they should indeed take into account all data that can be crunched. But in addition, they should use qualitative judgment.

In an agile organization, teams use design thinking and other exploratory techniques (plus data) to make rapid decisions and change the course on a weekly basis. Decision making is done by a team of people, offsetting in this way the potential biases of a single person making a decision based on her individual judgement. To some extent, an agile team-based organization enables the possibility to leverage qualitative data and judgement — combined today with infinite hard data — for better decisions.

Relying solely on hard data has unquestionably killed many potential great businesses. Take Nespresso, the coffee pod pioneer developed by Nestle.  Nespresso took off when it stopped targeting offices and started marketing itself to households. There was little data on how households would respond to the concept and whatever information was available suggested a perceived consumer value of just 25 Swiss centimes versus a company-wide threshold requirement of 40 centimes. The Nespresso team had to interpret the data skillfully to present a better case to top management. Because it believed strongly in the idea, it forced the company to take a bigger-than-usual risk. If Nestle had been guided solely by quantitative market research the concept would never have gotten off the ground.

The traditional planning approach needs to be revisited to better serve the purposes of the agile enterprise of the twenty-first century. Agile planning is the future of planning. This new approach will require two fundamental elements. First, replacing the traditional obsessions on hard data and playing the numbers-game with a more balanced co-existence of hard and soft data where judgment also plays an important role. Second, introducing new mechanisms and routines to ensure alignment between the hundreds of self-organizing autonomous local teams and the overarching goals and directions of the company.

Article link: https://hbr.org/2018/09/planning-doesnt-have-to-be-the-enemy-of-agile?

Alessandro Di Fiore is the founder and CEO of the European Centre for Strategic Innovation (ECSI) and ECSI Consulting. He is based in Boston and Milan. He can be reached at adifiore@ecsi-consulting.com. Follow him on twitter @alexdifiore.

What You Need to Know Before Contracting with the Federal Government – National Law Review

Posted by timmreardon on 05/09/2022
Posted in: Uncategorized. Leave a comment

By Jeffrey M. Stefan II and M. Alexander Monahan of Varnum LLP

May 9, 2022

Making the decision to engage your business in government contracting at the local, state or national level can admittedly be overwhelming, particularly for those new to the process. However, the potential benefits should outweigh the hesitations. According to an American Express OPEN survey, 57 percent of businesses noted their revenue grew significantly because of government contracting, at an average rate of 61 percent. This advisory provides a high-level overview of the process with a focus on federal government contracting, which is far and away the largest source of government contracting.

United States federal government contracting is an enormous business both nationwide and internationally, with total contract spending value in the hundreds of billions annually. In fact, the U.S. government is the single largest procurer of goods and services in the world. While the Department of Defense (DOD) accounts for most of the federal service and product acquisitions, there are myriad industries that are engaged in contracting with the U.S. government, providing products and services that range from paper clips to missile defense systems. Nevertheless, to take part in this seemingly endless source of opportunity, your business will want to make sure it is well prepared prior to embarking.

Complete Regulatory Basics

Any business legitimately (and legally) capable of doing business with the federal government must have a few basic regulatory tasks initially completed. To start, the government requires any potential contractor register its business with Dun & Bradstreet (D&B) and the System for Award Management (SAM). 

The D&B system utilizes a nine-digit unique identifier number to manage a company’s credit profile so lenders and potential customers or business partners can better ascertain a company’s reliability and financial stability.

The SAM is the government’s central registration repository for all businesses, both large and small. However, before a business begins completing the D&B or SAM registrations, a business needs to be aware of its North American Industrial Classification System (NAICS) code. The purpose of the NAICS is to provide the government with a uniform method of classifying its purchases so it can track spending for reporting, funding and budgeting. Prior to tendering a bid or proposal, a prospective contractor must register with the SAM.

Broadly speaking, the SAM will require a contractor to:

  • Register under the company’s Data Universal Numbering System (DUNS) number;
  • List the NAICS Code applicable to the type of work the contractor performs;
  • Complete representations and certifications contained in the Federal Acquisition Regulation (FAR);
  • Identify the contractor’s bank account; and
  • Provide background information regarding the contractor. 

Notably, a company’s information included on the SAM must be updated annually or when previously provided information deviates.

Furthermore, any contracts awarded by the federal government must first be approved by the federal government’s Contracting Officer (CO). A CO will only approve, in its discretion, what it determines to be responsible contractors. Specifically, the government will not enter into a contract with any business that:

  • owes back taxes
  • has a current or pending legal judgment with the government
  • does not have a checking account
  • is on the government’s excluded parties list
  • hasn’t completed the basic regulatory requirements for doing business with the government

Before moving on to the next step, potential contractors will want to ensure they have completed the above-mentioned registrations and completed a self-diagnostic on their business to identify and address any potential hindrances, including those listed above, that may currently exist.

Finding an Opportunity

The process for seeking business from the federal government is largely comparable to the process of obtaining business in the private sector. As in the private sector, marketing a service or product to the government depends on identifying relevant markets and potential government customers suited to your businesses capabilities.

In the realm of federal government contracting, there are numerous sources available to help pinpoint opportunities suited for your business. Below are some of the main portals of entry into federal government contracting opportunities.

GSA Schedule
Obtaining a General Services Administration (GSA) schedule contract is perhaps the most common form of federal government contract. The GSA is the “acquisition arm” of the federal government, playing a key role in connecting the private sector with the relevant federal agency seeking a fulfillment need. Any person/entity interested in selling their products and services to the federal government should prepare by making sure they have satisfied the applicable requirements and registering in the appropriate systems. Any prospective vendor who wishes to be included on a GSA Schedule can find more information here. The primary contract vehicle is the GSA Schedules, or Multiple Award Schedules, program. Additionally, any prospective vendor should develop a sales and marketing strategy for how that vendor will be targeting specific government contracts.

To be eligible for a GSA Schedule contract, a vendor must have been in business for at least two years and be able to provide two years’ worth of financial statements. In this regard, a company must be able to demonstrate it has measurable past performance. If a company does not have previous federal contracting experience, it may use federal and non-federal references from six or more previous customers, in part to obtain a past performance and evaluation Open Ratings report through Dun & Bradstreet.

FedBizOpps
Federal Business Opportunities (FedBizOpps) is a point of entry for business to seek out federal government contracting opportunities with a value of over $25,000.

GWACs
The federal government is a massive purchaser of hardware, software and related services through Governmentwide Acquisition Contracts (GWAC).

Subcontracting
Another way to get involved in federal government contracting, albeit indirectly, is to serve as a subcontractor for a company that has been awarded a government contract (known as the “prime contractor”). Agencies may provide information on their websites about firms to which they have awarded contracts. As an example, the GSA and SBA maintain subcontracting directories and databases. Subnet is another database of subcontracting opportunities. Other potentially useful sources of information include trade and business publications, the SAM website, company websites, and the Federal Procurement Data System (FPDS). Information obtained from these resources might indicate which companies have received, or plan to receive, government contracts.

One note before moving ahead: take the time to thoroughly research a potential contract opportunity and plan your “elevator pitch” and capability statement for said opportunity before making an offer. It will pay off in the long run.

Offering on a Contract

After you have completed the necessary registrations and found an opportunity that fits your business, you are ready to jump into the offer pool. There are two types of offers when it comes to government contracts – bids and proposals. Bids are generally used in sealed bidding purchases, while proposals usually involve contract awards to be made following a negotiation process. Three of the main offer types are briefly described below:

  • Request for Quotation (RFQ): An RFQ is generally used for proposed contracts with a value of less than $150,000. The benefit is that this method is usually relatively simple and focuses mainly on price and delivery capabilities.
  • Request for Proposal (RFP): Typically for acquisitions sought with larger values than an RFQ, a potential contractor will be required to provide additional details about how they would be able to complete a specific project or develop a specific product.
  • Invitation for Bid (IFB): In a similar vein to an RFP, an IFB is generally used for projects with a value of over $100,000. Potential contractors submit a sealed solicitation/bid for government procurement. This process typically does not involve any outside negotiation between a potential contractor and the government vendor seeking the acquisition.

It is crucial that the information provided in an offer (whether it is for an RFQ, RFP, IFB, or otherwise) is factually sound and inclusive of any pertinent material a CO would need to make its evaluation. A company will want to provide as much information as possible without overwhelming the CO. However, make sure not to overpromise on any proposal, particularly related to technical specifications (if required), as this will become part of the contract in the event your proposal is selected.

Submit an Offer

Once you have identified an opportunity, double-checked everything included in your bid and/or proposal and have satisfied all the rules for the submission process, you are ready to submit your offer. As a parting word of advice, do not make the mistake of assuming offering the lowest price is the key to winning a government contract. A company’s experience and history of providing excellent service in its respected field is as important, if not more important, than the actual offer value.

The evaluation and award process begin when a government procurer receives bids/offers. This process can vary greatly regarding timing (often between 30 and 120 days) and ultimate acceptance of a bid. Stay patient, be prepared to provide any necessary follow-up information, keep in regular contact with the assigned CO (without being too pushy), and continue to set your business up for success should your offer be accepted.

The information provided in this advisory is a starting point to prepare your business for contracting with the federal government.

Article link: https://www-natlawreview-com.cdn.ampproject.org/c/s/www.natlawreview.com/article/what-you-need-to-know-contracting-federal-government?

© 2022 Varnum LLP

National Law Review, Volume XII, Number 129

A Study of More Than 250 Platforms Reveals Why Most Fail – HBR

Posted by timmreardon on 05/09/2022
Posted in: Uncategorized. Leave a comment

by David B. Yoffie, Annabelle Gawer, Michael A. Cusumano

Summary.   

May 29, 2019

Platforms have become one of the most important business models of the 21st century. The problem is that platforms fail at an alarming rate. By identifying the sources of failure, managers can avoid the obvious mistakes. To understand why and how platforms fail, we tried to identify as many failed American platforms as possible over the last twenty years that competed with the 43 successful platforms. The 209 failures allowed us to extract some general lessons about why platforms struggle. In general, platforms fail for four reasons: (1) mispricing on one side of the market, (2) failure to develop trust with users and partners, (3) prematurely dismissing the competition, and (4) entering too late.

Platforms have become one of the most important business models of the 21st century. In our newly-published book, we divide all platforms into two types: Innovation platforms enable third-party firms to add complementary products and services to a core product or technology. Prominent examples include Google Android and Apple iPhone operating systems as well as Amazon Web Services. The other type, transaction platforms, enable the exchange of information, goods, or services. Examples include Amazon Marketplace, Airbnb, or Uber.

Five of the six most valuable firms in the world are built around these types of platforms.  In our analysis of data going back 20 years, we also identified 43 publicly-listed platform companies in the Forbes Global 2000. These platforms generated the same level of annual revenues (about $4.5 billion) as their non-platform counterparts, but used half the number of employees. They also had twice the operating profits and much higher market values and growth rates.

However, creating a successful platform business is not so easy. What we call “platformania” has resembled a land grab, where companies feel they have to be the first mover to secure a new territory, exploit network effects, and raise barriers to entry.  Uber’s frenetic efforts to conquer every city in the world and Airbnb’s desire to enable room sharing on a global scale are the two most obvious recent examples.

The problem is that platforms fail at an alarming rate.  By identifying the sources of failure, managers can avoid the obvious mistakes.

To understand why and how platforms fail, we tried to identify as many failed American platforms as possible over the last twenty years that competed with the 43 successful platforms. The 209 failures allowed us to extract some general lessons about why platforms struggle.

The average life of the failed platforms is only 4.9 years. Many gig economy platforms collapsed within 2-3 years because they did not have enough users or funding. Given the need for deep pockets, it should not be surprising that standalone firms tended to have shorter lives than those that were acquired or launched as part of a larger firm or consortium of firms.  Standalone firms had an average duration of only 3.7 years. Acquired firms, which generally had stronger balance sheets, were capable of fighting longer (averaged 7.4 years), while firms that were part of larger entities were just average in length of survival.

We grouped the most common mistakes into four categories: (1) mispricing on one side of the market, (2) failure to develop trust with users and partners, (3) prematurely dismissing the competition, and (4) entering too late.

Researchers have extensively studied pricing decisions, yet managers still get them wrong. A platform often requires underwriting one side of the market to encourage the other side to participate.  But knowing which side should get charged and which side should get subsidized may be the single most important strategic decision for any platform.

Firms may have to throw commonsense pricing out the window when two or more platforms are racing to create a network effect. For example, Sidecar pioneered the peer-to-peer ridesharing model before Uber and Lyft, but it never became a household name. It deliberately pursued innovation and a conservative slow-growth strategy in order to be financially responsible. The fatal flaw was not recognizing the importance of attracting both sides of the platform.  Sidecar also raised much less venture capital than Uber and Lyft, and was unable to attract enough drivers and riders to survive much beyond the startup phase. Of course, Uber and Lyft have lost billions of dollars and, even though both have now gone public, they may never generate a profit or survive as viable businesses.

Getting the price right is necessary in any platform, though it is not sufficient for success. Platforms also require two or more parties, who may or may not know each other, to connect. Therefore, building trust is essential; this is typically done through rating systems, payment mechanisms, or insurance. In the absence of trust, the players on the platform have to make a leap of faith.  One of the biggest failures in this category was eBay in China. eBay was the first mover, with a dominant share in China in the early 2000s. But Alibaba took over the market. The biggest source of the failure, confided the CEO of eBay China in an interview, was that “eBay’s single biggest problem… was trust.” eBay relied on PayPal, which was designed as a payment system, much like a bank.  For Chinese consumers unfamiliar with ecommerce, that was not enough.  Alibaba’s Alipay used an escrow model (which did not release payment until the consumer was satisfied).  This neutralized eBay’s early mover advantage, and Alibaba quickly captured the bulk of the market.

A common misconception about platforms is that once the market tips in your favor, you will be the long-run winner.  Often this is true. But there is a better way to think about tipped markets:  it is the winner’s opportunity to lose.  Hubris, along with overconfidence and arrogance, to name a few misdirected traits, can produce spectacular failures. For example, browsers were a classic innovation platform: web masters had to optimize their websites to exploit key features in a browser. When Microsoft’s Internet Explorer captured close to 95% of the market by 2004, pundits proclaimed the browser wars were over, the market had tipped, and Microsoft had won. It would require a monumental screw up for Microsoft to lose, but this is exactly what happened. It took Microsoft almost a decade to lose its leading position: extremely poor product execution between 2004 and 2008 enabled the emergence of Firefox; and then inferior product innovation between 2008 and 2015 opened the door to Google’s Chrome.

Perhaps the most classic platform mistake is mistiming the market. The smartphone market illustrates how great products plus all the resources in the world can still lead to failure when entry is too late. Here again, Microsoft was the poster child for failure. Despite billions and billions of dollars of investments over a decade, Microsoft’s Windows phone died. Entering the business five years after Apple, and three years after Google, meant that Microsoft missed the platform window and never recovered.

Here are the key takeaways from our research into why platforms fail:

First, since many things can go wrong in a platform market, managers and entrepreneurs need to make concerted efforts to learn from failures.  Despite the huge upside opportunities that platforms offered, pursuing a platform strategy does not necessarily improve the odds of success as a business.

Second, since platforms are ultimately driven by network effects, getting the prices right and identifying which sides to subsidize remain the biggest challenges. Uber’s great insight (and Sidecar’s great failure) was recognizing the power of network effects to drive volume by dramatically lowering prices and costs on both sides of the market. While Uber is still struggling to make the economics work (and it may yet fail as a business), Google, Facebook, eBay, Amazon, Alibaba, Tencent, and many other platforms started by aggressively subsidizing at least one side of the market and made the transition to high profits.

Third, it is important to put trust front and center. Asking customers or suppliers to take a leap of faith, without history and without prior connections to the other side of a market, is usually asking too much of any platform business. eBay’s failure to establish mechanisms for building trust in China, like Alibaba did with Taobao, is an error that platform managers can and should avoid.

Fourth, although it may sound obvious, timing is crucial. Being early is preferable, but no guarantee of success: remember Sidecar. Being late can be deadly. Microsoft’s catastrophic delay in building a competitor to iOS and Android is a case in point.

Finally, hubris can lead to disaster. Dismissing the competition, even when you have a formidable lead, is inexcusable. If you cannot stay competitive, no market position is safe. Microsoft’s terrible execution with Internet Explorer is an obvious example.

Article link: https://hbr.org/2019/05/a-study-of-more-than-250-platforms-reveals-why-most-fail

David B. Yoffie is the Max and Doris Starr Professor of International Business Administration at Harvard Business School. He is co-author of The Business of Platforms: Strategy in the Age of Digital Competition, Innovation and Power (2019).

Annabelle Gawer is chaired professor in digital economy and the director of the Centre of Digital Economy at the University of Surrey, UK. She is co-author of The Business of Platforms: Strategy in the Age of Digital Competition, Innovation and Power (2019).

Michael A. Cusumano is the Sloan Distinguished Professor of Management at the MIT Sloan School of Management in Cambridge. He is co-author of The Business of Platforms: Strategy in the Age of Digital Competition, Innovation and Power (2019).

How Apple, Google, and Microsoft will kill passwords and phishing in one stroke – ARS Technia

Posted by timmreardon on 05/08/2022
Posted in: Uncategorized. Leave a comment

Dan Goodin 05/6/2022 2:33 pm

For more than a decade, we’ve been promised that a world without passwords is just around the corner, and yet year after year, this security nirvana proves out of reach. Now, for the first time, a workable form of passwordless authentication is about to become available to the masses in the form of a standard adopted by Apple, Google, and Microsoft that allows for cross-platform and cross-service passkeys.

Password-killing schemes pushed in the past suffered from a host of problems. A key shortcoming was the lack of a viable recovery mechanism when someone lost control of phone numbers or physical tokens and phones tied to an account. Another limitation was that most solutions ultimately failed to be, in fact, truly passwordless. Instead, they gave users options to log in with a face scan or fingerprint, but these systems ultimately fell back on a password, and that meant that phishing, password reuse, and forgotten passcodes—all the reasons we hated passwords to begin with—didn’t go away.

A new approach

What’s different this time is that Apple, Google, and Microsoft all seem to be on board with the same well-defined solution. Not only that, but the solution is easier than ever for users, and it’s less costly for big services like Github and Facebook to roll out. It has also been painstakingly devised and peer-reviewed by experts in authentication and security.

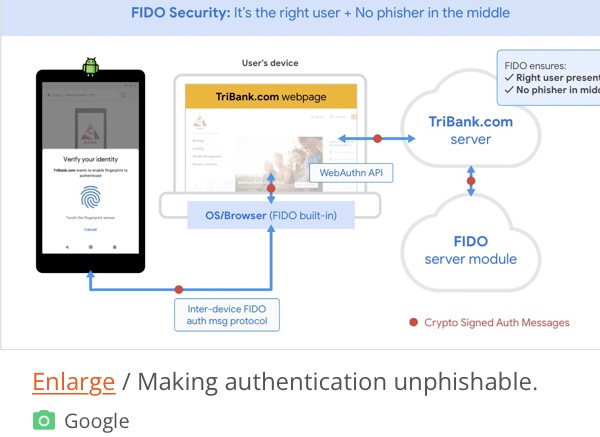
The current multifactor authentication (MFA) methods have made important strides over the past five years. Google, for instance, allows me to download an iOS or Android app that I use as a second factor when logging in to my Google account from a new device. Based on CTAP—short for client to authenticator protocol—this system uses Bluetooth to ensure that the phone is in proximity to the new device and that the new device is, in fact, connected to Google and not a site masquerading as Google. That means it’s unphishable. The standard ensures that the cryptographic secret stored on the phone can’t be extracted.

Google also provides an Advanced Protection Program that requires physical keys in the form of standalone dongles or end-user phones to authenticate logins from new devices.

The big limitation right now is that MFA and passwordless authentication get rolled out differently—if at all—by each service provider. Some providers, like most banks and financial services, still send one-time passwords through SMS or email. Recognizing that those aren’t secure means for transporting security-sensitive secrets, many services have moved on to a method known as TOTP—short for time-based one-time password—to allow the addition of a second factor, which effectively augments the password with the “something I have” factor.

Physical security keys, TOTPs, and to a lesser extent two-factor authentication through SMS and email represent an important step forward, but there remain three key limitations. First, TOTPs generated through authenticator apps and sent by text or email are phishable, the same way regular passwords are. Second, each service has its own closed MFA platform. That means that even when using unphishable forms of MFA—such as standalone physical keys or phone-based keys—a user needs a separate key for Google, Microsoft, and every other Internet property. To make matters worse, each OS platform has differing mechanisms for implementing MFA.

These problems give way to a third one: the sheer unusability for most end users and the nontrivial cost and complexity each service faces when trying to offer MFA.

Taming the MFA beast

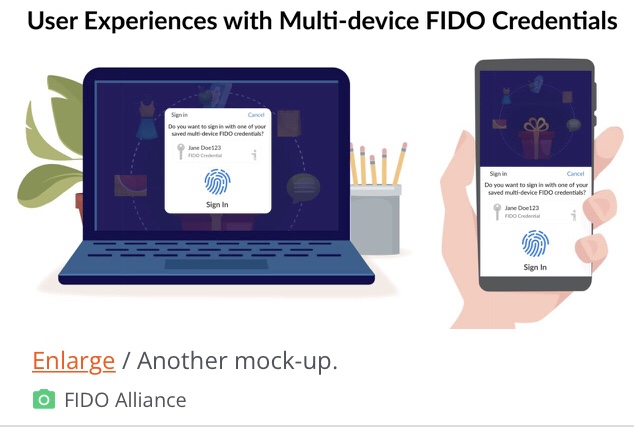
The program that Apple, Google, and Microsoft are rolling out will finally organize the current disarray of MFA services in some significant ways. Once it’s fully implemented, I’ll be able to use my iPhone to store a single token that will authenticate me on any of those three companies’ services (and, one expects, many more follow-on services). The same credential can also be stored on a device running Android or Windows.

By presenting a facial scan or fingerprint to the device, I’ll be able to log in without having to type a password, which is faster and much more convenient. Equally important, the credential can be stored online so that it’s available when I replace or lose my current phone, solving another problem that has plagued some MFA users—the risk of being locked out of accounts when phones are lost or stolen. The recovery processes works by using an already authenticated device to download the credential, with no password required.

“That’s really the whole point here—there’s no recovery process as the private key is immediately available across a user’s devices,” Andrew Shikiar, executive director of the FIDO Alliance, wrote in an email. “They just need to verify themselves to their device to log into their previously enrolled accounts.”

He added: “If the question is about device cloud recovery (e.g., how do I get back into my iCloud account?)—that is something that is managed by each platform provider, all of whom have highly secure methods to ensure that recovery is possible for authentic users.”

Besides giving end users a much more usable process for logging in, the program also offers robust security protections that go beyond what’s available from most online services today.

“While any MFA is better than no MFA, only FIDO authentication is phishing-resistant and is the MFA gold standard,” Bob Lord, a senior technical advisor in the Cybersecurity Division at the Cybersecurity and Infrastructure Security Agency, told me. Previously, Lord was the chief security officer for the Democratic National Committee and chief information security officer at Yahoo. “We finally have a cryptographically strong MFA that is based on open standards and is built into the browsers and phones we already use. That drives costs down and reduces complexity for organizations that want to remove credential theft from the attacker’s toolkit.”

The linchpin to this scheme is something called “multi-device credentials” or, more colloquially, “passkeys,” introduced in updates to the existing FIDO, WebAuthn, and CTAP standards for authentication. As the name suggests, the credential works across all devices, whether you’re running iOS, Android, or Windows, and across all Apple, Google, or Microsoft services.

To make passkey authentications immune to phishing and other common forms of credential theft, the phone or other device storing the credential must be in proximity to the device the user is using to log in. A Bluetooth connection allows the two devices to exchange information that ensures the device logging in is near the end user rather than a remote threat actor. It also allows the authenticating device to ensure that the machine logging in is connected to the legitimate URL rather than an imposter attempting to gain unauthorized access.

So even if a remote attacker attempts to log in, account owners will be unable to use their passkeys to authenticate the transaction. Since the phone or other authenticating device must be physically close to a user’s computer before it will display a “do you want to login” dialog, a phisher in another city, state, or country can’t initiate a login and perform a technique known as MFA prompt bombing.

Lord and other security experts say that passkeys also eliminate the need to enter a password without degrading security assurances provided by most current forms of MFA. Most MFA has consisted of a password and a security token—that is, something I know and something I have. The new system provides another, easier form of MFA—specifically, something I have (my phone) and something I am (my fingerprint or face scan).

In an email, Andrew Shikiar, executive director of the FIDO Alliance, said that he expects rollouts to start by the end of this year and early into the next year.

“Each platform provider has their own timelines for initial deployment over the coming year,” he wrote. Once all three services have fully implemented the system, “users will be able to leverage the ‘passkey’ functionality for passwordless logins across devices on a device platform and also can bootstrap from one platform to another that also has support. This latter action is done via a local Bluetooth pairing in a new protocol being built into the FIDO specs.”

The FIDO Alliance, Google, and Microsoft have more details here, here, and here.

Given the decade of empty promises announcing the demise of the password, people have good reason to greet this week’s announcement with skepticism. It won’t be a done deal until all the pieces are in place and passkeys are rolled out on a mass scale. That said, with the support of Google, Microsoft, and especially Apple—a company famous for its “not invented here” bias—we’re for the first time within spitting distance of this key landmark.

Article link: https://arstechnica.com/information-technology/2022/05/how-apple-google-and-microsoft-will-kill-passwords-and-phishing-in-1-stroke/?

This post has been updated to add comment from FIDO explaining how the recovery process works.

New Marine Corps aviation plan makes ‘digital interoperability’ a top priority – Breaking Defense

Posted by timmreardon on 05/08/2022
Posted in: Uncategorized. Leave a comment

By Justin Katz on May 03, 2022 at 4:27 PM

CORRECTION 5/5/2022 at 9:34 a.m. ET: This report has been updated to remove a chart and accompanying text that misidentified information about aircraft production figures.

WASHINGTON: The Marine Corps today published its first aviation plansince 2019, in which it stressed a need to ensure the service’s aviation fleet maintains “digital interoperability” among the Joint Force and foreign partners.

“The future [Marine Air Ground Task Force] is increasingly characterized by its ability to sense, share, and fuse information at tactically relevant speeds with the Joint Force, as well as partners and allies,” reads the document, signed by the service’s top aviator, Lt. Gen. Mark Wise. “Information, and the speed at which it can be shared, is a driving force in the MAGTF’s ability to create tempo in a future operating environment.”

The service’s aviation plan is akin to the Navy’s 30-year shipbuilding plan in that it projects what the Marine Corps envisions the future aviation fleet will look like, what capabilities will be most important and the overall strategic vision laid out by the deputy commandant for aviation. Also similar to the shipbuilding plan, the service has failed to produce the document on a routine basis.

The document’s focus on “digital interoperability,” also referred to as “DI,” echoes the Pentagon’s larger goals for Joint All Domain Command and Control as well as the Navy’s portion of that effort, Project Overmatch.

“The goal of MAGTF DI is to provide the required information to the right participants at the right time, to overcome an adversary, while improving efficiency and effectiveness,” according to the document. “MAGTF DI aims to provide greater situational awareness, accelerate the kill chain, and enhance survivability to outmaneuver and defeat the threat.”

The aviation plan describes the “MAGTF Agile Network Gateway Link,” dubbed MANGL, as the foundation of the service’s efforts to digitally connect its aircraft. The service’s plan uses a “hubs” and “spokes” analogy to describe MANGL.

“Hubs have a comprehensive gateway and spectrum agile radio to handle the message translation and network management of present and future tactical data links (TDL),” according to the document. “Spokes have the same interfaces, but less capable gateways and legacy radios.”

The service anticipates that by fiscal 2024 that every Marine Corps aviation platform will have “a way to transmit and receive multiple standardized links” to meet the service’s missions.

Article link: https://breakingdefense-com.cdn.ampproject.org/c/s/breakingdefense.com/2022/05/new-marine-corps-aviation-plan-makes-digital-interoperability-a-top-priority/amp/

Leaders Focus Too Much on Changing Policies, and Not Enough on Changing Minds – HBR

Posted by timmreardon on 05/07/2022
Posted in: Uncategorized. Leave a comment

by Tony Schwartz

June 25, 2018

Summary.   So why is business transformation so difficult to achieve? One reason is the invisible fears and insecurities that keep us locked into behaviors even when we know rationally that they don’t serve us well. Leaders can change processes, policies, seating arrangements, and other external factors, but until they change people’s internal feelings, assumptions, blind spots, and fears, they’ll struggle to make change stick. This kind of transformation should start with the leaders themselves, since its their personalities that often shape corporate culture. close

Not long ago, I asked 100 CEOs attending a conference how many of them were currently involved in a significant business transformation. Nearly all of them raised their hands, which was no surprise. According to a study by BCG, 85% of companies have undertaken a transformation during the past decade.

The same research found that nearly 75% of those transformations fail to improve business performance, either short-term or long-term.

So why is transformation so difficult to achieve?

Among many potential explanations, one that gets very little attention may be the most fundamental: the invisible fears and insecurities that keep us locked into behaviors even when we know rationally that they don’t serve us well. Add to that the anxiety that nearly all human beings experience in the face of change. Nonetheless, most organizations pay far more attention to strategy and execution than they do to what their people are feeling and thinking when they’re asked to embrace a transformation. Resistance, especially when it is passive, invisible, and unconscious, can derail even the best strategy.

Business transformations are typically built around new structural elements, including policies, processes, facilities, and technology. Some companies also focus on behaviors — defining new practices, training new skills, or asking employees for new deliverables.

What most organizations typically overlook is the internal shift — what people think and feel — which has to occur in order to bring the strategy to life. This is where resistance tends to arise — cognitively in the form of fixed beliefs, deeply held assumptions and blind spots; and emotionally, in the form of the fear and insecurity that change engenders. All of this rolls up into our mindset, which reflects how we see the world, what we believe and how that makes us feel.

The result is that transforming a business also depends on transforming individuals — beginning with the most senior leaders and influencers. Few of them, in our experience, have spent much time observing and understanding their own motivations, challenging their assumptions, or pushing beyond their intellectual and emotional comfort zones. The result is something that the psychologists Lisa Lahey and Robert Kegan have termed “immunity to change.”

We first ran up against the power of mindset two decades ago when we began to make a case inside organizations that rest and renewal are essential for sustaining high performance. The scientific evidence we presented to clients was compelling. Nearly all of them found the concept persuasive and appealing, both logically and intuitively. We taught them very simple strategies to build renewal into their lives, and they left our workshops eager to change the way they worked.

Nonetheless, most of them struggled with changing their behavior when they got back to their jobs. They continued to equate continuous work and long hours with success. Taking time to renew during work days made them feel as if they were slacking. Even when organizations built nap rooms, they often went unused. People worried that if they rested at all, they wouldn’t get their work done, and above all, they feared failing. Despite their best intentions, many of them eventually defaulted back to their habitual patterns.

More recently, we worked with the senior team of a large consumer product company which had been severely disrupted by smaller, more agile online competitors selling their services directly to consumers. On its face, the team was aligned, focused, and committed to a new multi-faceted strategy with a strong digital component. But when we looked at the team’s mindset more deeply, we discovered that they shared several underlying beliefs including, “Everything we do is equally important,” “More is always better,” and “It has to be perfect or we don’t do it.” They summarized these beliefs in a single sentence: “If we don’t keep running as hard as we can, and attend to every detail, everything will fall apart.”

Not surprisingly, the leaders found they were spreading themselves too thin, struggling to pull the trigger on new initiatives, and feeling exhausted. Simply surfacing these costs and their consequences proved highly valuable and motivating. We also launched several initiatives to address these issues individually and collectively.

One of the most successful began with a simple exercise aimed at helping the leaders to define their three highest priorities. Then we took them through a structured exercise including delving into their calendars to assess whether they were using their time to best advantage, including setting aside time for renewal. This process prompted them to examine more consciously why they were working in self-defeating ways.

We also developed an online site where leaders agreed to regularly share their progress on prioritizing, as well as any feelings of resistance that were arising, and how they managed them. Their work is ongoing, but among the most common feelings people reported were liberation and relief. Their worst fears failed to materialize.

Several factors typically hold mindset in place. The first is that much of it gets deeply rooted early in our lives. Over time we tend to develop confirmation bias, forever seeking evidence that reinforces what we already believe, and downplaying or dismissing what doesn’t. We’re also designed, both genetically and instinctively, to put our own safety first, and to avoid taking too much risk. Rather than using our capacity for critical thinking to assess new possibilities, we often co-opt our prefrontal cortex to rationalize choices that were actually driven by our emotions.

All this explains why the most effective transformation begins with what’s going on inside people — and especially the most senior leaders, given their disproportionate authority and influence.  Their challenge is to deliberately turn attention inward in order to begin noticing the fixed patterns in their thinking, how they’re feeing in any given moment, and how quickly the instinct for self-preservation can overwhelm rationality and a longer term perspective, especially when the stakes are high.

Leaders also have an outsize impact on the collective mindset — meaning the organizational culture. As they begin to change the way they think and feel, they’re more able to model new behaviors and communicate to others more authentically and persuasively. Even employees highly resistant to change tend to follow their leaders, simply because most people prefer to fit in, rather than stick out.

Ultimately, personal transformation requires the courage to challenge one’s current comfort zone, and to tolerate that discomfort without overreacting. One of the most effective tools, we’ve found is a series of provocative questions we ask leaders and their teams to build a practice around asking themselves:

“What am I not seeing?

“What else is true?”

“What is my responsibility in this situation?”

“How is my perspective being influenced by my fears?”

Great strategy remains foundational to transformation, but successful execution also requires surfacing and continuously addressing the invisible reasons that people and cultures so often resist changing, even when the way they’re working isn’t working.

Article link: https://hbr.org/2018/06/leaders-focus-too-much-on-changing-policies-and-not-enough-on-changing-minds?

Tony Schwartz is the CEO of The Energy Project and the author of The Way We’re Working Isn’t Working. Become a fan of The Energy Project on Facebook.

Posts navigation

← Older Entries
Newer Entries →
  • Search site

  • Follow healthcarereimagined on WordPress.com
  • Recent Posts

    • By Barring Profits on Basic Coverage, Switzerland Keeps Insurers from Denying Care – Commonwealth Fund 10/19/2026
    • Patients’ Perspectives on AI in Primary Care – Commonwealth Fund 09/11/2026
    • Bitcoin Mining Energy Footprint 08/06/2026
    • Closing the AI Hype Gap 08/05/2026
    • Why Artificial Intelligence is Neither Artificial, Nor Intelligent 07/31/2026
    • Agentic AI, explained 07/05/2026
    • Heeding the pope’s call to ensure AI protects human dignity – MIT Sloan Management 06/01/2026
    • Association between Wealth and Mortality in the United States and Europe – New England Journal of Medicine 05/30/2026
    • U.S. Health Care from a Global Perspective, 2026 – The Commonwealth Fund 05/30/2026
    • Anthropic co-founder Chris Olah’s remarks on Pope Leo XIV’s encyclical “Magnifica humanitas” 05/28/2026
  • Categories

    • Accountable Care Organizations
    • ACOs
    • AHRQ
    • American Board of Internal Medicine
    • Big Data
    • Blue Button
    • Board Certification
    • Cancer Treatment
    • Data Science
    • Digital Services Playbook
    • DoD
    • EHR Interoperability
    • EHR Usability
    • Emergency Medicine
    • FDA
    • FDASIA
    • GAO Reports
    • Genetic Data
    • Genetic Research
    • Genomic Data
    • Global Standards
    • Health Care Costs
    • Health Care Economics
    • Health IT adoption
    • Health Outcomes
    • Healthcare Delivery
    • Healthcare Informatics
    • Healthcare Outcomes
    • Healthcare Security
    • Helathcare Delivery
    • HHS
    • HIPAA
    • ICD-10
    • Innovation
    • Integrated Electronic Health Records
    • IT Acquisition
    • JASONS
    • Lab Report Access
    • Military Health System Reform
    • Mobile Health
    • Mobile Healthcare
    • National Health IT System
    • NSF
    • ONC Reports to Congress
    • Oncology
    • Open Data
    • Patient Centered Medical Home
    • Patient Portals
    • PCMH
    • Precision Medicine
    • Primary Care
    • Public Health
    • Quadruple Aim
    • Quality Measures
    • Rehab Medicine
    • TechFAR Handbook
    • Triple Aim
    • U.S. Air Force Medicine
    • U.S. Army
    • U.S. Army Medicine
    • U.S. Navy Medicine
    • U.S. Surgeon General
    • Uncategorized
    • Value-based Care
    • Veterans Affairs
    • Warrior Transistion Units
    • XPRIZE
  • Archives

    • October 2026 (1)
    • September 2026 (1)
    • August 2026 (2)
    • July 2026 (2)
    • June 2026 (1)
    • May 2026 (12)
    • April 2026 (4)
    • March 2026 (9)
    • February 2026 (6)
    • January 2026 (8)
    • December 2025 (11)
    • November 2025 (9)
    • October 2025 (10)
    • September 2025 (4)
    • August 2025 (7)
    • July 2025 (2)
    • June 2025 (9)
    • May 2025 (4)
    • April 2025 (11)
    • March 2025 (11)
    • February 2025 (10)
    • January 2025 (12)
    • December 2024 (12)
    • November 2024 (7)
    • October 2024 (5)
    • September 2024 (9)
    • August 2024 (10)
    • July 2024 (13)
    • June 2024 (18)
    • May 2024 (10)
    • April 2024 (19)
    • March 2024 (35)
    • February 2024 (23)
    • January 2024 (16)
    • December 2023 (22)
    • November 2023 (38)
    • October 2023 (24)
    • September 2023 (24)
    • August 2023 (34)
    • July 2023 (33)
    • June 2023 (30)
    • May 2023 (35)
    • April 2023 (30)
    • March 2023 (30)
    • February 2023 (15)
    • January 2023 (17)
    • December 2022 (10)
    • November 2022 (7)
    • October 2022 (22)
    • September 2022 (16)
    • August 2022 (33)
    • July 2022 (28)
    • June 2022 (42)
    • May 2022 (53)
    • April 2022 (35)
    • March 2022 (37)
    • February 2022 (21)
    • January 2022 (28)
    • December 2021 (23)
    • November 2021 (12)
    • October 2021 (10)
    • September 2021 (4)
    • August 2021 (4)
    • July 2021 (4)
    • May 2021 (3)
    • April 2021 (1)
    • March 2021 (2)
    • February 2021 (1)
    • January 2021 (4)
    • December 2020 (7)
    • November 2020 (2)
    • October 2020 (4)
    • September 2020 (7)
    • August 2020 (11)
    • July 2020 (3)
    • June 2020 (5)
    • April 2020 (3)
    • March 2020 (1)
    • February 2020 (1)
    • January 2020 (2)
    • December 2019 (2)
    • November 2019 (1)
    • September 2019 (4)
    • August 2019 (3)
    • July 2019 (5)
    • June 2019 (10)
    • May 2019 (8)
    • April 2019 (6)
    • March 2019 (7)
    • February 2019 (17)
    • January 2019 (14)
    • December 2018 (10)
    • November 2018 (20)
    • October 2018 (14)
    • September 2018 (27)
    • August 2018 (19)
    • July 2018 (16)
    • June 2018 (18)
    • May 2018 (28)
    • April 2018 (3)
    • March 2018 (11)
    • February 2018 (5)
    • January 2018 (10)
    • December 2017 (20)
    • November 2017 (30)
    • October 2017 (33)
    • September 2017 (11)
    • August 2017 (13)
    • July 2017 (9)
    • June 2017 (8)
    • May 2017 (9)
    • April 2017 (4)
    • March 2017 (12)
    • December 2016 (3)
    • September 2016 (4)
    • August 2016 (1)
    • July 2016 (7)
    • June 2016 (7)
    • April 2016 (4)
    • March 2016 (7)
    • February 2016 (1)
    • January 2016 (3)
    • November 2015 (3)
    • October 2015 (2)
    • September 2015 (9)
    • August 2015 (6)
    • June 2015 (5)
    • May 2015 (6)
    • April 2015 (3)
    • March 2015 (16)
    • February 2015 (10)
    • January 2015 (16)
    • December 2014 (9)
    • November 2014 (7)
    • October 2014 (21)
    • September 2014 (8)
    • August 2014 (9)
    • July 2014 (7)
    • June 2014 (5)
    • May 2014 (8)
    • April 2014 (19)
    • March 2014 (8)
    • February 2014 (9)
    • January 2014 (31)
    • December 2013 (23)
    • November 2013 (48)
    • October 2013 (25)
  • Tags

    Business Defense Department Department of Veterans Affairs EHealth EHR Electronic health record Food and Drug Administration Health Health informatics Health Information Exchange Health information technology Health system HIE Hospital IBM Mayo Clinic Medicare Medicine Military Health System Patient Patient portal Patient Protection and Affordable Care Act United States United States Department of Defense United States Department of Veterans Affairs
  • Upcoming Events

Blog at WordPress.com.
healthcarereimagined
Blog at WordPress.com.
  • Subscribe Subscribed
    healthcarereimagined
    Join 149 other subscribers

    Have a WordPress.com account? Log in now.

  • healthcarereimagined
    View site in Reader
    Manage subscriptionsSign upLog in
    Report this content
    Collapse this bar
Loading Comments...