BY: GRACE DILLE JUN 7, 2022
The Department of Veterans Affairs (VA) Office of Inspector General (OIG) is calling on the agency to address its slow progress in improving its cybersecurity posture, but the VA said a lack of funding causes the agency to lose high-quality IT personnel.
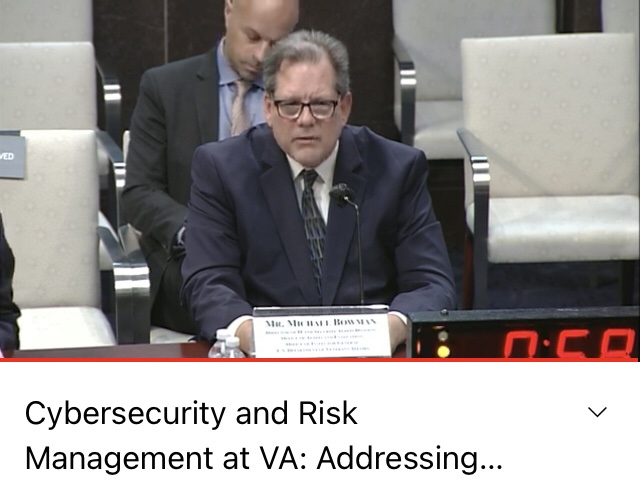
At a House Committee on Veterans’ Affairs Subcommittee on Technology Modernization hearing on June 7, Michael Bowman, director of the IT and security audits division at the VA OIG’s Office of Audits and Evaluations, explained that the VA’s fiscal year (FY) 2021 Federal Information Security Modernization Act (FISMA) audit showed “limited progress.”
The FY2021 audit included 26 of the same recommendations from the FY2020 audit, and 23 of those have been included in every FISMA report dating back to 2018, according to Bowman.
“Our annual FISMA audit and other IG reports demonstrate VA has considerable work in order to achieve better IT security outcomes,” Bowman said during the hearing. “The number of persistent problems, such as weak access controls and deficient configuration management controls, underscores VA’s incremental progress towards improving its security program.”
However, Bowman did note that VA’s remaining FISMA recommendations are “more institutional findings and recommendations,” which he said, “are more difficult to resolve in a year’s time or maybe even five years’ time.” VA has remediated the newer findings quickly, Bowman said, and the institutional ones will “probably remain on the books for several years to come.”
VA’s Cyber Approach, Ongoing Challenges
VA’s new Chief Information Officer Kurt DelBene acknowledged VA can improve in certain areas such as manual processes, as opposed to only focusing on a longer-term approach.
“What I’ve found since I’ve joined the VA is we need to do a better job in terms of the manual processes we do to remediate vulnerabilities,” DelBene said.
“I think we’ve had this view of the long term where there’s automation across everything we do in order to secure the VA – and it turns out because of the complexity we have, that’s absolutely critical – but in the near term, especially with the issues that FISMA, that the OIG has identified, we can use old fashioned shoe leather to really just get involved in the particular systems,” he said.
Lynette Sherrill, VA’s acting chief information security officer echoed DelBene’s shoe leather vision, and said the agency is currently doing a “deep dive” into each of the 26 recommendations to “move these remediations forward on the most critical systems.”
However, at the same time, DelBene noted the VA faces ongoing challenges to improve its cybersecurity posture, such as a lack of funding to recruit and retain high-quality cybersecurity personnel.
“As you know, cybersecurity is an incredibly hot area in industry, and we compete every day with people that can earn higher salaries outside of the Federal government,” DelBene said.
“Just this past couple of weeks, we lost two people that we made offers to at the SES [Senior Executive Service] level, because they went to industry and got higher pay,” he added. “And it’s not small increases in pay – it’s actually substantial differences between what we’re able to pay and what industry will pay people right now.”
One possible solution, DelBene said, is to implement special salary rates for IT specialists. Another, he said, is reimplementing “on-call pay,” when an IT specialist is asked to sacrifice their personal time to be on-call for work.
A strong IT workforce is critical to building a strong cybersecurity posture. While the VA has a mission that energizes many employees, DelBene also said the agency needs Congress’ help to “augment that with pay that’s much more commensurate with where it is in the market.”
Article link: https://www.meritalk.com/articles/va-shows-limited-cyber-progress-calls-for-higher-pay-to-retain-cyber-employees/
By ALEXANDRA KELLEYJUNE 6, 2022
A team of bipartisan lawmakers unveiled new data privacy legislation that stands to finally implement a federal set of regulations to protect Americans’ online information.
Led by Reps. Frank Pallone, D-N.J., and Cathy McMorris Rodgers, R-Wash., as well as Sen. Roger Wicker, R-Miss., the bill, titled the American Data Privacy and Protection Act, has an exhaustive list of definitions that work to give online users power over how their data is accessed and shared by host platforms and third party data brokers.
“This bipartisan and bicameral effort to produce a comprehensive data privacy framework has been years in the making, and the release of this discussion draft represents a critical milestone,” the lawmakers said in prepared remarks. “In the coming weeks, we will be working with our colleagues on both sides of the aisle to build support and finalize this standard to give Americans more control over their personal data. This landmark agreement represents the sum of years of good faith efforts by us, other Members, and numerous stakeholders as we work together to provide American consumers with comprehensive data privacy protections.”
Should the bill become law, it would mandate corporate governing bodies of online platforms that harbor user data, in order to limit such bodies collecting that data and require them to specifically ask permission to access data in digestible language.
It also stipulates targeted advertising should be optional for online users and consumers and expands protections particularly for children and minors.
The Federal Trade Commission would be tasked with enforcing these new privacy requirements.
“This bill strikes a meaningful balance on issues that are critical to moving comprehensive data privacy legislation through Congress, including the development of a uniform, national data privacy framework, the creation of a robust set of consumers’ data privacy rights, and appropriate enforcement mechanisms,” the lawmakers continued. “We believe strongly that this standard represents the best opportunity to pass a federal data privacy law in decades, and we look forward to continuing to work together to get this bill finalized and signed into law soon.”
Taking a page out of the European Union’s playbook, The American Data Privacy and Protection Act would also request the FTC conduct deeper studies on how younger technology start-ups can thrive in the current digital ecosystem.
Dispute data privacy and security being a new frontier for domestic and national security, the U.S. lacks a federal data privacy and protection law. Other lawmakers have previously introduced a bevy of bills aimed at expanding protections for U.S. online consumers to better understand how algorithms track and collect user data to curate content.
Fred BurtonForbes Councils Member
Forbes Technology Council COUNCIL POST| Membership (fee-based)
Jun 7, 2022,09:00am EDT
New York Times best-selling author, former special agent and security expert who helms the Ontic Center for Protective Intelligence.

The war in Ukraine may be the most documented conflict in human history. On social media, we can watch in near real time as military units prepare for battle. A few hours later, we see the aftermath.
Images are being posted and recirculated by an online community of open-source intelligence professionals and enthusiasts. The more analytically rigorous among them may have military, intelligence agency, IT and think tank backgrounds where they learned the skills and abilities that inform their analyses, providing in-depth explanations of battlefield successes and failures to anyone with an internet connection. Information and intelligence that was once available only to governments and intelligence services can now be seen and understood by anyone.
According to the Office of the U.S. Director of National Intelligence, open-source intelligence, also known as OSINT, is defined as “publicly available information appearing in print or electronic form including radio, television, newspapers, journals, the Internet, commercial databases, and videos, graphics, and drawings.” Typically, OSINT doesn’t include any information obtained using clandestine means, making it available to anyone with the ability to uncover it or pay for it.
As a former counter-terrorism agent and executive protection professional, I’ve used open-source intelligence extensively to understand my operating environment and maintain situational awareness, as have protective intelligence teams around the world. But the scope and scale of the OSINT we’re seeing in Ukraine demonstrate how much these capabilities have improved in recent years and how widely available the information has become.
For casual observers not involved in security operations, these developments may mark the first time they’ve seen OSINT used in practice. It demonstrates the incredible value—and risks—of freely available information. But the mainstreaming of OSINT also marks an opportunity for security professionals whose domains have expanded beyond “guns and gates” to include areas like supply chain risk, social unrest, labor shortages, pandemic monitoring and travel security. OSINT’s prevalence in our lives and this wider spread of awareness can make it a topic and bridge to engage colleagues across the organization—and to prove and enhance the value security teams provide businesses.
Here’s how.
First, we have the lightbulb moment. The growing societal awareness of the types of OSINT that are available and their value is an opportunity for a companywide discussion of what data and intelligence the organization might need, the best ways to find that data and how the analysis of that data could be leveraged to help other departments understand and mitigate organizational risk. This is especially true for business functions that focus on specific geographic locations, like logistics, travel security and strategic planning, or those that may deal with specific individuals, like HR, legal and mergers and acquisitions teams. Because the security team is likely already using OSINT as part of their operations, they’re often uniquely placed to understand where the most valuable OSINT can be found, how it can be used and potential pitfalls to avoid.
Second, OSINT can only help your organization if you’re able to identify and integrate the critical insights without getting stuck in information overload. The amount of OSINT available is staggering, but without a plan to analyze and integrate that information, your company will be drinking from a firehose of information. The growing usefulness of OSINT creates an invitation for collaboration between multiple business units to find ways to integrate their data within shared platforms and tools, finding the most useful data in proprietary and open sources to create a more comprehensive picture of the situation. The collaboration between units like HR, risk management, legal and security can decrease resource redundancy while real-time information is made available to the appropriate stakeholders.
Overlaying your internal datasets with OSINT material could yield positive results in many areas. For example, watching the war in Ukraine, it’s not uncommon for online sleuths to match an infrared picture from drone footage posted online to Google Maps data, giving clues about where operations are taking place. In companies, security teams may be able to extract metadata from social media posts to identify the locations of threat actors. In certain situations, this type of information could be integrated into travel and route planning for key executives.
Third, security teams can help the organization understand and communicate the risks and challenges that are present with open-source data. Security teams are often trained to analyze data to spot a wide variety of potential problems in different types of information. For example, information produced by certain outlets may contain biases based on its ownership, which could make their conclusions less reliable. Advanced analysis of images and videos may reveal where or how they were created. It’s not enough to merely find OSINT—the data must be evaluated and analyzed in an attempt to ensure its accuracy and reliability to determine if it’s also actionable.
Security teams are also uniquely placed to help companies understand the risks posed by publicly available corporate information. Employee information available online, either intentionally or accidentally, can be used to concoct social engineering schemes that could be the first step in a cyberattack. Maps of corporate facilities, building plans and photos taken inside facilities could be used to facilitate pre-operational surveillance in preparation for a physical attack. Members of the security team can help the organization see OSINT about the company through the eyes of an attacker and work to create ways to mitigate threats that the OSINT might create.
For some, OSINT is merely a curiosity. Harnessing the value of OSINT for your company and mitigating its risks are complex undertakings, but the mainstreaming of OSINT can provide your organization with a new way of looking at your operations and understanding risks.
Forbes Technology Council is an invitation-only community for world-class CIOs, CTOs and technology executives. Do I qualify?
Ardi Janjeva, Alexander Harris and JoeByrne 7 June 2022
DOWNLOAD PDF(18MB)
Main Image Credit Topographic map concept. Courtesy of cherezoff / Adobe Stock.
This paper explores the use of publicly available information and open source intelligence for national security purposes, and provides recommendations for future policy development.
This joint paper from RUSI and the Alan Turing Institute’s Centre for Emerging Technology and Security aims to establish an independent evidence base to inform future government policy development regarding the use of publicly available information (PAI) and open source intelligence (OSINT) for national security purposes. The findings are based on in-depth consultations with stakeholders from across academia, civil society, commercial organisations, law enforcement and the UK government.
The paper explores the extent to which the increasing proliferation of PAI – and wider accessibility of tools leveraging PAI for OSINT – is changing perceptions of modern intelligence. From this foundation, it asks what the commercial, cultural, policy and technological implications are for UK national security stakeholders.
Article link: https://rusi.org/explore-our-research/publications/occasional-papers/future-open-source-intelligence-uk-national-security
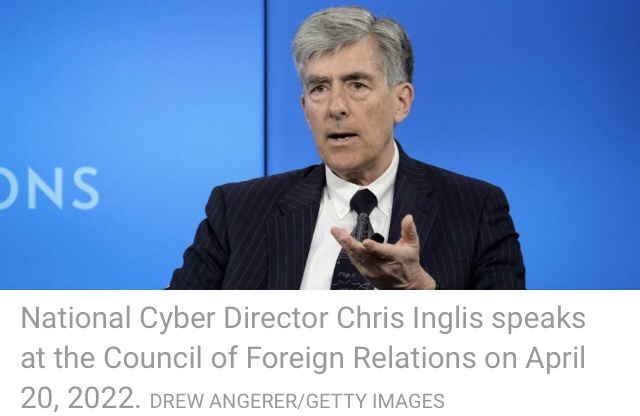
By NATALIE ALMSJUNE 3, 2022
An expert panel is calling on the White House-based Office of the National Cyber Director to steer a governmentwide cybersecurity workforce strategy to address long-standing workforce shortages.
The report, issued Thursday, comes from an offshoot of the congressionally chartered Cyberspace Solarium Commission called CSC 2.0, housed at the nonprofit Foundation for the Defense of Democracies.
It’s a “blueprint to help address the problem,” CSC 2.0 co-chair, Rep.Mike Gallagher (R-Wis.), told FCW.
The panel wants National Cyber Director Chris Inglis to use his position to review agencies’ cyber budgets, revamp hiring mechanisms across the government and potentially even work with Congress to establish expected service authorities for cyber personnel across the government.
“I think we should be concerned about the jobs that have cyber [or] IT in them that go unfilled,” said Inglis, himself a member of the original Solarium Commission, during a Thursday panel discussion held by the Foundation for the Defense of Democracies.
His role, he continued, is making sure that authorities and resources are aligned across the government.
“We have to make sure we first have a strategy that defines what’s missing,” Inglis said. “We then have to make use of all the parts that are already there and connect them to that strategy.”
There are nearly 600,000 cyber job openings nationwide, and for the government alone, there are almost 39,000 job openings, according to the National Institute of Standards and Technology-based CyberSeek.
Currently, the government’s strategy is ad hoc. Federal hiring practices are onerous, and degree and level of experience requirements for jobs often block out entry-level hires. The government’s existing cyber workforce is also less diverse than the rest of the federal workforce.
As with another cyber workforce report issued this year by a different expert panel at the National Academy of Public Administration (NAPA), the latest recommendations call on Inglis to coordinate existing, disparate efforts with new leadership and coordination structures.
One key focus is chronic problems with actually hiring cyber workers into government using antiquated and bulky processes.
“We all know how many jobs we’d like to fill, but there aren’t any vehicles, or many vehicles, that essentially would take that aspiration and meaningfully assist people” to be hired into government jobs, said Inglis, continuing to point to qualification requirements and saying that the government needs to be more flexible and invest in early career hires. “People who show up today at the front door of a government organization with a bachelor of science in computer science, but no experience in hand, typically are turned away,” he said.
The report’s authors recommend various fixes, such as working with the Office of Personnel Management to modernize cybersecurity job codes or expand existing direct hire authorities.
The preference is a third option, though, something report co-author and CSC 2.0 director, Mark Montgomery, called the “Rosetta Stone.”
That recommendation is that Inglis push Congress to authorize governmentwide excepted service authorities for cyber personnel, a category distinct from the competitive service — the majority of rank-and-file feds, governed by particular civil service rules for hiring, firing and pay — or the administrators of the senior executive service.
The report references the Department of Homeland Security’s Cybersecurity Talent Management System, an excepted service system for cyber professionals that launched last fall, but has struggled to scale, only onboarding in a few new hires thus far.
The Department of Defense has similar hiring authorities.
“In essence, this option would take the authorities that underpin CTMS and CES and expand them to the whole of the federal government,” the report states. “This option would maximize the federal government’s flexibility in hiring and managing cyber talent, by creating systems built for the cyber workforce.”
Such a move would likely face opposition, Montgomery said Thursday.
“This will be tough. There will be people who fight this both in Congress and in federal government organizations. And it’s going to cost money, but … no one ever thought fixing federal cybersecurity workforce was going to be a cheap endeavor,” he said. “We really do have to come up with a new hiring mechanism.”
The recent NAPA report also referenced CTMS, saying that it should be evaluated and, if successful, scaled to other agencies.
The CSC 2.0 also pushes Inglis to use his office’s congressional mandate to assess the effectiveness of cyber policies and annual budget proposals from agencies, and the double-hatting of one top official, Chris DeRusha, as the deputy cyber director and federal chief information security officer out of the Office of Management and Budget, to “review and align” agencies’ cybersecurity workforce budgets alongside OMB.
Finally, one of the top challenges is data about the government’s cyber workforce, which is inconsistent and siloed within agencies, said Montgomery.
The NAPA study recommended a cybersecurity data bureau, while this latest report calls for Inglis to focus accountability for existing data mandates and for Congress to extend and amend the law governing data collection on the government’s cyber workers, the Federal Cybersecurity Workforce Assessment Act of 2015.
Article link: https://www.nextgov.com/cybersecurity/2022/06/solarium-successor-wants-white-house-lead-cyber-workforce-strategy/367728/

By MARIAM BAKSHJUNE 6, 2022 04:17 PM ET
It’s time the National Institute of Standards and Technology point to how organizations should be assessing the risk they’re associating with systems when deciding what security controls to implement for their protection, according to the Defense Department.
“Enhance Section 4.0 (Self-Assessing Cybersecurity Risk with the Framework) to integrate guidance on how [Special Publication 800-30, revision 1] can be leveraged to perform the risk measurement to assign a value,” wrote Michele Iversen, director of risk assessment and operational integration at DOD’s chief information office for cybersecurity. “It appears that [the Cybersecurity Framework] depends on measuring, or assessing risk, but [avoids] alignment to the NIST standard commonly used to assess cybersecurity risks.”
Iversen’s comment is in response to a request for information NIST issued toward a second update of the agency’s landmark cybersecurity framework. NIST on Friday released a summary of the comments it’s received—over 130, mostly from industry—since the request in February.
Originally issued in 2014, the Cybersecurity Framework, or CSF, points to various security controls organizations should consider implementing. But the document leaves it up to the user to determine which of those to prioritize, depending on how much risk they’re looking to address, or are willing to accept. And the question of how to measure whether use of the framework was successful was never really answered.
“Further guidance for measuring the performance of an entity in establishing and improving a cybersecurity program was a key need expressed in the RFI responses,” NIST wrote. “As with previous RFIs, comments on drafts, and discussions at NIST forums, metrics and measurement remain a lively topic among respondents. Many recognize that cybersecurity program implementation and improvement are not a pass/fail exercise, and that an effective program must be able to assess, coordinate and report measurable activities. Others stated that such detailed metrics, such as specific control objectives, ‘defeat the broad applicability and flexibility that make the CSF valuable.’”
That tension between the desire for broad applicability and specific guidance is another general challenge for the framework, with groups like BSA | The Software Alliance asking for examples of how federal agencies have used it, as required.
“The level of detail and specificity in the CSF reflects the scalability and flexibility necessary to meet the needs of a wide range of stakeholders—small and large organizations in various sectors,” NIST wrote. “There were more than 500 references in the comments supporting the need for more guidance to support CSF implementation, and many users expressed a desire for greater detail in the CSF while maintaining a non-prescriptive approach. Identifying the proper balance between simplicity and detail in updates to the CSF is a key takeaway that will need further discussion.”
From DOD’s perspective, measurement is “NIST’s core competency” and the agency should be doing more to facilitate whole-of-government risk assessments which also consider the supply chain components of commercial information and communications technology.
“The current practice of departments and agencies developing their own overlays results in variability … The individual department or agency may be operating at low risk to their mission w/o realizing how others may be impacted by the residual risks that they manage,” read the Defense Department comments. “Whole-of-government activities (national security, national commerce, etc.) need a capstone resource to enable integrated risk assessments grounded in the broader/shared uncertainties associated with observation and measurement particularly for their common operating space of ICT, cyber and cyber-security.”
Article link: https://www.nextgov.com/cybersecurity/2022/06/dod-recommends-nist-align-frameworks-cybersecurity-risk-management/367815/
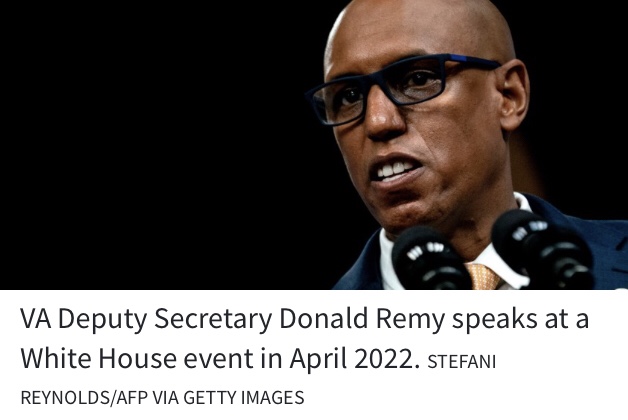
By ADAM MAZMANIANJUNE 3, 2022
The Cerner electronic health records system the Department of Veterans Affairs acquired for $10 billion over 10 years to replace its homegrown Vista software is falling short on data reporting requirements, according to a watchdog report.
The VA’s Office of Inspector General reported on Wednesday that the Mann-Grandstaff Medical Center in Spokane, Washington, the first site to implement the new health record system, isn’t providing metrics needed to support the hospital’s accreditation. A loss in accreditation “may affect patient’s trust in the facility and can also hinder the facility’s ability to recruit quality staff who may prefer to work for an accredited facility,” the report states.
The OIG found that “gaps in available quality and patient safety metrics, more than a year after go-live, hindered publication of quality and patient safety metrics as legislatively required.”
The go-live for the Cerner software at Mann-Grandstaff took place in October 2020. Several oversight reports from VA’s watchdog have identified multiple issues relating to workflows, training, patient safety and more. The project, which is expected to cost at least $21 billion overall, includes a $10 billion contract with Cerner for software, storage and services.
Related articles
VA’s new health record still putting patients at risk
VA plans new health record deployments, despite critical watchdog reports
A Veterans Health Administration official interviewed for the report told the OIG that the agency decided to try to produce reports internally after learning that Cerner would charge $12 million for 50 metrics reports and noted that Cerner did not appear to have the expertise sought by VHA when it came to metrics.
Cerner has “had lots of people leave, lots of buyouts,” the official was quoted as saying in the report. “So sometimes you’ll get somebody that has 20 years. Sometimes you’ll get somebody that just came out of college. We would get stuff when we were validating [metrics reports created by Cerner] that didn’t work right off the bat. Had spelling errors, you know, just simple, simple things.”
Cerner was recently acquired by Oracle for approximately $28.3 billion. Oracle announced on Wednesday that the deal was cleared by U.S. antitrust regulators.
The OIG report included two recommendations for VA Deputy Secretary Donald Remy, whose position includes executive oversight of the Electronic Health Record Modernization program. The report requests that Remy evaluate gaps in metrics and examine issues around the availability of data and taking corrective action as needed. VA agreed with both recommendations and expects to complete the work by October 2022.
In reply comments, Remy noted that many of the problems flagged in the report, which was based on an investigation conducted from July to October 2021, have already been addressed.
Article link: https://fcw.com/it-modernization/2022/06/data-gap-poses-risks-launch-site-vas-new-health-record/367753/

By FRANK KONKELJUNE 3, 2022
Despite tens of billions of dollars in fundingand numerous efforts to improve internet availability across America, millions of Americans still lack broadband internet, according to a new audit from the Government Accountability Office.
Released May 31, the audit posits reasons why the federal government’s broadband efforts haven’t been more successful.
“Federal broadband efforts are fragmented and overlapping, with more than 100 programs administered by 15 agencies,” auditors stated. “Many programs have broadband as their main purpose, and several overlap because they can be used for the purpose of broadband deployment.”
The audit indicates the federal government invested more than $44 billion in broadband from 2015 to 2020. However, the audit makes clear that many efforts are disjointed and suffer programmatic differences. In one example, the National Telecommunications and Information Administration, which is responsible for coordinating telecommunications matters across the executive branch and improving broadband coordination, “did not identify which statutory provisions limit alignment nor recommend any changes” when it led an interagency group that reviewed differing broadband programs in 2018.
“Improved alignment is needed to help address fragmentation and overlap. Without legislative proposals for Congress to consider, agencies may continue to face limitations in aligning programs to close the digital divide,” auditors state.
The auditors also make the case for a new national broadband strategy with “clear roles, goals, objectives and performance measures.”
“In 2021, the Executive Office of the President, through the National Economic Council and in collaboration with other White House offices, took the lead for coordinating broadband programs,” the audit states. “The Executive Office of the President has not decided if a national strategy is needed, but it is well positioned to develop and implement one. A strategy to help better align programs could also include legislative proposals for Congress. Without such a strategy, federal broadband efforts will not be fully coordinated, and thereby continue to risk overlap and duplication of effort.”
GAO issued three recommendations. NTIA agreed with such recommendations to identify statutory limitations to program alignment and develop legislative proposals. The Executive Office of the President did not take a position on GAO’s recommendation to develop a national broadband strategy.
Article link: https://www.nextgov.com/it-modernization/2022/06/gao-federal-broadband-efforts-fragmented-overlapping/367684/