healthcarereimagined

Envisioning healthcare for the 21st century

  • About
  • Economics

How much health insurers pay for almost everything is about to go public – NPR & KHN

Posted by timmreardon on 07/01/2022
Posted in: Uncategorized. Leave a comment

July 1, 20225:00 AM ET

JULIE APPLEBY

The new rules will help people get upfront cost estimates for about 500 so-called “shoppable” services, meaning medical care they can schedule ahead of time DNY59/Getty Images

Consumers, employers and just about everyone else interested in health care prices will soon get an unprecedented look at what insurers pay for care, perhaps helping answer a question that has long dogged those who buy insurance: Are we getting the best deal we can?

Starting July 1, health insurers and self-insured employers must post on websites just about every price they’ve negotiated with providers for health care services, item by item. About the only exclusion is the prices paid for prescription drugs, except those administered in hospitals or doctors’ offices.
KHN logo

This story was produced in partnership with Kaiser Health News.

The federally required data release could affect future prices or even how employers contract for health care. Many will see for the first time how well their insurers are doing compared with others.

The new rules are far broader than those that went into effect last year requiring hospitals to post their negotiated rates for the public to see. Now insurers must post the amounts paid for “every physician in network, every hospital, every surgery center, every nursing facility,” said Jeffrey Leibach, a partner at the consulting firm Guidehouse.

“When you start doing the math, you’re talking trillions of records,” he said. The fines the federal government could impose for noncompliance are also heftier than the penalties that hospitals face.

Federal officials learned from the hospital experience and gave insurers more direction on what was expected, said Leibach. Insurers or self-insured employers could be fined as much as $100 a day for each violation and each affected enrollee if they fail to provide the data.

“Get your calculator out: All of a sudden you are in the millions pretty fast,” Leibach said.

Determined consumers, especially those with high-deductible health plans, may try to dig in right away and use the data to try comparing what they will have to pay at different hospitals, clinics, or doctor offices for specific services.

But each database’s enormous size may mean that most people “will find it very hard to use the data in a nuanced way,” said Katherine Baicker, dean of the University of Chicago Harris School of Public Policy.

At least at first.

Entrepreneurs are expected to quickly translate the information into more user-friendly formats so it can be incorporated into new or existing services that estimate costs for patients. And starting Jan. 1, the rules require insurers to provide online tools that will help people get upfront cost estimates for about 500 so-called “shoppable” services, meaning medical care they can schedule ahead of time.
Hospitals Have Started Posting Their Prices Online. Here's What They Reveal

Once those things happen, “you’ll at least have the options in front of you,” said Chris Severn, CEO of Turquoise Health, an online company that has posted price information made available under the rules for hospitals, although many hospitals have yet to comply.

With the addition of the insurers’ data, sites like his will be able to drill down further into cost variation from one place to another or among insurers.

“If you’re going to get an X-ray, you will be able to see that you can do it for $250 at this hospital, $75 at the imaging center down the road, or your specialist can do it in office for $25,” he said.

Everyone will know everyone else’s business: for example, how much insurers Aetna and Humana pay the same surgery center for a knee replacement.

The requirements stem from the Affordable Care Act and a 2019 executive order by then-President Donald Trump.

“These plans are supposed to be acting on behalf of employers in negotiating good rates, and the little insight we have on that shows it has not happened,” said Elizabeth Mitchell, president and CEO of the Purchaser Business Group on Health, an affiliation of employers who offer job-based health benefits to workers. “I do believe the dynamics are going to change.”

Other observers are more circumspect.

“Maybe at best this will reduce the wide variance of prices out there,” said Zack Cooper, director of health policy at the Yale University Institution for Social and Policy Studies. “But it won’t be unleashing a consumer revolution.”

Still, the biggest value of the July data release may well be to shed light on how successful insurers have been at negotiating prices. It comes on the heels of research that has shown tremendous variation in what is paid for health care. A recent study by the Rand Corp., for example, shows that employers that offer job-based insurance plans paid, on average, 224% more than Medicare for the same services.

Tens of thousands of employers who buy insurance coverage for their workers will get this more-complete pricing picture — and may not like what they see.

“What we’re learning from the hospital data is that insurers are really bad at negotiating,” said Gerard Anderson, a professor in the department of health policy at the Johns Hopkins Bloomberg School of Public Health, citing research that found that negotiated rates for hospital care can be higher than what the facilities accept from patients who are not using insurance and are paying cash.

That could add to the frustration that Mitchell and others say employers have with the current health insurance system. More might try to contract with providers directly, only using insurance companies for claims processing.

Other employers may bring their insurers back to the bargaining table.

“For the first time, an employer will be able to go to an insurance company and say, ‘You have not negotiated a good-enough deal, and we know that because we can see the same provider has negotiated a better deal with another company,'” said James Gelfand, president of the ERISA Industry Committee, a trade group of self-insured employers.

If that happens, he added, “patients will be able to save money.”

That’s not necessarily a given, however.

Because this kind of public release of pricing data hasn’t been tried widely in health care before, how it will affect future spending remains uncertain. If insurers are pushed back to the bargaining table or providers see where they stand relative to their peers, prices could drop. However, some providers could raise their prices if they see they are charging less than their peers.

“Downward pressure may not be a given,” said Kelley Schultz, vice president of commercial policy for AHIP, the industry’s trade lobby.

Baicker, of the University of Chicago, said that even after the data is out, rates will continue to be heavily influenced by local conditions, such as the size of an insurer or employer — providers often give bigger discounts, for example, to the insurers or self-insured employers that can send them the most patients. The number of hospitals in a region also matters — if an area has only one, for instance, that usually means the facility can demand higher rates.

Bill Of The Month

Bill Of The Month

Another unknown: Will insurers meet the deadline and provide usable data?

Schultz, at AHIP, said the industry is well on the way, partly because the original deadline was extended by six months. She expects insurers to do better than the hospital industry. “We saw a lot of hospitals that just decided not to post files or make them difficult to find,” she said.

So far, more than 300 noncompliant hospitals have received warning letters from the government. But they could face $300-a-day fines for failing to comply, which is less than what insurers potentially face, although the federal government has recently upped the ante to up to $5,500 a day for the largest facilities.

Even after the pricing data is public, “I don’t think things will change overnight,” said Leibach. “Patients are still going to make care decisions based on their doctors and referrals, a lot of reasons other than price.”

KHN (Kaiser Health News) is a national newsroom that produces in-depth journalism about health issues. It is an editorially independent operating program of KFF (Kaiser Family Foundation).
The Strategic Relevance of Cybersecurity Skills – Lawfare

Posted by timmreardon on 06/29/2022
Posted in: Uncategorized. Leave a comment

By Tommaso De Zan Monday, June 27, 2022, 8:01 AM

Evidence suggests there is a global cybersecurity skills shortage affecting businesses and governments alike, which means that organizations are struggling to fill their cybersecurity vacancies. For example, the United Kingdom would need to attract approximately 17,500 new people every year into its cybersecurity sector to meet demand, and similar workforce difficulties have been reported in Australia, Italy, Japan, and the United States. Cybersecurity firm Fortinet depicted a stark picture of this gap in its 2022 report: 80 percent of polled organizations suffered one or more breaches due to a lack of cybersecurity skills and/or awareness, and 67 percent agreed that this shortage creates additional risks for their organizations. 

Further compounding this growing skills shortage has been increasing reliance on information systems, data, and networks to facilitate daily life. Modern information and communication technologies (ICT) are the main drivers of the “information society” of which cyberspace is a constitutive element and very much intertwined with the other physical, social, economic, and political layers. Hence, the absence of professionals who could defend the technological backbones of modern societies could have dire consequences for economic development and national security. For example, when cybersecurity skills are not available in the private sector, companies may incur heavier financial losses, experience disrupted operations, or compromise customers’ privacy and safety. And if this shortage were to happen on a large scale, firms will suffer because of cyber-related incidents in addition to market-related ones.

Meanwhile, the absence of cybersecurity experts protecting national critical infrastructures constitutes a national security threat, a loophole that may be exploited by malicious actors. The importance of securing systems that are generally unclassified or nonmilitary was highlighted even during the ongoing military confrontation in Ukraine by the former head of the U.K. National Cyber Security Centre, who pointed out that “[t]he strategic vulnerability to disruption and sabotage lies not so much in the military space but in the hospital booking system (Ireland), the logistics schedule (Maersk), the political party … and thousands of other mainstream, civilian, mostly privately owned networks.” Because societies are dependent on these information technology (IT) systems, which today are subject more than ever to “elevated cyber threats,” stakeholders should have a twofold approach: start treating the cyber skills shortage as a strategic policy challenge and devise a comprehensive strategy to deal with it.

The Cybersecurity Workforce as a Strategic Asset

Luckily, some national authorities have already framed the lack of cybersecurity experts as a relevant issue and have recognized the need for action. For instance, the U.K. Parliament was “struck” by the government’s apparent lack of urgency in addressing the shortage, which is of “vital importance to both national security and the economy.” The U.S. government expanded on this sentiment even further, stating that:

America’s cybersecurity workforce is a strategic asset that protects the American people, the homeland, and the American way of life. The National Cyber Strategy, the President’s 2018 Management Agenda, and Executive Order 13800 …, each emphasize that a superior cybersecurity workforce will promote American prosperity and preserve peace.

If the cybersecurity workforce is a strategic asset that can promote prosperity and preserve peace, then it follows that the lack of cybersecurity workers is a strategic issue with potential geopolitical implications. And if a country could significantly accrue its cybersecurity expertise by creating a proficient national cyber workforce, it would gain a comparative advantage: By nurturing the people with the right skills to fend off online attacks, that country could continue enjoying the benefits of digital advancements, as opposed to other countries that may struggle to defend themselves if they lack a security-savvy workforce. 

Some governments seem aware of what cybersecurity expert Greg Austin has suggested could become a “cyber workforce arms race.” The White House in its 2018 National Cyber Strategy stated that “[o]ur peer competitors are implementing workforce development programs that have the potential to harm long-term United States cybersecurity competitiveness.” This sentiment is also shared among other superpowers, most notably China, where President Xi Jinping reportedly argued that “talent is the first resource; competition in cyber space is ultimately talent competition.” 

Treating the skills shortage as a strategic issue does not imply that cybersecurity education and skills should be “securitized.” Instead, this realization should help stakeholders allocate the right resources when they plan to enhance the cyber resilience of their countries and organizations. Unfortunately, so far, the skills shortage has belied the high ranking of cybersecurity on corporate and national risk registers: Clearly, the identification of the problem has not translated into adequate investments in skills in the short or long term. For instance, it costs only 37,000 thousand euros to organize programs such as national cybersecurity skills competitions, whose goals are to help students increase their technical competencies and encourage them to choose cybersecurity as a career path, yet such competitions involve almost 18,000 talented youth in Europe every year. Not surprisingly, however, and despite the little investment needed to implement these programs, only 25 percent of national organizers think they have enough financial resources to achieve their objectives. 

A Comprehensive Cybersecurity Skills Strategy

A new inclusive strategy is imperative as multiple factors continue to worsen the shortage. On the one hand, there probably are not enough students enrolling in degrees that are conducive to a career in the cybersecurity sector. For example, in the U.K., almost 80,000 students are enrolled in computer science degrees, but only 6,000 (a mere 13 percent) study cybersecurity. Moreover, both hiring managers and academics complain that students’ cybersecurity skills are often too theoretical and that students lack practical experience. Conversely, employers are not making the situation any better when they publish job vacancies with unrealistic requirements, provide no entry-level opportunities, offer salaries below market value, or do not offer adequate cybersecurity training. For example, 89 percent of cybersecurity-related job postings in the U.S. require a bachelor’s degree, 75 percent require three to five years of professional experience, and 59 percent require professional certification. Thus, because this shortage has several roots, a holistic strategy needs a strong public-private partnership (PPP), where all relevant parties convene to bring their resources and expertise to solve this problem together.

From government reforms to changes in the way businesses recruit, much can be done. While private- and public-sector entities can take some measures immediately to ease their internal shortages, the reality is that this issue requires a national-level effort. Governments should ensure that more young people become interested in cybersecurity. In Israel, cybersecurity education is taught from an early age through the famous Magshimim program. Another option is to organize effective national cybersecurity competitions such as the Italian CyberChallenge.IT, which has noted an increased interest in general cybersecurity among its participants thanks to a mix of training, career seminars, and local and national capture-the-flag events. Governments can also design cybersecurity degrees that are academically and industry relevant, as they did in France and the U.S., where national cybersecurity authorities sat with faculty and professionals to establish new standards for cybersecurity curricula. Depending on the most in-demand jobs nationally, administrations could design market-level interventions to retrain junior IT staff and help them obtain an entry-level cybersecurity role, as the U.K. has already partially done with the Cyber Skills Immediate Impact Fund. Finally, employers must also have an active role in this process and increase junior placements, reconsider entry requirements, and upskill their current workforce. As a threat research expert put it eloquently, “Once it becomes clear that off-the-shelf experts aren’t realistic at scale, cultivating entry-level talent emerges as the only long-term solution—not just for a hiring organization but for the field as a whole.” 

Compared to five years ago when I started analyzing solutions to the skills shortage, we now know more about the problem and what tools may be used to remedy it. However, more could be achieved if stakeholders started treating the shortage as a strategic issue requiring appropriate resources. The lack of cybersecurity professionals might harm information society’s progress and beget geopolitical confrontation, and stakeholders need to converge on strong PPPs to find common solutions before it is too late.

Topics: 

  • Cybersecurity

Tags: 

  • Cybersecurity Training
Tommaso De Zan

Tommaso De Zan is a Senior Consultant within the Digital Policy Team at ICF (UK), where he conducts research studies and impact assessments for the European Commission and other public sector organisations. Previously, he was a CEI Expert for ENISA, an Associate Fellow with the EUISS and a Researcher at the International hAffairs Institute in Rome. He has a PhD in cybersecurity and education from the University of Oxford and a master’s degree in international security from the University of Bologna (Forlì).

  • tdezan21

Article link: https://www.lawfareblog.com/strategic-relevance-cybersecurity-skills?

Federal Government Gets Serious About Post-Quantum Encryption Protection – Nextgov

Posted by timmreardon on 06/29/2022
Posted in: Uncategorized. Leave a comment

By JOHN BREEDEN IIJUNE 29, 2022 08:00 AM ET

A Phase III PQE contractor talks about getting federal quantum protection deployed quickly.

There is a Chinese proverb that states that the best time to plant a tree was 20 years ago, while the second best time to plant one is right now. Given the quantum arms racegoing on between the United States and its potential rivals, the same can probably be said about post-quantum computing cybersecurity. And the government is now doing everything it can to get a program in place as quickly as possible.

There have already been mandates, proposals and studies. Earlier this year the White House mandated post-quantum cybersecurity—or PQC—via the National Security Memorandum “Promoting United States Leadership in Quantum Computing While Mitigating Risks to Vulnerable Cryptographic Systems.” And in Congress, the Quantum Computing Cybersecurity Preparedness Act would direct the National Institute of Standards and Technology and the Office of Management and Budget to develop mitigation measures for post-quantum cryptography. Meanwhile, the Department of Homeland Security worked with NIST to develop a roadmap toward better agency protection.

Planning for a safer future is good, but action is better. That is why the federal government awarded a rare Small Business Innovation Research (SBIR) Phase III contract to post-quantum cybersecurity company QuSecure. The sole-source contract, the first and only one issued for PQC, calls for the company to develop an end-to-end solution for post-quantum cybersecurity that can be deployed to federal agencies as quickly as possible.

Nextgov talked with QuSecure Co-Founder and COO Skip Sanzeri about the need for federal cybersecurity protections that can survive in a world where powerful quantum computers can shred today’s most advanced encryption.

Nextgov: Can you first explain what the awarding of a Phase III contract means for post-quantum protections?

Sanzeri: The Phase III award is a mechanism to allow a small technology company to move to the top of the heap and become a prime contractor, in order to supply vital technologies that can be used by the government without the typical bureaucracy or red tape. QuSecure sees this Phase III as an instance where the government recognizes the gravity of the coming situation where quantum computers will crack current encryption.

Nextgov: I am glad you brought up those dangers. One that has been talked about a lot here at NextGov is the fact that foreign governments are attempting to steal government data right now in hopes that they can store it and crack it later when better quantum computers are available. How important is it that we apply quantum resistant protections to government data right now?

Sanzeri: These “store now, decrypt later” attacks are the biggest reason to start upgrading networks and communications to post-quantum cybersecurity. Foreign nation states are stealing data every second of the day. That data is harvested and stored on computers waiting to be decrypted. And quantum computers will [one day] be able to crack that encryption.

For example, if a quantum computer with enough power to crack encryption is developed in five years, data stolen today would still be very valuable if it has 10, 20 or more years of shelf life. And national security secrets, bank account information, and electronic health records may have data security requirements of up to 75 years. Making matters worse, many experts estimate that changing our current encryption across an enterprise or government agency could take as long as 10 years. Adding this to the shelf life of data means that there are 10 more years of exposed data which attackers can weaponize or use against us. 

In many cases, we are already behind.

Nextgov: Putting aside the “steal and store” attacks for a moment, how long do you think we have before quantum computers can crack AES-256 or other strong encryption?

Sanzeri: At this point, quantum computers are not strong enough to crack our current encryption. Via an algorithm written by Peter Shor, it was mathematically proven that in order to crack current RSA 2048 encryption, you would need about 4,100 qubits. We are in the 100-qubit era now, but advancing rapidly. Many believe that we will have a powerful enough quantum computer in the next three to five years to crack encryption. Some say it will take longer, but nonetheless most data needs to be protected for 25 years or more. IBM, Google, PsiQuantum, Rigetti, and IonQ all have 1,000 qubit computing roadmaps by 2025.

Nextgov: How does your technology work to protect data from quantum-based and encryption-breaking attacks?

Sanzeri: To protect against quantum computers, we need to change encryption and use quantum keys to ensure that data and communications are secure from quantum attacks. QuSecure has an end-to-end post-quantum cybersecurity orchestration platform called QuProtect, which enables organizations for the first time to leverage quantum resilient technology to help prevent today’s cyberattacks, while future-proofing networks and preparing for post-quantum cyberthreats. 

It provides quantum-resilient cryptography, anytime, anywhere and on any device. QuProtect uses an end-to-end, quantum-security-as-a-service (QSaaS) architecture that addresses the digital ecosystem’s most vulnerable aspects, uniquely combining zero-trust, next-generation post-quantum-cryptography, quantum-strength keys, high availability, easy deployment, and active defense into a comprehensive and interoperable cybersecurity suite. The end-to-end approach is designed around the entire data lifecycle as data is stored, communicated and used.

Nextgov: So government will be able to protect its data both in transit and at rest from quantum attacks?

Sanzeri: Yes. Our QuProtect software-only security architecture overlays current infrastructure and protects data in motion, in use, and at rest—on any system, anywhere—from existing and emerging cyber-threats. We utilize NIST algorithms, quantum random number generation and proprietary software applied to communications and data, in order to protect it against quantum attacks. We also have backwards compatibility with our own proxy which translates between TLS layers and post-quantum encrypted communications. This combination of tools enables us to protect communications, data in transit, and data at rest.

Nextgov: Not to be a skeptic, but given that quantum computers rely on various different kinds of technologies—some are mechanical, some are electrical—and the fact that their capabilities are constantly expanding, how can you test your protections against that future threat and guarantee federal data protection?

Sanzeri: Very good question. At this point in time, no one has a quantum computer powerful enough to test encryption, and if we wait until we have that quantum computer, it will be too late. The best we can do at this point is to show how current classical cyberattacks can make data and communications vulnerable, then we can show the same classical attacks will not work against quantum resilient communications and data. 

Additionally, we must rely on organizations such as NIST, which spent over six years studying algorithms to find algorithm candidates that would withstand quantum computing attacks. Fundamentally, those algorithms have changed to be very complex, such as latticed-based infrastructures that mathematically can withstand quantum attacks. But that’s the best that anybody can do at this time.

Nextgov: Okay, so how long will it be before anti-quantum protection is widely available for deployment across the federal government?

Sanzeri: QuSecure will have this first production version of quantum resilience available for government purchase in less than six months. And we intend on adding many features to the initial system in future months that will make the system more robust and scalable. 

However, even with this rapid availability, it will still take years to deploy post-quantum cybersecurity across vast government networks—so that is the entire reason to start early. QuSecure’s solution is mostly software-based and can scale out to IoT and other end devices very quickly to create secure quantum communications. So once decisions are made, scalability and adoption will happen very quickly. 

We’re hoping that the federal government continues its rapid ascent towards a post-quantum world so that our nation’s most important data is protected. Our national security depends on it.

Article link: https://www.nextgov.com/cybersecurity/2022/06/federal-government-gets-serious-about-post-quantum-encryption-protection/368728/

John Breeden II is an award-winning journalist and reviewer with over 20 years of experience covering technology. He is the CEO of the Tech Writers Bureau, a group that creates technological thought leadership content for organizations of all sizes. Twitter: @LabGuys

An Opinion Series on Innovation: How the Intelligence Community Kills Ideas – The Cipher Brief

Posted by timmreardon on 06/29/2022
Posted in: Uncategorized. Leave a comment

Alternative Perspectives 

JUNE 28TH, 2022 BY MIKE MEARS | 0 COMMENTS

Mike Mears retired as the CIA’s Chief of Human Capital where he founded and headed the CIA Leadership Academy. He is a trainer and leadership consultant to government and private sector organizations. Prior to CIA, Mike was senior vice president at GE investments where he managed private equity funds, was a turnaround specialist, and a Six Sigma Black Belt. Before that, he launched eleven small business start-ups, and was president of a fast-food company. Mike served as commander of a nuclear missile site, a general’s aide, and was decorated for valor as a U.S. Army combat platoon leader in Vietnam.

View all articles by Mike Mears

OPINION — I recently saw a creative idea killed. Like a professional hit, the kill was silent and non-attributable. Managers essentially neutralized the employee—let’s call him Matt. I’m confident Matt will never make another suggestion, much less offer another game-changing idea, again.

Idea rejection in bureaucracies is often a clueless crime scene. There are no fingerprints because no one says, “No.” Managers and co-workers use passive-aggressive put-downs, grimaces, or admonishments like:

  • We tried it before.
  • Don’t rock the boat; be a team player.
  • It won’t work here; we’re different.
  • The boss will never buy it.
  • We have mission to do—no time for this.

In this case, like hyenas circling a fresh kill, several managers ganged up to ravage Matt’s idea—probably because it was a bit provocative and none of the managers had time to implement it. Here is the gauntlet they forced him to run:

  • Appear before a panel of those same managers to brief the idea. (None of the managers offered positive responses or encouragement during or after the brief.)
  • The panel reassigned Matt to a new location to work on the idea.
  • They required him to report to another manager who was not known for innovative receptiveness.
  • They advised Matt to stop talking to outsiders (IC colleagues) about the idea.
  • They required that he write a detailed execution plan.
  • Then, he had to work up a detailed budget.
  • He had to coordinate with legal.
  • Finally, Matt had to go on a roadshow to formally brief everyone who might be affected.

Of course, big ideas that impact multiple units need to be vetted, but in this case, the employee had to do it all himself, with no top cover or buy-in. In effect, the managers forced the idea through the organizational meat grinder to polish, pulverize, and contort it until it became a minor adjustment to the status quo—the perfect way to anonymously choke innovation.

It worked. The exhausted employee abandoned his treasured idea, and news of the gauntlet sent a clear signal to other employees not to come up with any pesky new ideas or potentially game-changing problem solutions.

What stops innovation?

A CIA Director once asked me, “Mike, why aren’t Agency employees being more creative?”

Then, he added, “I’ve told them I wanted more innovation.”

Like most organizational leaders, he tried to logically sell a cultural and motivational message to be more innovative. In most cases, that doesn’t stick because our minds don’t work that way.  Principles, values, and fears outweigh logic. For example, how often has your logic won a political argument?

If I could replay the conversation and answer him today, I would mention three powerful idea-killing forces that hinder innovation and will stop a CIA Director from unleashing change:

  • Survival instinct (Human nature)
  • Cultural rigidity (Organizational nature)
  • Leadership

Survival instinct

Human change resistance is a survival mechanism buried in all of our minds. It protects us from foolhardy or potentially dangerous ideas.

Rejecting ideas, especially terrible ones, got humans safely through the past 100,000 years or so. You’ll understand how potent change resistance is if you’ve ever tried to lose weight, quit smoking, or start an exercise program. Change resistance acts as a hidden brake inside our unconscious minds to slow us—even when we are trying to execute beneficial ideas.


The Cipher Brief hosts expert-level briefings on national security issues for Subscriber+Members that help provide context around today’s national security issues and what they mean for business.  Upgrade your status to Subscriber+ today.


Ideas are not created equal. Some are better than others. However, ideas—good or bad—are a gift to be treated with respect by management. A manager who gives a quick no, issues a put-down, or injects a little humiliation ensures employees won’t offer another idea because it is a part of the human survival instinct to avoid pain. If you’ve ever been rejected you understand the pain Matt felt.

Culture

At times, various reviews and blue-ribbon reports on intelligence community activities call for the need for “transformation” or “culture change.” The monographs leave IC managers in the dark about what culture is, much less how to change it.

Simple definition: Culture is the way we do things around here. Another way to think about it is that culture is shared habits, or the cumulative effect of individual’s behaviors.

Examples of culture include whether we call executives by their first name, how new employees are treated when onboarding, how freely employees and managers share ideas, dress codes, and even the amount of stress placed on internal correspondence that is error free. All of these are shared, habitual workplace behaviors.

Breaking individual habits, such as diet, smoking, and exercise, are problematic. Breaking shared habits in culture is trickier, and this is where I rephrase management guru Peter Drucker’s expression, “Culture eats strategy for breakfast,” to, “Culture eats executives for snacks.”

When I asked several hundred IC employees to describe their culture, they listed Mission first. That’s good. However, other descriptors crept into the top 10, including Caution and Control. Needless to say, if one aspires to be a “learning organization” or an “agile organization,” caution and control are severe inhibitors.

A prudent level of caution and control makes sense because of the nature of intel work. On the other hand, the overwhelming majority of the IC’s work does not involve life-and-death matters, and that’s where innovation becomes crucial. Yet, there is little personal upside to innovation for many employees in the IC, just lots of downside. As one person told me:

When someone proposes a new idea that fails, they are punished. If it succeeds, they aren’t rewarded; or everyone else takes credit.

Leadership

The leadership chain, including supervisors, managers, and executives, decides what ideas to accept or block. Let’s look at three innovation inhibitors:

  1. The absence of defined Senior Intelligence Service (SIS) roles
  2. Management turnover
  3. Leadership quality

The absence of defined SIS roles

We’ve all heard IC executives say, “I do mission.” But if the mission is choked by red tape, overwhelmed by technological change, and facing ever-changing adversaries, is “doing the mission” enough?

Some call an SIS promotion a “crown.” It is certainly a capstone to a career, but it should carry responsibility in addition to recognition of a successful career. For instance, are SIS officers shapers and keepers of the culture? Do they know how to change culture? Do they have a duty to reduce bureaucracy and inefficient processes? Do they have a role in removing barriers from employees? Should they act as “champions” to listen, coach, and provide top cover for innovation?

Too often, new SIS officers spend energy addressing problems in their unit, but do not act in concert with other executives in solving the broader organizational issues, no matter how pressing they may be. In effect, each SIS officer operates in their own bubble and not linked to the others.

I had discussions with change guru John Kotter about transforming the IC. He was aware of the turnover issue, and over the years, we had a running joke. When we bumped into one another, I’d ask, “What’s the first step to transform a large East Coast intelligence organization?” His reply was always, “You need a unified, committed leadership team at the top.”  High turnover insures that can’t happen.

As part of their promotion process, potential SIS officers should think through their responsibility to improve the overall organization and submit a detailed write-up of how they intend to do it.

Without a well-defined role, new SIS officers find themselves in the position of a teenager writing an English paper without a thesis statement.

Management turnover

Even if SIS roles were understood and reinforced, we face calamitous management turnover rates from the director level down to the supervisors. Each time a manager changes position, reporting lines are ruptured, vision and direction changes, and relationship bonds are fractured. None of the other elite organizations I consult with match the damaging 22-month turnover I found in one IC organization.

As a result of frequent job switching, enlightened managers don’t stay in place long enough to provide innovation cover—their tours are often curtailed early to solve a pressing problem elsewhere. Innovation lacks time to sprout, much less blossom, before the next manager arrives with a new agenda. Rapid turnover can be justified in specific overseas postings, but not in headquarters.

Short management tours make management accountability more difficult—bad leaders can move on before seniors can assess the damage they’ve done. In addition, rapid turnover hampers long-term thinking—executives focus on getting results over the next 18 months rather than launching the needed long-range programs and executing long-term improvement efforts.


Today’s constant barrage of information makes it easy for countries to wage disinformation campaigns and your emotions are the weapon of choice.  Learn how disinformation works and how we can fight it in this short video.  This is one link you can feel good about sharing.


Leadership quality

Years ago, I collected employee ratings on the 8,000 IC bosses they served over their careers. I was delighted at the percentage of both “Good” and “Outstanding” leaders, but the percentage of leaders they rated as “Poor” or “Awful” was disturbing because even a small percentage of bad leaders can have an outsized impact on organizational performance.

Bad leaders engender lower employee performance, create organizational distrust, and force some of the best employees to resign. However, they also generate cultural problems. in the short run, culture affects all the managers, but in the long run, the managers collectively affect culture. In this case, an autocratic boss develops his own microculture, one that is marked by higher psychological fear and far less innovation. Because culture is “sticky,” a bad boss can negatively affect an organization for up to five years after transferring out.

In organizations with two-year management turnover, a poor leader can ricochet around and serve in and “infect” three separate units within five years. The residual effect of lowered employee performance shows how a small percentage of bad leaders can have an outsized organizational impact.

In closing

Hundreds of long-gone, private-sector firms ignored the need for radical innovation, including Swiss watchmakers, Compaq, and Blockbuster. Hopefully, the IC can innovate fast enough that HUMINT and other vital IC functions are not added to the list.

Widely used change and transformation models often don’t deliver what they promise. They may pay lip service to the importance of employees’ and managers’ change resistance, the power of culture, and the difficulty of sustaining management commitment, yet these models too often underestimate the tenacity of these barriers.

What works when implementing change or spurring creativity? Take human nature into account when launching a transformation initiative. Despite the fact that humans are innately risk-averse, we see innovation all around. But how does this happen?

Step 1 is to define what makes people tick. We can do that by reviewing the current findings in psychology and neuroscience—for example, brain imaging is fine-tuned enough to give us an understanding of why humans are risk-averse and what managers can do to overcome it. I’ll dive into this more in part two of this series.

Step 2 is to apply leadership techniques that conform with the findings from Step 1—guiding employees around their innate change resistance. Best of all, this new way of leading and managing is less painful and easier to apply than current practices. I’ll focus more on that in part three of this series.

In Part II, I’ll visit a neuroscience lab and peer inside the brain to learn what went on in Matt’s head as his idea was killed. We’ll see how the tragedy goes deeper than just one fewer idea in the IC. The managers drowned his initiative—we’ll look into an fMRI to see why they may as well have fitted Matt’s motivation with tiny concrete shoes, wrapped it in chains, and tossed it over the side of a boat. And then we’ll ask whether the IC afford this.

Article link: An Opinion Series on Innovation: How the Intelligence Community Kills Ideas

This is an opinion piece, which means the views of the author are one perspective on an important issue. Have an opinion to contribute?  Drop a note to Editor@thecipherbrief.com

Read more expert-driven national security insights, perspective and analysis in The Cipher Briefbecause National Security is Everyone’s Business.

Quantum Sensors—Unlike Quantum Computers—Are Already Here – Nextgov

Posted by timmreardon on 06/28/2022
Posted in: Uncategorized. Leave a comment

By CHRIS JAY HOOFNAGLE AND SIMSON GARFINKEL JUNE 28, 2022 08:44 AM ET

And they’re improving at a rate that demands urgent attention.

Much ink has been spilled about quantum computers, particularly in overblown claims that quantum cryptanalysis will someday shred today’s encryption techniques. But their simpler cousins—quantum sensors—are here now and improving at a rate that demands urgent attention.

Quantum sensors use the smallest amounts of energy and matter to detect and measure tiny changes in time, gravity, temperature, pressure, rotation, acceleration, frequency, and magnetic and electric fields. They’ve been commercially available in various forms for more than a half-century; think of a magnetic resonance imaging, or MRI, machine, which tracks flips in the magnetic spin of individual hydrogen atoms to peer into a body. But recent progress in the field suggests that such sensors will soon bring a revolution in measurement and signals intelligence—possibly by making it far easier to detect submarines, spacecraft, and underground facilities.

Strategists must understand the new capabilities that quantum sensing will provide and start planning countermeasures today. Here are three examples that help explain why.

Measuring time

Ultra-precise timekeeping is the most important quantum-sensing achievement to date, for it adds precision to all other forms of sensing. For instance, it allows us to make repeated observations and combine them, an approach that is sometimes called “super resolution.” Think of the way today’s photographers take four or eight photos of the same scene and then combine the images using software. Better timing allows the same kind of thing with all kinds of measurements.

The atomic clocks of the 1970s that underlie the Global Positioning System and its attendant revolution—and miniaturized atomic clock are becoming commercially available. Microsemi Corporation, for example, sells a 35-gram “space chip scale atomic clock.” Laboratories are working on even better timing technology that promises to be just as transformative. In 2018, NIST announced a breakthrough: a clock based on a lattice of ytterbium atoms so sensitive that it wouldn’t drift more than a second in 10 billion years.

Location, location, location

Beyond making super-accurate GPS, quantum sensors can measure the shape and gravitational field of Earth to within a centimeter. Such sensing can be useful both for mapping out underground mineral resources and for precisely calculating the trajectories of ballistic missiles and other munitions.

Militaries have long sought ways to get extremely precise location data without using easily jammed GPS-type signals at all. Quantum positioning sensors track minute changes to rotation and acceleration, using Newton’s laws (adjusted for relativity) to accurately infer changes to location over time. Because they do not depend on signals from satellites or ground stations, they work anywhere—indoors, underground or underwater—and resist jamming. Defense contractors are starting to make portable QPS packages that could fit into weapons.

Related articles

Critical Update: To Bridge Quantum’s Valley of Death, Labs Need Funding and Workforce

Back to the Future: Protecting Against Quantum Computing

Seeing through walls and water

Advances in quantum radar and sonar research have rattled some policymakers because they may allow enemies to detect stealthy aircraft and warships and to distinguish legitimate radar targets from decoys.

Quantum radar would work by generating billions of “entangled” photon pairs, sending one photon from each pair into the search area while retaining the other in memory. “Signal” photons reflected back to the sensor are then compared to their “idler” mates, revealing information about airborne objects. Unlike conventional radar, such sensors promise to be largely immune to jamming and even detection by an adversary. In space, where photons are less likely to be scattered, quantum radar might be used to detect ballistic missiles, discover adversaries’ secret satellites, and spot and track tiny-but-still-dangerous space junk. There are engineering challenges, but theoreticians believe these are surmountable, and recent developmentssuggest approaches that could produce practical results.

Quantum sensing’s threat to the status quo is more dire underwater. The Chinese military has reportedly developed next-generation, sonar-like systems that can detect submarines and even underground objects. Other publications describe how Chinese scientists used precise measurement of time and location to fly a magnetometer over a field and detect buried iron balls based on their perturbations of the Earth’s magnetic field.

Such devices should eventually be able to detect the existence of underground tunnels or structures, and even the movement of military matériel or drugs through such tunnels. They might also allow the detection and tracking of America’s previously all-but-undetectable ballistic missile submarines and thereby destabilize nuclear deterrence.

Conclusion

The importance of quantum sensors has largely eluded policymakers, even though the technology has been improving for decades. Part of the reason is surely the hype surrounding quantum computers, whose challenges to practicability include their need to be shielded from interacting with the rest of the universe until its computation is complete. But quantum sensors, which put this extreme sensitivity to use, are here today and rapidly getting better.

The coming decades will be defined by greater reliance on measurement and sensing intelligence, brought about by electromagnetic and gravimetric quantum sensors that can see through barriers. Militaries may soon find it impossible to hide matériel and current secrecy strategies, such as using underground facilities, may be rendered ineffective.

Security policymakers must keep their eye on quantum sensing advances and their implications. And they must ask what it will mean when this technology leaves intelligence and military agencies and becomes in reach of law enforcement agencies, private companies, and wealthy individuals.

Article link: https://www.nextgov.com/ideas/2022/06/quantum-sensorsunlike-quantum-computersare-already-here/368681/

Chris Jay Hoofnagle is Professor of Law in Residence at the University of California, Berkeley, School of Law. Simson Garfinkel is a Senior Data Scientist at the U.S. Department of Homeland Security, a part-time teacher at The George Washington University, and a member of the Association for Computing Machinery’s US Technology and Policy Committee. They are co-authors of Law and Policy for the Quantum Age (Cambridge University Press, 2022). The views presented in this article do not reflect the policy of the Department of Homeland Security or the U.S. government.

How Agile Thinking Has Helped Federal Programs Excel – Forbes

Posted by timmreardon on 06/28/2022
Posted in: Uncategorized. Leave a comment

Jeff ShupackForbes Councils Member

Forbes Technology CouncilCOUNCIL POST| Membership (fee-based)

Jun 28, 2022,07:15am EDT

Jeff Shupack is the President of Advisory Practice at Project & Team.

You don’t usually see innovation happening first in government; that’s typically the bailiwick of private industry. But in the case of the General Services Administration, great strides have been made in using agile methodologies to modernize applications and integrate flexible architecture—progress that sets a high bar for any corporate entity.

Agile software development was also the mantra for Nicolas Chaillan, the former Chief Software Officer of the Air Force and Space Force. Innovation and agile development in software is a better use of taxpayer dollars than a typical waterfall-type acquisition and development process, Chaillan has explained.

Despite some stumbles or stubbornness along the way, the federal government is starting to take on a leadership role in the use of agile business practices to improve effectiveness while accomplishing business goals.

Agile methodologies enable organizations to maintain higher ground and accelerate their competitive positioning. Indeed, there are several government initiatives that pit agencies competitively against each other. One of those is the Federal IT Acquisition Reform Act (FITARA), which we’ll look at shortly. The takeaway, however, is that agencies that have chosen to adopt agile practices routinely do better than their peers.

Let’s take a nuts and bolts look at the GSA project we addressed at the outset. In a project very near completion (anticipated to wrap in the Fiscal Year 2022), GSA used agile methodologies in a program that has seen no cost overruns and is projected to meet its approved budget.

FITARA And TMF

GSA is absolutely leading the way as the government sees an increasing convergence of two federal initiatives—FITARA and the Technology Modernization Fund (TMF). By proactively taking advantage of one, the agency finds itself well-positioned to offer success stories for both.

For context, the TMF is an innovative funding vehicle that gives agencies additional ways to deliver services to the American public more quickly while improving the security of sensitive systems and data and making more efficient use of taxpayer dollars.

TMF was born out of the Modernizing Government Technology Act of 2017 to ensure project success for federal tech programs. So far, TMF has amassed $175 million through the annual budget process and $1 billion through the American Rescue Plan to fund modernization projects.

FITARA is a bit longer in the tooth, having been passed by Congress in December 2014 in what was the first major overhaul of Federal information technology (IT) in nearly two decades. Each year in April, agencies score themselves against a list of requirements, with the Office of Management and Budget scorecarding the results a month or so later.

Lately, agencies have found themselves treading water in FITARA compliance. Last year, 18 of 24 agencies saw no improvement in their scores, with two having slipped below their previous rankings. Only GSA received an A-plus score amidst a sea of Cs and Bs.

The less-than-stellar agency performance in FITARA has led lawmakers and CIOs alike to posit that perhaps the program would benefit from somewhat of an overhaul, concentrating more on cybersecurity and getting assistance from TMF. (TMF has become a way for agencies to improve their cybersecurity and achieve IT modernization goals as well.)

It remains to be seen whether TMF will help all agencies over the FITARA hump, but as we’ve said, GSA, in particular, offers a glowing example of success in the use of agile practices for IT modernization and reform. Let’s take a closer look at how GSA has emerged as the poster child for responsible and effective digital transformation.

GSA’s Agile Application Modernization

GSA’s account of how it succeeded in modernizing its applications is brief and well worth reading and can be found in TMF’s publicly available overview. 

In essence, in 2018, the organization needed to modernize 88 IT applications to integrate them with other systems. The agency received an investment from TMF of nearly $10 million, allowing GSA to take on all its modernization needs at once, from software to hardware.

There are two takeaways to understanding how GSA succeeded in its modernization mission.

1. The agency adopted a cross-functional solutions team to implement best-in-class agile methodologies.

2. They created a set of “playbooks” to standardize how databases will be transformed and how data is to be migrated from now on. (As a bonus, GSA has made these playbooks available to other agencies in similar positions.)

The result of the effort is a comprehensive initiative that’s on track to come in on time and within budget.

This, of course, is the goal of every agile project in any industry. The proper application of agile practices typically allows organizations to improve performance and create an easier pathway to scaling their operations.

In fact, GSA’s success story is at the heart of what digital transformation can and should be. Agile methodologies and best practices create repeatable processes that can continually adjust to the demands of the ever-shifting digital landscape. It’s also an example of how innovative thinking can make use of existing initiatives to improve performance across more than one set of enterprise requirements.

GSA succeeded because agency personnel understood that they were not just overhauling IT systems. They were actually upending years of inflexible attitudes toward business processes and replacing them with a culture of “continuous learning.”

Cross-functional solutions teams, like those in GSA’s account, are essential to an environment of continuous learning. The individuals on the teams are free to create new and innovative ways to address problems without the stress and fatigue that can often come with an organizational mandate to “get creative.”

Of course, there’s much more to creative learning and digital transformation, and we’ll unpack aspects of the process throughout these commentaries. The question now becomes, what lessons can your organization learn from the GSA’s experience? How can you apply agile processes to your own business goals to continually learn how to navigate the waters of digital transformation?

Article link: https://www.forbes.com/sites/forbestechcouncil/2022/06/28/how-agile-thinking-has-helped-federal-programs-excel/amp/


Forbes Technology Council is an invitation-only community for world-class CIOs, CTOs and technology executives. Do I qualify?

Improving Defense Acquisition – RAND

Posted by timmreardon on 06/26/2022
Posted in: Uncategorized. Leave a comment

Insights from Three Decades of RAND Research

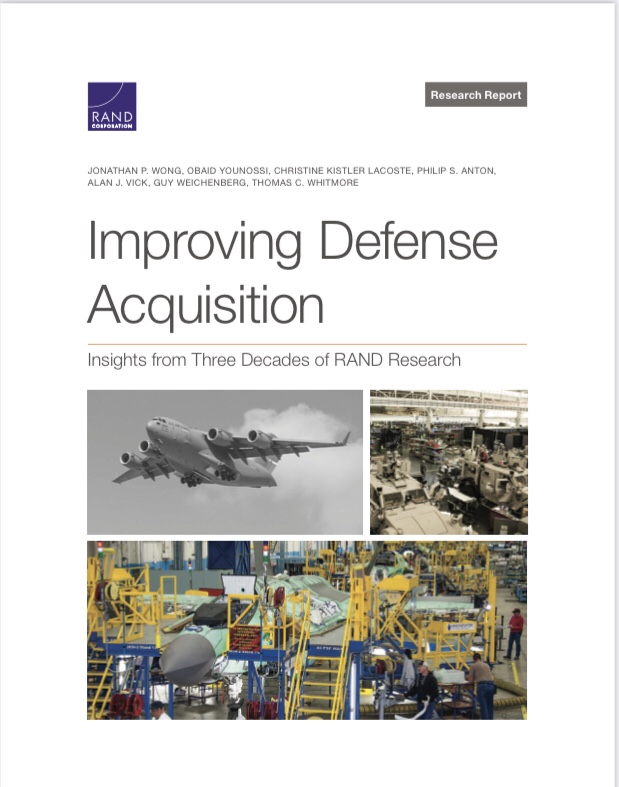
by Jonathan P. Wong, Obaid Younossi, Christine Kistler LaCoste, Philip S. Anton, Alan J. Vick, Guy Weichenberg, Thomas C. Whitmore

  • Related Topics: 
  • Military Acquisition and Procurement, 
  • Military Budgets and Defense Spending, 
  • Military Technology, 
  • United States Department of Defense
  • Citation
  • Synopsis(print-friendly)
  • Embed
  • View related products
  • Share on Facebook
  • Share on Twitter
  • Share on LinkedIn

Download

DOWNLOAD EBOOK FOR FREE

Full Document

PDF file1.3 MB

Technical Details »

Research Summary

PDF file0.1 MB

Technical Details »

Purchase

Research Questions

  1. What are the overarching trends that affect the DoD acquisition system?
  2. What challenges does DoD’s acquisition of weapon systems face?
  3. What insights can RAND research offer on how to confront these challenges?

Improving the U.S. Department of Defense (DoD) acquisition system — the management and development processes by which the department acquires, develops, and sustains weapon systems, automated information systems, and services — has been an issue of sustained interest to policymakers since the beginning of the military establishment. Numerous actions have been initiated and implemented over decades to rein in the increasing life-cycle costs and to ensure a timely delivery of these systems to meet U.S. security needs. In this report, researchers describe overarching trends that affect the defense acquisition system, outline challenges in DoD’s defense acquisition process, and suggest improvements that might help address those challenges. The study is informed by open-source documents and insights from publicly available RAND Corporation research on defense acquisition, especially reports published since 1986, when a similar review of RAND research was published.

Key Findings

Four overarching trends affect the defense acquisition system

  • Geopolitical changes have widened the threat landscape; in addition to a resurgent Russia, growing Chinese economic and military power poses new threats to U.S. interests, while Islamic extremism remains a potent force.
  • Globalization has altered the economic and technological landscape, creating new opportunities, as well as challenges, for DoD.
  • The United States has changing national priorities: Defense issues remain important, but domestic policy issues compel policymakers to prioritize attention and resources.
  • Advancing commercial technologies are creating new challenges and opportunities for an acquisition system that was not designed to import and adapt technologies developed outside the traditional defense industrial base.

The trends are linked to the following eight challenges for DoD’s acquisition system

  • Responding to evolving missions.
  • Leveraging a changing defense industrial base.
  • Accommodating interoperability.
  • Building in cybersecurity.
  • Planning for technology refresh and insertion.
  • Rebuilding the acquisition workforce.
  • Managing the acquisition cost of systems.
  • Aligning incentives, organizations, and processes to acquisition goals.

Recommendations

  • To achieve desirable acquisition outcomes, acquisition strategies, organizational roles and responsibilities, and reporting structures must be tailored to the unique characteristics of each program. There is no one-size-fits-all approach that works with every program, and attempts to force programs into a single paradigm lead to problems and inefficiencies.
  • It is important to broaden and plan for the defense industrial base. An inclusive industrial base must be better engaged to fully exploit its innovation potential and must be focused on sustaining key parts of the defense industrial base.
  • The acquisition workforce must be properly sized, trained, and incentivized to make the smart decisions that flexible acquisition approaches and partnering productively with industry entail.
  • DoD needs to continue improving its ability to track and analyze important attributes of the acquisition system. Broadly improving acquisition data collection and analysis would help DoD evaluate the effects of major changes in acquisition policy and better plan for the long term.

Article link: https://www.rand.org/pubs/research_reports/RRA1670-1.html

Russia-linked actors may be behind an explosion at a liquefied natural gas plant in Texas

Posted by timmreardon on 06/26/2022
Posted in: Uncategorized. Leave a comment

June 26, 2022 By Pierluigi Paganini

A Russian hacking group may be responsible for a cyber attack against a liquefied natural gas plant in Texas that led to its explosion on June 8.

The explosion took place at the Freeport Liquefied Natural Gas (Freeport LNG) liquefaction plant and export terminal on Texas’ Quintana Island. The June 8 incident will have a lasting impact on Freeport LNG’s operations.

Preliminary investigations suggested that the incident resulted from the overpressure and rupture of a segment of an LNG transfer line, leading to the rapid flashing of LNG and the release and ignition of the natural gas vapor cloud.

At this time it is not clear why the safety mechanisms in place did not prevent the explosion. Experts speculate a cyber attack may have turned off the industrial safety controls at the natural gas facility.

ICS malware like TRITON, which experts associated with Russia-linked APT group XENOTIME, has offensive capabilities to shut down industrial safety controls and cause extensive damages to industrial facilities.

“On March 24 the U.S. Department of Justice brought charges against four Russian nationals suspected of using TRITON malware in cyber attacks on behalf of the Russian government between 2012 and 2018. That same day, the FBI issued an advisory warning that TRITON malware tools still remain a major threat to industrial systems around the world.” reported the American Military News website.

The Washington Times national security writer Tom Rogan confirmed that the explosion at the Freeport LNG facility could be consistent with a hacking campaign conducted by APT groups like XENOTIME.

Rogan added that the company does have in place the Operation Technology/Industrial Control Systems network detection systems.

At this time, Freeport LNG denied the theory that sees a cyber attack as the root cause of the incident. 

“Unless Freeport LNG has OT/ICS network detection systems deployed appropriately and has completed a forensics investigation, a cyberattack cannot be ruled out,” Rogan wrote.

“Two more sources who spoke with Rogan said that around the time of Russia launched its invasion of Ukraine, a cyber unit of Russia’s GRU military intelligence service conducted targeting-reconnaissance operations against Freeport LNG.” continues the American Military News

Article link: https://securityaffairs.co/wordpress/132608/security/liquefied-natural-gas-plant-texas-explosion.html?

A national patient ID is essential for patient safety – STAT

Posted by timmreardon on 06/26/2022
Posted in: Uncategorized. Leave a comment

By Wylecia Wiggs Harris and Tom CoxJune 22, 2022

Misidentifying patients can have tragic consequences.

Numerous catastrophic cases and near misses have been collected by Patient ID Now, a coalition of health care organizations we are affiliated with that is dedicated to advancing a nationwide patient identification and matching strategy.

In one example from the Patient ID Now website, a woman had a routine mammogram, but never received the results. Assuming that no news was good news, she mentioned the mammogram to her doctor months later during her annual physical. That conversation led to the discovery that her results had been misfiled in the chart of a deceased patient who shared her name. The mammogram showed cancer which, during the one-year delay, had become terminal.

This story is not an outlier.

There’s far more than anecdotal evidence that patient misidentification is a serious and widespread problem in U.S. health care. A Government Accountability Office report found that 45% of large hospitals reported difficulty accurately identifying patients through electronic health information. A report from Pew Charitable Trusts notes that accurately matching patients to their medical records can be as low as 80% within a single care setting, and as low as 50% among organizations that shared electronic health information.

This epidemic of misidentification is rooted in the lack of a national patient identification strategy.

Today, a hospital’s or clinic’s ability to accurately identify the patients it serves often hinges on a precarious patchwork of Social Security numbers, phone numbers, driver’s licenses, and home addresses that strains under the weight of an increasingly mobile population with health information scattered across multiple care settings.

Covid-19 has underscored that patient identification is an increasing issue for public health. During the pandemic, there were reports of patients not receiving Covid-19 test results, or receiving the wrong results, because of misidentification. And many received vaccinations outside of their usual doctor’s office at pop-up and pharmacy locations, adding complexities about updating medical records.

Progress toward a national patient identification strategy has been hindered for more than two decades because of a rider inserted into the federal budgetthat prohibits federal funds from being used to develop a unique health identifier standard.

The history of this annual rider dates back to 1996, when Congress passed, and President Bill Clinton signed, the Health Insurance Portability and Accountability Act. One of HIPAA’s many goals was to aid the transition from paper to electronic records, and it called for developing a unique identifier. Rep. Ron Paul (R-Tex.), Congress’s leading libertarian at the time, saw such an identifier as government intrusion into private health care and inserted language into the federal budget that barred the government from spending any money to develop a unique identifier. That ban has been in place ever since.

Bipartisan support for repealing this ban has been growing in Congress, with the House of Representatives removing the language from its Labor, Health and Human Services, Education, and Related Agencies appropriations bill for three years, and the Senate removing the language for the first time from its draft Labor-HHS bill released for fiscal year 2022.

Final negotiations, however, resulted in the ban being reinserted to the 2022 budget, continuing the provision that stifles progress to improve patient safety and privacy. President Biden signed the budget into law earlier this year. Just last month, the Patient ID Now Coalition continued the push to remove the rider from the 2023 fiscal year appropriations bill in a letter to House appropriators and Senate appropriators that was signed by 119 industry stakeholders.

The health care community has a responsibility to do everything possible to protect the people and communities it serves. To fulfill this mission, it needs to move forward with serious discussions regarding the shape, scale, and cost of a national patient identification strategy, one that ensures the safety of patients and the privacy and security of their personal and medical information.

This national strategy could include a number of solutions that have been proposed, including, but not limited to, a unique patient identifier; biometrics; standardization of demographic elements such as home address or telephone number; or various algorithms, and would require a number of considerations to be taken into account.

As the Patient ID Now coalition proposed in its Framework for a National Strategy on Patient Identity, a national strategy should increase patient match rates, protect patient privacy and security, support interoperability, and improve standardization of health data, data quality, and health equity. To get there, the federal government would need to bring in stakeholders from across health care and public health to address these issues.

This isn’t just a bureaucratic issue. In addition to enhancing safety and reducing health care costs, a national patient identification strategy would empower patients. Recent federal regulations, such as the provisions prohibiting information blocking in the 21st Century Cures Act, give consumers greater ability to store, aggregate, use, and share their health information using apps of their choice. Improving patient identification would make it easier for complete and accurate health records to follow individuals wherever they go and allow them to better control who can access and share their personal health information.

Congress must finally address this outdated ban to make true progress toward solving one of health care’s most enduring problems. Health care has spent the better part of 20 years investing in an interoperable, value-based, patient-centric ecosystem. A national strategy for patient identification is essential for connecting the fragmented health care system, while making it safer and more efficient for patients and health providers.

Article link: https://www.statnews.com/2022/06/22/national-patient-id-essential-patient-safety/?

Wylecia Wiggs Harris is CEO of the American Health Information Management Association (AHIMA), a global nonprofit association of health information professionals. Tom Cox is president of Experian Health, a provider of health care software solutions. AHIMA and Experian Health are members of Patient ID Now.

Empathetic customer experience helps build trust in government – Federal News Network

Posted by timmreardon on 06/26/2022
Posted in: Uncategorized. Leave a comment

Since it surfaced in the 1990s, the federal service-to-the-citizen movement has continuously evolved. New technologies keep making new services possible and, as in the private sector, moving the expectations of customers and constituents.

Customer experience has emerged as the latest iteration. Embodied in the current President’s Management Agenda, customer experience (CX) embodies all of the ways in which a constituent might interact with a federal agency. An earlier concentration on web transactions has expanded into omni-channel thinking. Constituents want reach agencies in person, on the telephone, by email or live chat, or digitally. This means systems and processes must share backend access to data connected to an individual, for example a taxpayer. Or to a transaction, the tax return itself.

“It is this that seamless experience of interacting through tax administration, that is really taxpayer experience for us,” said Kenneth Corbin, the chief taxpayer experience officer at the IRS. He spoke as part of a Federal News Network panel entitled, Better Customer Experience Builds Trust in Government. Corbin added, “That seamless experience is being able to choose how you interact with the Internal Revenue Service, whether you interact in person, whether you call us on toll free and talk with one of our customer service representatives, or of course, interact with us digitally online through irs.gov.”

Maintaining the trust of the nine million veterans it serves is foundational to CX work at the Veterans Affairs Department. Barbara Morton, the VA’s deputy chief veterans experience officer, detailed “three core elements that we have tried to focus on and hardwire into our business operations.” They start with a customer journey approach to veterans’ interactions, and add measurements of effectiveness of those iterations. “And thirdly,” Morton said, “and most importantly, perhaps, they must be emotionally resonant for the veteran. There must be empathy in everything we do, in every interaction we have.”

It might sound surprising coming from the Office of Management and Budget, but officials there consider empathy an important CX element across the government.

“I always say we have to lead with empathy,” said Andy Lewandowski, the digital experience advisor to the federal chief information officer. “The basic purpose of customer experience delivery, and of human centered design, is to put ourselves in our customers’ shoes.”

Steven Boberski, the senior business development executive for the puvlic sector at Genesys, said that cybersecurity is an important CX consideration, given the sensitive and personally identifiable data that agencies deal with. He recommended use of FedRAMP-approved vendors in the chain of technology for public-facing services.

Boberski said that while mapping the customer’s journey is critical, it’s also critical to retain and consolidate data from each step of a given customer’s encounter.

“To provide empathy from the federal perspective,” Boberski said, means “knowing exactly where that citizen has been in their journey with the agency.” For example, the agency should be able to say, “We can see from the data that you’ve called in multiple times. You’ve tried an email. We have a record of where you’ve been, perhaps we can see that you’ve tried to file your taxes, or you’ve tried to renew something or create a new claim.”

“Knowing where they’ve been in a customer journey is very important,” Boberski added.

Given the challenges of great CX, agencies must take care to integrate the data sources and applications they have and bend them towards CX.

“If we were to design a federal service or agency from scratch, the technologists would probably start by implementing a single customer relationship management system,” Lewandoski said. “That is not the reality in most of our federal agencies and programs today.”

He added, “So the challenge that agencies have from a technology standpoint, is to make sure that those systems are talking to each other.” And that information is stored securely yet available to shared programs.

“And,” Lewandowski said, “that those systems are fundamentally mapping themselves in the backstage, as I like to say, to the front stage experience that customers have when they interact with government.”

Learning objectives:

  • Defining Customer Experience from an Agency Perspective
  • Relevant Tools for Enhancing Customer Experience
  • Customer Experience with Secure Interactions

Article link: https://federalnewsnetwork.com/cme-event/federal-insights/better-customer-experience-builds-trust-in-government/?readmore=1

Posts navigation

← Older Entries
Newer Entries →
  • Search site

  • Follow healthcarereimagined on WordPress.com
  • Recent Posts

    • By Barring Profits on Basic Coverage, Switzerland Keeps Insurers from Denying Care – Commonwealth Fund 10/19/2026
    • Patients’ Perspectives on AI in Primary Care – Commonwealth Fund 09/11/2026
    • Bitcoin Mining Energy Footprint 08/06/2026
    • Closing the AI Hype Gap 08/05/2026
    • Why Artificial Intelligence is Neither Artificial, Nor Intelligent 07/31/2026
    • Agentic AI, explained 07/05/2026
    • Heeding the pope’s call to ensure AI protects human dignity – MIT Sloan Management 06/01/2026
    • Association between Wealth and Mortality in the United States and Europe – New England Journal of Medicine 05/30/2026
    • U.S. Health Care from a Global Perspective, 2026 – The Commonwealth Fund 05/30/2026
    • Anthropic co-founder Chris Olah’s remarks on Pope Leo XIV’s encyclical “Magnifica humanitas” 05/28/2026
  • Categories

    • Accountable Care Organizations
    • ACOs
    • AHRQ
    • American Board of Internal Medicine
    • Big Data
    • Blue Button
    • Board Certification
    • Cancer Treatment
    • Data Science
    • Digital Services Playbook
    • DoD
    • EHR Interoperability
    • EHR Usability
    • Emergency Medicine
    • FDA
    • FDASIA
    • GAO Reports
    • Genetic Data
    • Genetic Research
    • Genomic Data
    • Global Standards
    • Health Care Costs
    • Health Care Economics
    • Health IT adoption
    • Health Outcomes
    • Healthcare Delivery
    • Healthcare Informatics
    • Healthcare Outcomes
    • Healthcare Security
    • Helathcare Delivery
    • HHS
    • HIPAA
    • ICD-10
    • Innovation
    • Integrated Electronic Health Records
    • IT Acquisition
    • JASONS
    • Lab Report Access
    • Military Health System Reform
    • Mobile Health
    • Mobile Healthcare
    • National Health IT System
    • NSF
    • ONC Reports to Congress
    • Oncology
    • Open Data
    • Patient Centered Medical Home
    • Patient Portals
    • PCMH
    • Precision Medicine
    • Primary Care
    • Public Health
    • Quadruple Aim
    • Quality Measures
    • Rehab Medicine
    • TechFAR Handbook
    • Triple Aim
    • U.S. Air Force Medicine
    • U.S. Army
    • U.S. Army Medicine
    • U.S. Navy Medicine
    • U.S. Surgeon General
    • Uncategorized
    • Value-based Care
    • Veterans Affairs
    • Warrior Transistion Units
    • XPRIZE
  • Archives

    • October 2026 (1)
    • September 2026 (1)
    • August 2026 (2)
    • July 2026 (2)
    • June 2026 (1)
    • May 2026 (12)
    • April 2026 (4)
    • March 2026 (9)
    • February 2026 (6)
    • January 2026 (8)
    • December 2025 (11)
    • November 2025 (9)
    • October 2025 (10)
    • September 2025 (4)
    • August 2025 (7)
    • July 2025 (2)
    • June 2025 (9)
    • May 2025 (4)
    • April 2025 (11)
    • March 2025 (11)
    • February 2025 (10)
    • January 2025 (12)
    • December 2024 (12)
    • November 2024 (7)
    • October 2024 (5)
    • September 2024 (9)
    • August 2024 (10)
    • July 2024 (13)
    • June 2024 (18)
    • May 2024 (10)
    • April 2024 (19)
    • March 2024 (35)
    • February 2024 (23)
    • January 2024 (16)
    • December 2023 (22)
    • November 2023 (38)
    • October 2023 (24)
    • September 2023 (24)
    • August 2023 (34)
    • July 2023 (33)
    • June 2023 (30)
    • May 2023 (35)
    • April 2023 (30)
    • March 2023 (30)
    • February 2023 (15)
    • January 2023 (17)
    • December 2022 (10)
    • November 2022 (7)
    • October 2022 (22)
    • September 2022 (16)
    • August 2022 (33)
    • July 2022 (28)
    • June 2022 (42)
    • May 2022 (53)
    • April 2022 (35)
    • March 2022 (37)
    • February 2022 (21)
    • January 2022 (28)
    • December 2021 (23)
    • November 2021 (12)
    • October 2021 (10)
    • September 2021 (4)
    • August 2021 (4)
    • July 2021 (4)
    • May 2021 (3)
    • April 2021 (1)
    • March 2021 (2)
    • February 2021 (1)
    • January 2021 (4)
    • December 2020 (7)
    • November 2020 (2)
    • October 2020 (4)
    • September 2020 (7)
    • August 2020 (11)
    • July 2020 (3)
    • June 2020 (5)
    • April 2020 (3)
    • March 2020 (1)
    • February 2020 (1)
    • January 2020 (2)
    • December 2019 (2)
    • November 2019 (1)
    • September 2019 (4)
    • August 2019 (3)
    • July 2019 (5)
    • June 2019 (10)
    • May 2019 (8)
    • April 2019 (6)
    • March 2019 (7)
    • February 2019 (17)
    • January 2019 (14)
    • December 2018 (10)
    • November 2018 (20)
    • October 2018 (14)
    • September 2018 (27)
    • August 2018 (19)
    • July 2018 (16)
    • June 2018 (18)
    • May 2018 (28)
    • April 2018 (3)
    • March 2018 (11)
    • February 2018 (5)
    • January 2018 (10)
    • December 2017 (20)
    • November 2017 (30)
    • October 2017 (33)
    • September 2017 (11)
    • August 2017 (13)
    • July 2017 (9)
    • June 2017 (8)
    • May 2017 (9)
    • April 2017 (4)
    • March 2017 (12)
    • December 2016 (3)
    • September 2016 (4)
    • August 2016 (1)
    • July 2016 (7)
    • June 2016 (7)
    • April 2016 (4)
    • March 2016 (7)
    • February 2016 (1)
    • January 2016 (3)
    • November 2015 (3)
    • October 2015 (2)
    • September 2015 (9)
    • August 2015 (6)
    • June 2015 (5)
    • May 2015 (6)
    • April 2015 (3)
    • March 2015 (16)
    • February 2015 (10)
    • January 2015 (16)
    • December 2014 (9)
    • November 2014 (7)
    • October 2014 (21)
    • September 2014 (8)
    • August 2014 (9)
    • July 2014 (7)
    • June 2014 (5)
    • May 2014 (8)
    • April 2014 (19)
    • March 2014 (8)
    • February 2014 (9)
    • January 2014 (31)
    • December 2013 (23)
    • November 2013 (48)
    • October 2013 (25)
  • Tags

    Business Defense Department Department of Veterans Affairs EHealth EHR Electronic health record Food and Drug Administration Health Health informatics Health Information Exchange Health information technology Health system HIE Hospital IBM Mayo Clinic Medicare Medicine Military Health System Patient Patient portal Patient Protection and Affordable Care Act United States United States Department of Defense United States Department of Veterans Affairs
  • Upcoming Events

Blog at WordPress.com.
healthcarereimagined
Blog at WordPress.com.
  • Subscribe Subscribed
    healthcarereimagined
    Join 149 other subscribers

    Have a WordPress.com account? Log in now.

  • healthcarereimagined
    View site in Reader
    Manage subscriptionsSign upLog in
    Report this content
    Collapse this bar
Loading Comments...