The U.S. NSA, CISA and ODNI created the Securing the Software Supply Chain guide to focus on the software development lifecycle.
By Chris Hughes
CSO
SEP 15, 2022 2:00 AM PT
Software supply chain attacks are on the rise, as cited in the Cloud Native Computing Foundation’s (CNCF’s) Catalog of Supply Chain Compromises. Industry leaders such as the Google, Linux Foundation, OpenSSF, and public sector organizations such as NIST have provide guidance on the topic over the past year or so.
The U.S. National Security Agency (NSA) alongside the Cybersecurity and Infrastructure Security Agency (CISA), and the Office of the Director of National Intelligence (ODNI) now join that list with their publication Securing the Software Supply Chain: Recommended Practices Guide for Developers. The announcement of the publication emphasizes the role developers play in creating secure software and states the guide strives to help developers adopt government and industry recommendations on doing so. Subsequent releases from Enduring Security Framework (ESF) will focus on the supplier and the software consumer, given the unique role each plays in the broader software supply chain and its resilience.
At a high-level the document is organized into three parts:
- Part 1: security guidance for software developers
- Part 2: software supplier considerations
- Part 3: software customer recommendations
The role of developers, software suppliers and customers
The guidance notes the unique role developers, suppliers and customers play in the broader software supply chain ecosystem.

Software providers and their development teams may end up in the dichotomy of speed to market, versus secure and resilient software or software-enabled products.
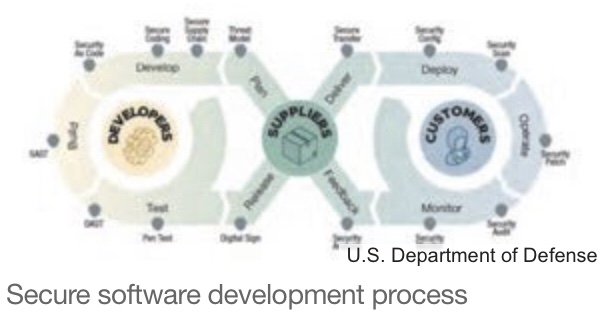
As noted in the image above, each of the three roles has respective security activities it can and should be doing. These activities span the gamut from initial secure software development, composition and architecture all the way through security acceptance testing and integrity validation on the customers’ end.
Secure software begins with a secure software development lifecycle (SDLC) and the guidance cites many options teams can use, such as the U.S. National Institute of Standards and Technology’s (NIST’s) Secure Software Development Framework (SSDF), Carnegie Mellon University’s Secure Software Development Lifecycle Processes, and others such as the recently announced OpenSSF Secure Software Development Fundamentals courses.
How to develop secure software
The guidance stresses not just using secure software development processes but producing tangible artifacts and attestations that are used for validation, both by the software producer and consumer to have assurances related to the security and resiliency of the software. These processes and activities include best practices such as threat modeling, SAST, DAST and pen testing but also using secure release activities such as digitally signing, a notable example being the increased adoption of Sigstore, which is a standard for signing, verifying and protecting software. The adoption and use of Sigstore is also cited in the OpenSSF’s Open Source Security Mobilization Plan as a method to deliver enhanced trust in the software supply chain.
Threat modeling gets a significant mention, recognizing that during product development and delivery teams should be examining the potential threat scenarios that can occur and what controls could be put in place to mitigate them. Teams should also have established security test plans and associated release readiness criteria to ensure unacceptable vulnerabilities are not making it to production environments or getting to customers.
Mature product teams have established support and vulnerability handling policies as well. This includes having a system where product vulnerabilities can be submitted and an associated incident response team that is in a position to respond and get engaged should an incident occur. Given the impact developers can have on producing secure or insecure products, formalized assessment and training must occur. Determine what training is required and who is required to take it at a specified frequency. The OpenSSF’s Open Source Software Security Mobilization Plan lists upskilling developers on secure software development as a key objective that is recognized as an industry-wide necessity. Training topics include secure software development, code reviews, verification testing and using vulnerability assessment tools during development to drive down vulnerabilities that make it into their end products.
The activities and practices discussed above, such as secure development training, threat modeling, security test plan and developed security policies and procedures, are mapped to activities in the previously mentioned NIST SSDF, which will be a requirement soon for software vendors to self-attest to when selling software products to the U.S. federal government.
Secure code development has many aspects, including selecting programming languages that could mitigate vulnerabilities from the onset. There is also the need for organizations to address insider threats, which might be a compromised engineer or simply poorly trained engineers. Organizations can mitigate these threats by having codified source control processes with appropriate authentication, running static and dynamic tests on code, as well as looking for exposed secrets.
Organizations should also implement nightly builds and security regression testing to recognize and address flaws and vulnerabilities. Development efforts shouldn’t be ad hoc and should be mapped to specific system requirements with associated security testing to avoid feature creep which can introduce risk.
Code reviews should be prioritized, especially critical code to ensure fundamentals such as cryptography are in place and there are requirements for privilege escalation and access protection for resources. It isn’t just the code that must be secured but also the development environment. There has been notable incidents such as SolarWinds where the development environment can be compromised and poison downstream consumers so systems, such as developers endpoints, source code repositories and CI/CD pipelines, should be threat modeled and have vulnerability assessments conducted.
Open-source software (OSS) introduces its own unique risk and the guidance recommends using dedicated systems to download, scan and perform recurring checks on OSS components that internal development teams can use. This concept is also advocated by NIST in its Improving the Nation’s Cybersecurity executive order guidance for Section 4 and has been dubbed as continuous packaging.
Another practice emphasized is securing the developer environment, using secure development build configurations and secure third-party software toolchains and libraries. Development systems should be hardened and only used for development purposes, without internet access, and only with pre-approved tooling and software. The guidance recommends vetting third-party modules for CVEs against the NIST National Vulnerability Database (NVD). Tooling and automation can help facilitate this process and can even be done as part of the integrated development environment (IDE) using security dependency analyzers and similar tooling to identify vulnerabilities.
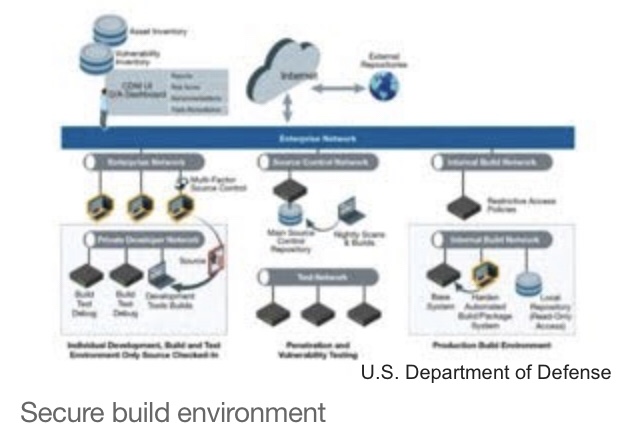
Hardening the build environment is critical, including the developer network, enterprise network and internal build environments. This mitigates threats being introduced from the internet and external malicious actors as well as integrity and validation measures to validate that malicious activities have not occurred to compromise products.
Software components should be sourced from known trusted suppliers that meet organizational requirements and validated through methods such as SPDX or CycloneDX SBOM formats as well as the suppliers responsiveness to vulnerabilities with established methods for vulnerability reporting.
Securing the Software Supply Chain’s guidance goes beyond hardening the build environment to make recommendations such as using hermetic reproducible builds as well. This means fully declared build steps, immutable references, and no network access, as well as identical outputs and artifacts regardless of variable metadata changes to things such as timestamps.
Software should be delivered securely, including an SBOM of final composition to the customers. As part of package validation customers can use binary analysis outputs to ensure only intended software components are in place. To address compromises of software packages and updates, both product and components can make use of hashes and digital signatures for product distribution, components and upgrades. Organizations should also take steps to mitigate compromises of the distribution system itself. This can include applying security measures to repositories and package managers as well as using secure transport layer mechanisms.
Other resources for securing the software supply chain
The guidance includes a crosswalk among various scenarios with developers, suppliers and customers to specific practices outlined in SSDF. It also includes a mapping of dependencies and artifacts that exist among the supplier, third-party suppliers and the end customer.
A mapping to the SLSA framework shows how specific recommendations in the guidance map to the various levels of SLSA, ranging from L1 to L4. Lastly, there’s a comprehensive list of artifacts and checklists to be used throughout the SDLC and a list of informative references such as the cyber executive order, DoD and NIST documentation as well as industry organizations such as OWASP.
This secure software supply chain guidance is a critical resource that will undoubtedly be adopted by the industry as a go-to reference for organizations looking to bolster their software supply chain practices for both software producers and consumers. With this document taking a developer-centric focus, the industry would be well advised to look for the subsequent guidance, which will focus on software suppliers and consumers.[ Learn how to track and secure open source in your enterprise.
April 16, 2018, Updated April 20, 2018
Summary. There’s a new kind of leadership taking hold in organizations. Strikingly, these new leaders don’t like to be called leaders, and none has any expectation that they will attract “followers” personally — by dint of their charisma, status in a hierarchy, or access to resources. Instead, their method is to get others excited about whatever problem they have identified as ripe for a novel solution. Having fallen in love with a problem, they step up to leadership — but only reluctantly and only as necessary to get it solved. Leadership becomes an intermittent activity as people with enthusiasm and expertise step up as needed, and readily step aside when, based on the needs of the project, another team member’s strengths are more central. Rather than being pure generalists, leaders pursue their own deep expertise, while gaining enough familiarity with other knowledge realms to make the necessary connections. They expect to be involved in a series of initiatives with contributors fluidly assembling and disassembling.close
In front of a packed room of MIT students and alumni, Vivienne Ming is holding forth in a style all her own. “Embrace cyborgs,” she calls out, as she clicks to a slide that raises eyebrows even in this tech-smitten crowd. “Really. Fifteen to 25 years from now, cognitive neuroprosthetics will fundamentally change the definition of what it means to be human.”
She’s referring to the work that interests her most these days, as cofounder of machine learning company Socos and a visiting scholar at UC Berkeley’s Center for Theoretical Neuroscience. (“So — can I literally jam things in your brain and make you smarter? If you’re curious, the answer is unambiguously yes.”) But the talkhas covered a lot more than this, as Ming has touched on many initiatives and startups she’s been involved with, all solving problems at the intersection of advanced technology, learning, and labor economics.
She’s an entrepreneur, a CEO, and a teacher — all leadership roles — but when we ask her about her leadership style, she demurs. “What I’ve learned about myself as a leader, as an executive, is — I’ll be blunt — I’m a pretty mediocre manager. I try to do the right things, but I’m much more focused on problems than I am on people, and that’s not always that healthy.” While she’s utterly confident in herself, she just doesn’t identify as top management. She’s happier to think of herself as a data scientist, a computer geek. She loves talking about hacks she’s pulled off — like the alterations she made to her diabetic son’s medical devices, so she could merge all their data to produce a predictive model. Now, she gets an alert an hour in advance if a spike or drop is coming in his blood glucose level. This is an unprecedented, and highly valuable, thing. “Turns out, it would have broken several federal laws if I had done this with patients as a medical device company,” she laughs.
Ming is a tech optimist, believing that all kinds of previously intractable problems will be able to be solved as the tool kit for addressing them is developed. And she’s decided her best way of contributing to that progress is to keep honing her individual-contributor skills. “For a long time, I tried to be the whole package. I put a lot of energy into making certain that I was shepherding everyone along, doing all the right things for my teams. Then I realized: You know what? If I can get some people that are really good at the things that I’m not, then I can focus on my strengths. And my strengths are in creative problem solving — all the way down to writing the code myself.”
The attitude she’s espousing doesn’t really map to the traditional image of the enterprise leader, or to what typically gets taught in leadership development programs. Yet there is no denying that truly awesome stuff gets done thanks to Ming’s abilities to see possibilities and assemble talent. There’s a reason she’s been invited by the MIT Leadership Center to speak. We think her approach to taking on big problems will resonate with this crowd.
Over the past year, as faculty director and executive director of the MIT Leadership Center, we have been trying to put a finer point on a distinctive style of leadership we keep seeing all around us. We weren’t sure if it was because we spent so much time with MIT-trained people, or if there was a much more widespread shift under way, but the people we saw driving impactful, world-changing initiatives just didn’t look like old-school leadership material — and didn’t seem to want to. Cautiously, we called it problem-led leadership, and launched into all the interviewing, case studying, and literature review that goes into a leadership research project.
To make a long story very short, we found several common threads in the work of problem-led leaders. Most striking is that none of these leaders has any expectation that they will attract “followers” personally — by dint of their charisma, status in a hierarchy, or access to resources. Instead, their method is to get others excited about whatever problem they have identified as ripe for a novel solution. Having fallen in love with a problem, they step up to leadership — but only reluctantly, and only as necessary to get it solved. As Ming says about her entrepreneurial ventures, “The only reason I do it is because it is an amazingly effective way to have an impact on the world.”
From this “problem-led” beginning, other differences follow. Leadership becomes an intermittent activity as people with enthusiasm and expertise step up as needed, and readily step aside when, based on the needs of the project, another team member’s strengths are more central. Rather than being pure generalists, leaders pursue their own deep expertise, while gaining enough familiarity with other knowledge realms to make the necessary connections. No one assumes that the life of a team, or even organization, will be prolonged for its own sake. They expect to be involved in a series of initiatives with contributors fluidly assembling and disassembling. It’s a key leadership talent, then, to know how to put together a team. To tackle a problem, they need to find the right talent and to convince others that their project offers the chance to be part of a breakthrough. (Talented people always have other options, after all.)
Back to Vivienne Ming. In an interview after her talk, she is pressed again to describe the role she plays in her ambitious projects and she pauses to reflect. “I lead by leading,” she begins, and then quickly worries that this “sounds a little self-aggrandizing.” She clarifies what she means. “I get out there, and I solve problems. And I hope that motivates my colleagues to do the same.”
It’s the leadership that dare not speak its name — we’ve heard this discomfort with the term expressed so many times that we now call people like Ming “anti-leadership leaders.” But while we started out thinking it was “MIT style,” we now believe it is a style that is generally trending in the world, at least in settings where a premium is placed on innovation. People like Vivienne Ming can be found in many places, getting focused on opportunities, getting others energized and organized, and getting problems solved. Call them what you want, but what they’re doing is leading.
Article link: https://hbr.org/2018/04/the-power-of-leaders-who-focus-on-solving-problems?
Editor’s note: We’ve updated this article to clarify that Vivienne Ming did not actually break any federal laws.
- Deborah Ancona is the Seley Distinguished Professor of Management at MIT’s Sloan School of Management and the founder of the MIT Leadership Center.
- Hal Gregersen is Executive Director of the MIT Leadership Center, a Senior Lecturer in Leadership and Innovation at the MIT Sloan School of Management, a Thinkers50 globally ranked management thinker, and the founder of the 4-24 Project. He is also the author of Questions Are the Answer: A Breakthrough Approach to Your Most Vexing Problems at Work and in Life and the coauthor of The Innovator’s DNA: Mastering the Five Skills of Disruptive Innovators.
By ALEXANDRA KELLEYSEPTEMBER 7, 2022
The President’s Council of Advisors on Science and Technology introduced new advice to help successfully implement the CHIPS Act and develop an advanced U.S. semiconductor market.
The President’s Council of Advisors on Science and Technology presented several recommendations focused on how to support and foster a strong domestic semiconductor industry within the U.S., following the passage of the Semiconductor and CHIPS Science Act in August.
Speaking in a public session, members of the PCAST introduced investigative findings that can help support a strong manufacturing economy to spur both revenue growth and global leadership in the semiconductor market.
“We’ve been…really looking at the key points of the CHIPS Act, particularly as it relates to the research and development investment,” PCAST member Lisa Su said. “So the purpose of our report is to really focus on ‘how do we revitalize the semiconductor ecosystem in the face of significant global competition?’”
The ten recommendations released today are broadly tailored toward implementing the National Semiconductor Technology Center, as stipulated in the CHIPS Act, as well as cultivating steady workforce talent for sustainable market sector growth.
The CHIPS and Science Act will allocate a total of $11 billion in government funding to help grow a sustainable domestic semiconductor manufacturing and research industry in the U.S.
Su introduced the first five recommendations, including building a coalition of public-private partnerships, developing a workforce specializing in microelectronics, reducing startup business barriers to entry, setting a national semiconductor research agenda, and supporting immigration related to semiconductor-based employment.
Fellow PCAST working group member Bill Dally introduced the second half of recommendations, which advocate for the creation of chiplet devices—tiny processing units that can be combined to form a more complex system—at the forthcoming NSTC.
Dally said that the chiplet priority will help smaller businesses participate in the U.S.’s burgeoning semiconductor industry.
The recommendations also direct the Department of Commerce to allocate over $500 million in federal funding to NSTC and further delegate 30% to 50% of this money to research, incorporating research challenges into NSTC’s initiatives. The NSTC would then have to publish investment figures and evaluate performance metrics.
Some of the research areas the working group want the NSTC to focus on are supercomputing, advanced logic and memory processing, and life sciences applications and use cases.
Su and Dally also emphasized the importance of public and private organizations collaborating on research and development projects.
Su said that cultivating a strong accompanying workforce is critical to a sustainable semiconductor industry and a high priority within internal PCAST discussions.
These recommendations follow a letter sent by PCAST members to President Biden in August, previewing the recommendations announced today. Su commented that the report builds out more detail into the initial bullet points included in the letter.
“I think we’re very excited about the broad coalition for the NSTC,” she said. “I think the opportunity there is to have a very geographically diverse…experience across both the entire semiconductor ecosystem.”
Article link: https://www.nextgov.com/policy/2022/09/white-house-team-unveils-new-recommendations-us-semiconductor-industry-growth/376834/

PRESS RELEASE | Sept. 7, 2022
The National Security Agency (NSA) released the “Commercial National Security Algorithm Suite 2.0” (CNSA 2.0) Cybersecurity Advisory (CSA) today to notify National Security Systems (NSS) owners, operators and vendors of the future quantum-resistant (QR) algorithms requirements for NSS — networks that contain classified information or are otherwise critical to military and intelligence activities.
A cryptanalytically-relevant quantum computer (CRQC) would have the potential to break public-key systems (sometimes referred to as asymmetric cryptography) that are used today. Given foreign pursuits in quantum computing, now is the time to plan, prepare and budget for a transition to QR algorithms to assure sustained protection of NSS and related assets in the event a CRQC becomes an achievable reality.
“This transition to quantum-resistant technology in our most critical systems will require collaboration between government, National Security System owners and operators, and industry,” said Rob Joyce, Director of NSA Cybersecurity. “Our hope is that sharing these requirements now will help efficiently operationalize these requirements when the time comes.”
The Director of NSA is the National Manager for NSS and therefore issues guidance for NSS. The algorithms in CNSA 2.0 are an update to those in the currently required Commercial National Security Algorithm Suite (now referred to as CNSA 1.0) listed in CNSSP 15, Annex B (released in 2016). The CNSA 2.0 algorithms have been analyzed as secure against both classical and quantum computers, and they will eventually be required for NSS.
NSA’s CNSA 2.0 algorithm selections were based on the National Institute of Standards and Technology’s (NIST) recently announced selections for standardization for quantum-resistant cryptography, but there are neither final standards nor FIPS-validated implementations available yet.
NSA urges NSS owners and operators to pay attention to NIST selections and to the future requirements outlined in CNSA 2.0, while CNSA 1.0 compliance continues to be required in the interim.
“We want people to take note of these requirements to plan and budget for the expected transition, but we don’t want to get ahead of the standards process,” said Joyce.
NSS owners and operators should not deploy QR algorithms on mission networks until they have been vetted by NIST and National Information Assurance Partnership (NIAP) as required in CNSSP-11.There will be a transition period, and NSA will be transparent about NSS transition requirements.
For additional information, the CNSA 2.0 CSA is accompanied by a cybersecurity information sheet (CSI), “The Commercial National Security Algorithm Suite 2.0 and Quantum Computing FAQ.” This CSI provides updated answers to quantum-related FAQs that were previously published on NSA’s website.
Visit our full library for more cybersecurity information and technical guidance.
From the factory floor to delivery robots, innovation is moving fast with real-time data processing.
Luxury auto maker Audi is driving full-throttle toward Industry 4.0, using AI inference and computer vision on the factory floor with autonomous robot welders that can react in real time and fix issues that may arise when welding the frame of a car. That’s just one example of how the company is moving toward realizing its ultimate vision of creating smart factories with a scalable and flexible platform that will enable data analytics, communications and processing at the edge, powered by 5G.
In the past, welding required a lot of manual intervention and inspection to ensure sufficient quality, says Nick McKeown, senior vice president and general manager of the network and edge group at Intel, which is working with Audi. Now, with cameras reviewing the quality of the weld the need for human intervention has greatly decreased.
“If you want, or need to process data in real time, you actually have to bring the compute to the data, to the point of data creation and data consumption.”
Sandra Rivera
“Edge computing is taking the technology resources we’ve been developing over many years for the computing industry and using them to analyze and process data at the edge”, McKeown says. The concept of edge computing is storing data closer to where it is generated and used—like the factory floor–instead of in the cloud, which means it can be processed in real or near real time.
“If you want, or need to process data in real time, you actually have to bring the compute to the data, to the point of data creation and data consumption”, explains Sandra Rivera, executive vice president and general manager of the datacenter and AI group at Intel. Not having to move large amounts of data enhances security, and increases reliability while reducing latency. And because data is kept more private there is an additional layer of data sovereignty available when needed, adds McKeown.
GROWING OPPORTUNITIES FOR 5G AT THE EDGE
As telecommunication operators continue rolling out 5G infrastructure, “there are opportunities that start to emerge because the data rate, the latency, the control that you have over the 5G network means that we can start to use it for applications that we would not have previously thought suitable for a cellular technology,” McKeown says.
In the Audi factory example, controlling a robot arm in real time requires either a cable, a wire, an ethernet cable that connects to it to guarantee connectivity, the data rate that is needed, and the low latency control—or it has to be replaced with a wireless link, he says.
“Now imagine that robot is moving around. You really don’t want a wire trailing around on the floor for other robots to trip over. You’d really like it to be a wireless link”, McKeown says. “And the problem is, wi-fi hasn’t really gotten there just yet in terms of the quality that you would want. What 5G, in particular private 5G, offers is a much more reliable, much lower latency, much more controlled-by-software experience.”

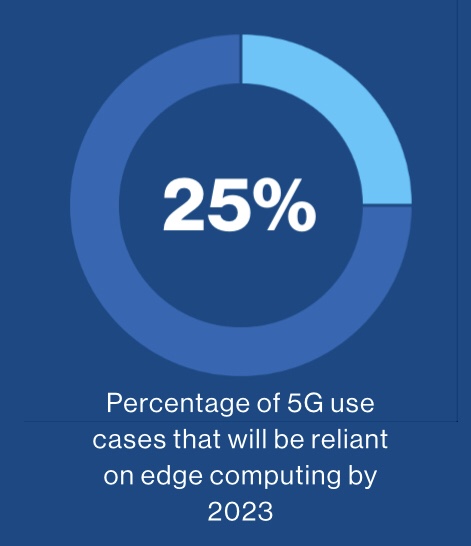

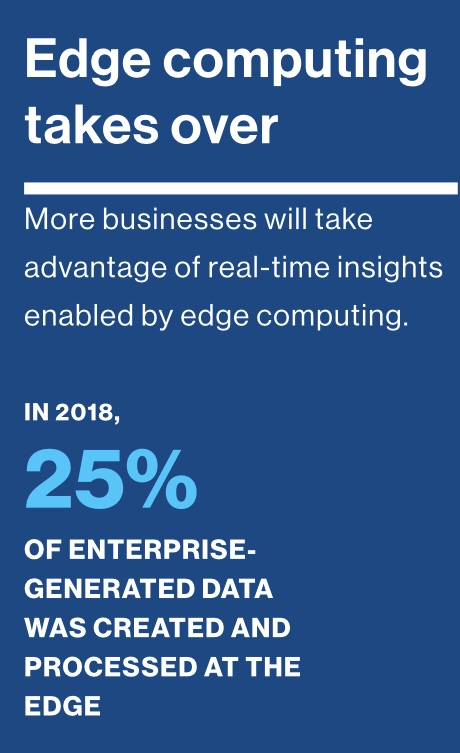
According to a recent Gartner report, “Predicts 2022: The Distributed Enterprise Drives Computing to the Edge”, 5G is the fastest growing segment in the wireless network infrastructure market—and global revenue will likely reach $23.2 billion in 2022. Gartner has further predicted that by 2025, more than 50% of enterprise-generated data will be processed outside a traditional centralized data center or cloud.
Deploying AI applications at the edge with 5G has the potential to generate new revenue sources—and position AI as standard bearer for 5G. Opportunities range across industries including smart manufacturing, smart cities, rich media, enhanced retail logistics, and automated warehouses, among others.
KEEPING AN EYE ON OBSTACLES
Because AI is a highly compute-intensive process it is critical to have the right infrastructure optimized for the unique demands of AI workloads at the edge. Another consideration says Rivera is that “Computing takes power. And we know that we have to work within restricted power envelopes when we’re deploying on the edge and also computing on small form factor devices, or in areas where you have a hostile environment,” Rivera notes.
“Every day, every week, I see a number of different use cases that our customers or their customers have put in place that we would never have thought of.”
Nick McKeown
For example, if wireless infrastructure is deployed across the globe, that connectivity will exist in both the coldest and the hottest places on earth, she says. “We design and develop our products on our own, as well as together with customers, for much more power-efficient types of platforms to address that particular set of issues.”
There’s always more work to do, because there’s always more computing people want to do on an ever-limited power budget, Rivera says.
“The other big limitation we see is in legacy applications,” she adds. In the case of deploying internet of things (IoT) devices, there is such a broad range of market segments each customer’s environment and individual needs have to be considered.
“Our challenge is, how do we give application developers an easy way to migrate and integrate AI into their legacy applications? When we look at how to do that, first of all, we have to understand that vertical and work closely with customers.”

THE POSSIBILITIES ARE ENDLESS
The combination of AI and 5G will transform the enterprise and accelerate economic growth, as 5G networks provide the backbone, scalable bandwidth, and remote compute resources to process increasing volumes of data that will fuel the proliferation of AI.
If someone had told McKeown a few years ago there would be smart delivery bots in cities and towns being driven by autonomous vehicles that would walk down sidewalks, climb stairs, and deliver right to someone’s door, he would have said that might happen maybe 15 or 20 years from now. Yet, those applications are being tested and rolled out right now.
And that’s just one visible example we will see. That automation and control is happening in warehouses and in factories because of sensors and actuators running on a 5G network. The combination is going to create “a sort of a Cambrian explosion of new ideas” that if we were to try to predict, we would get wrong, McKeown says.
Whatever we think is going to happen by combining new IoT applications with public and private 5G, as well as AI and machine learning at the edge, “will actually shock us”, he says. “And that’s because it’s the wild pioneering west, and it’s wonderful, it’s exciting, it’s terrifying, it’s growing, it’s expanding. Every day, every week, I see a number of different use cases that our customers or their customers have put in place that we would never have thought of.”
Intel technologies may require enabled hardware, software or service activation. No product or component can be absolutely secure. Your costs and results may vary. Performance varies by use, configuration and other factors.
Article link: https://www.technologyreview.com/2022/04/13/1049529/with-5g-ai-at-the-edge-promises-a-compute-everywhere-future/?
As the Department of Veterans Affairs looks to finalize its contract with Cerner, the agency has laid out some comprehensive expectations for the EHR vendor that emphasize change management and interoperability.
Documents released by the VA last week outlined some specific requirements for Cerner, which was tapped to overhaul the agency’s EHR system in June. The rollout is expected to cost at least $10 billion and is poised to consume the next decade.
Last week, Politico reported that the final contract, which VA officials expected to complete by the end of November, was held up because of lingering interoperability concerns from Secretary David Shulkin, M.D.
RELATED: Secretary Shulkin on Cerner integration: ‘This is a new VA’
Unsurprisingly, interoperability and data exchange make up a significant part of the VA’s focus. A performance work statement (PWS) finalized by VA officials in October states that the EHR system will “become the authoritative source of clinical data” for the 168-hospital system to support “improved population health, patient safety, and quality of care provided by VA.” Although the impetus of the sole-source contract was to better align the VA with the Department of Defense, the agency clearly expects Cerner to improve information exchange with community health providers.
The PWS features specific requirements for Cerner, including an interoperability plan delivered to the VA each year. At minimum, Cerner’s solution must be able to do the following:
- Allow the VA to release and consume a veteran’s “complete longitudinal health record” with DOD and community partners
- Share interactive care plans
- Share URL-based images with community and academic partners’ systems
- Connect with interoperable networks like eHealth Exchange, CareQuality, CommonWellHealth Alliance, Direct Trust and the National Association for Trusted Exchange
- Allow providers to collaborate via secure email within the EHR workflow.
Within two years of awarding the contract, the VA also expects Cerner to:
- Connect with the DOD and community providers to provide a referral management solution
- Notify providers when a veteran is admitted, discharged or transferred
- Identify and manage veterans at a high risk for suicide.
The VA also referenced its “digital health platform/digital veteran’s platform,” a project that has been in the works for several years. The agency calls on Cerner to “work in good faith” to integrate EHR data into the platform, including through an “API gateway.”
RELATED: VA’s EHR transition could take up to a decade
The PWS makes numerous references to organizational change management, an issue that Shulkin has repeatedly emphasized as a critical aspect of the EHR deployment. The VA wants Cerner to provide localized and national change management strategy using credentialed clinicians, change management specialists and project managers.
The PWS states that Cerner will also be responsible for identifying change management “hot spots” and pain points that might hinder adoption, and conduct site assessments to determine readiness.
Article link: https://www.fiercehealthcare.com/ehr/va-cerner-wishlist-interoperability-digital-health-platform-change-management

The US Army has announced that it will create an office next year dedicated to overseeing the country’s offensive cyber and space capabilities.
Offensive cyber refers to cyberspace operations intended to project power through application of force in or through cyberspace.
Called the Program Manager Cyber and Space, the office will be responsible for testing and fielding cutting-edge equipment, such as aerial jamming pods, biometric information systems, and battlefield navigation tools.
Establishing a new office is reportedly an important move due to increasing workloads and demands related to cyber and space.
“Because we’ve seen mission growth in that area, we’re going to spin off,” Mark Kitz from the Program Executive Office for Intelligence, Electronic Warfare and Sensors said.
The new cyber and space office will be led by a colonel.
Last month, the US Army announced the establishment of a “triad” that will combine space, cyber, and special operations capabilities to conceptualize effective battlefield strategies for modern warfare.
Article link: https://www-thedefensepost-com.cdn.ampproject.org/c/s/www.thedefensepost.com/2022/09/01/us-army-offensive-cyber-office/amp/
August 30, 2022 Contributor: Lori Perri
CIOs must possess five key characteristics to lead and deliver on digital transformation.
In short:
- CIOs must rethink their role as digital leaders, due to workplace disruptions and ongoing changes to business, operating and IT delivery models.
- When CIOs deal with uncertainty and change, they are more effective business leaders.
- Digital transformation requires technology leaders to reinvent their approach, rather than simply respond or react to business requirements.
As CIOs face ever-expanding responsibilities in their roles, they must remain effective in dealing with uncertainty and change. Digital not only disrupts business, it also transforms leadership. Gartner research shows that successful digital business initiatives demand paradigm shifts in technology leadership and new ways of thinking and approaching challenges.
Download Now: The IT Roadmap for Digital Business Transformation
“CIOs know they must function with flexibility and agility to thrive in the dynamic world. The realities of a disrupted workplace, business model transformations, operating model changes and IT delivery model changes, all force fundamental shifts in the activities and responsibilities of the given role of a CIO,” says Apoorva Chhabra, principal analyst at Gartner. “All of this also creates opportunities for the CIOs to expand their executive leadership.”

How to be a successful digital leader: Five characteristics to adopt
Business transformation can be accelerated or derailed depending on how effective leaders are at transforming themselves. Executive technology leadership must anticipate digital opportunities and threats, use technology to adapt to changing conditions, and find leverage and value from disruption. To become an effective digital CIO, it is important to understand and adopt these five characteristics:
No. 1: Neophilia: A Tendency to Like Anything New; Love of Novelty
Neophiliacs are naturally curious and attracted to new things. They seek to explore and find new ways to create value.
Neophiliacs welcome varying ideas from others that shift from the past, a key component of any successful digital transformation. A neophiliac asks, “What do we want to achieve?” rather than “What have we got?”, rejecting current assumptions. The ultimate objective drives solutions to seemingly complex problems.
Effective digital CIOs also embrace innovation. They tend to have a high degree of creativity, defined as the ability to connect seemingly unrelated areas.
See Playbook: Recession Advice for IT
No. 2: Develop New Opportunities: Invent, but Also Copy
Digital leaders don’t necessarily invent and innovate all the time. In reality, successful digital leaders appreciate exactly where their organizations need to be different, where they can copy and where they should improvise.
Successful digital leaders are selective, doubling down on particular areas that deliver a greater advantage, acceleration or value contribution. In areas where they do not see any clear advantage, digital leaders are comfortable copying and improvising based on already established methods. Ineffective leaders lack focus, and tend to be all over the place with innovation.
No. 3: Pioneer New Opportunities: Look Beyond Industry Boundaries
This leadership characteristic is personified by what Gartner labels “digital dragons,” who actively seek value beyond any specific industry and create whole new industries as they redefine value in any industry they pursue. Strategies and digital adoption plans are often made only as a result of a market disruption mindset.
Effective digital leaders see threats that aren’t necessarily distinct, and make decisions while maintaining a clear vision of their industry’s future, as opposed to considering the industry static or unchanging.
No. 4: Seek New Value Creation Opportunities: Never Consider Digital to Be the Outcome
Successful digital leaders understand that digital is a means, not an end, and that simply making something digital does not necessarily increase its value. It may actually decrease it.
Digital technology tools either change the way people work, or change the products and services provided, whether through extending the life cycle of a product, adding digital features or providing goods as a service.
Consider the logic behind the product/service’s value proposition before implementing digital tools. Ask how the digital offering drives the business outcomes of customer centricity, greater market share and revenue enhancement. Use digital to boost your value proposition such as on-demand services, hyperpersonalization, dynamic pricing and real-time applications.
No. 5: Focus on Technology-Driven Opportunities: Geek Out on Technology
A successful leader possesses a deep understanding of the technology underlying their business. It’s challenging to get value out of technology if you don’t understand what it does or doesn’t do.
CIOs need to enable a technology-enriched environment, where learning is engaging, collaborative and customized. They should follow —geek out on — technology as a passion, as well as an essential way to stay innovative and relevant in the crowded and competitive business spaces.
Article link: https://www.gartner.com/en/articles/top-five-characteristics-of-successful-digital-transformation-leaders?
June 20, 2017

Summary. Culture is like the wind. It is invisible, yet its effect can be seen and felt. When it is blowing in your direction it makes for smooth sailing. When it is blowing against you, everything is more difficult. For organizations seeking to become more adaptive and innovative, culture change is often the most challenging part of the transformation. But culture change can’t be achieved through top-down mandate. It lives in the collective hearts and habits of people and their shared perception of “how things are done around here.” Culture change needs to happen through a movement, not a mandate. To create a movement in your organization, start by framing the issue in terms that stir emotion and incite action; then mobilize more supporters by demonstrating quick wins. Broadcast these wins to an even wider audience by leveraging employees’ social networks, and using symbolism and pockets of innovation to keep momentum going. It’s important to start with actions, not new mission statements or company structures, because culture change only happens when people take action. Show people the change you want to see.
Culture is like the wind. It is invisible, yet its effect can be seen and felt. When it is blowing in your direction, it makes for smooth sailing. When it is blowing against you, everything is more difficult.
For organizations seeking to become more adaptive and innovative, culture change is often the most challenging part of the transformation. Innovation demands new behaviors from leaders and employees that are often antithetical to corporate cultures, which are historically focused on operational excellence and efficiency.
But culture change can’t be achieved through top-down mandate. It lives in the collective hearts and habits of people and their shared perception of “how things are done around here.” Someone with authority can demand compliance, but they can’t dictate optimism, trust, conviction, or creativity.
At IDEO, we believe that the most significant change often comes through social movements, and that despite the differences between private enterprises and society, leaders can learn from how these initiators engage and mobilize the masses to institutionalize new societal norms.
Dr. Reddy’s: A Movement-Minded Case Study
One leader who understands this well is G.V. Prasad, CEO of Dr. Reddy’s, a 33-year-old global pharmaceutical company headquartered in India that produces affordable generic medication. With the company’s more than seven distinct business units operating in 27 countries and more than 20,000 employees, decision making had grown more convoluted and branches of the organization had become misaligned. Over the years, Dr. Reddy’s had built in lots of procedures, and for many good reasons. But those procedures had also slowed the company down.
Prasad sought to evolve Dr. Reddy’s culture to be nimble, innovative, and patient-centered. He knew it required a journey to align and galvanize all employees. His leadership team began with a search for purpose. Over the course of several months, the Dr. Reddy’s team worked with IDEO to learn about the needs of everyone, from shop floor workers to scientists, external partners, and investors. Together they defined and distilled the purpose of the company, paring it down to four simple words that center on the patient: “Good health can’t wait.”
But instead of plastering this new slogan on motivational posters and repeating it in all-hands meetings, the leadership team began by quietly using it to start guiding their own decisions. The goal was to demonstrate this idea in action, not talk about it. Projects were selected across channels to highlight agility, innovation, and customer centricity. Product packaging was redesigned to be more user-friendly and increase adherence. The role of sales representatives in Russia was recast to act as knowledge hubs for physicians, since better physicians lead to healthier patients. A comprehensive internal data platform was developed to help Dr. Reddy’s employees be proactive with their customer requests and solve any problems in an agile way.
At this point it was time to more broadly share the stated purpose — first internally with all employees, and then externally with the world. At the internal launch event, Dr. Reddy’s employees learned about their purpose and were invited to be part of realizing it. Everyone was asked to make a personal promise about how they, in their current role, would contribute to “good health can’t wait.” The following day Dr. Reddy’s unveiled a new brand identity and website that publicly stated its purpose. Soon after, the company established two new “innovation studios” in Hyderabad and Mumbai to offer additional structural support to creativity within the company.
Prasad saw a change in the company culture right away:
After we introduced the idea of “good health can’t wait,” one of the scientists told me he developed a product in 15 days and broke every rule there was in the company. He was proudly stating that! Normally, just getting the raw materials would take him months, not to mention the rest of the process for making the medication. But he was acting on that urgency. And now he’s taking this lesson of being lean and applying it to all our procedures.
What Does a Movement Look Like?
To draw parallels between the journey of Dr. Reddy’s and a movement, we need to better understand movements.
We often think of movements as starting with a call to action. But movement research suggests that they actually start with emotion — a diffuse dissatisfaction with the status quo and a broad sense that the current institutions and power structures of the society will not address the problem. This brewing discontent turns into a movement when a voice arises that provides a positive vision and a path forward that’s within the power of the crowd.
What’s more, social movements typically start small. They begin with a group of passionate enthusiasts who deliver a few modest wins. While these wins are small, they’re powerful in demonstrating efficacy to nonparticipants, and they help the movement gain steam. The movement really gathers force and scale once this group successfully co-opts existing networks and influencers. Eventually, in successful movements, leaders leverage their momentum and influence to institutionalize the change in the formal power structures and rules of society.
Practices for Leading a Cultural Movement
Leaders should not be too quick or simplistic in their translation of social movement dynamics into change management plans. That said, leaders can learn a lot from the practices of skillful movement makers.
Frame the issue. Successful leaders of movements are often masters of framing situations in terms that stir emotion and incite action. Framing can also apply social pressure to conform. For example, “Secondhand smoking kills. So shame on you for smoking around others.”
In terms of organizational culture change, simply explaining the need for change won’t cut it. Creating a sense of urgency is helpful, but can be short-lived. To harness people’s full, lasting commitment, they must feel a deep desire, and even responsibility, to change. A leader can do this by framing change within the organization’s purpose — the “why we exist” question. A good organizational purpose calls for the pursuit of greatness in service of others. It asks employees to be driven by more than personal gain. It gives meaning to work, conjures individual emotion, and incites collective action. Prasad framed Dr. Reddy’s transformation as the pursuit of “good health can’t wait.”
Demonstrate quick wins. Movement makers are very good at recognizing the power of celebrating small wins. Research has shown that demonstrating efficacy is one way that movements bring in people who are sympathetic but not yet mobilized to join.
When it comes to organizational culture change, leaders too often fall into the trap of declaring the culture shifts they hope to see. Instead, they need to spotlight examples of actions they hope to see more of within the culture. Sometimes, these examples already exist within the culture, but at a limited scale. Other times, they need to be created. When Prasad and his leadership team launched projects across key divisions, those projects served to demonstrate the efficacy of a nimble, innovative, and customer-centered way of working and of how pursuit of purpose could deliver outcomes the business cared about. Once these projects were far enough along, the Dr. Reddy’s leadership used them to help communicate their purpose and culture change ambitions.
Harness networks. Effective movement makers are extremely good at building coalitions, bridging disparate groups to form a larger and more diverse network that shares a common purpose. And effective movement makers know how to activate existing networks for their purposes. This was the case with the leaders of the 1960s civil rights movement, who recruited members through the strong community ties formed in churches. But recruiting new members to a cause is not the only way that movement makers leverage social networks. They also use social networks to spread ideas and broadcast their wins.
Leadership at Dr. Reddy’s did not hide in a back room and come up with their purpose. Over the course of several months, people from across the organization were engaged in the process. The approach was built on the belief that people are more apt to support what they have a stake in creating. And during the organization-wide launch event, Prasad invited all employees to make the purpose their own by defining how they personally would help deliver “good health can’t wait.”
Create safe havens. Movement makers are experts at creating or identifying spaces within which movement members can craft strategy and discuss tactics. Such spaces have included beauty shops in the Southern U.S. during the civil rights movement, Quaker work camps in the 1960s and 1970s, the Seneca Women’s Encampment of the 1980s and early 1990s. These are spaces where the rules of engagement and behaviors of activists are different from those of the dominant culture. They’re microcosms of what the movement hopes will become the future.
The dominant culture and structure of today’s organizations are perfectly designed to produce their current behaviors and outcomes, regardless of whether those outcomes are the ones you want. If your hope is for individuals to act differently, it helps to change their surrounding conditions to be more supportive of the new behaviors, particularly when they are antithetical to the dominant culture. Outposts and labs are often built as new environments that serve as a microcosm for change. Dr. Reddy’s established two innovation labs to explore the future of medicine and create a space where it’s easier for people to embrace new beliefs and perform new behaviors.
Embrace symbols. Movement makers are experts at constructing and deploying symbols and costumes that simultaneously create a feeling of solidarity and demarcate who they are and what they stand for to the outside world. Symbols and costumes of solidarity help define the boundary between “us” and “them” for movements. These symbols can be as simple as a T-shirt, bumper sticker, or button supporting a general cause, or as elaborate as the giant puppets we often see used in protest events.
Dr. Reddy’s linked its change in culture and purpose with a new corporate brand identity. Internally and externally, the act reinforced a message of unity and commitment. The entire company stands together in pursuit of this purpose.
The Challenge to Leadership
Unlike a movement maker, an enterprise leader is often in a position of authority. They can mandate changes to the organization — and at times they should. However, when it comes to culture change, they should do so sparingly. It’s easy to overuse one’s authority in the hopes of accelerating transformation.
It’s also easy for an enterprise leader to shy away from organizational friction. Harmony is generally a preferred state, after all. And the success of an organizational transition is often judged by its seamlessness.
In a movements-based approach to change, a moderate amount of friction is positive. A complete absence of friction probably means that little is actually changing. Look for the places where the movement faces resistance and experiences friction. They often indicate where the dominant organizational design and culture may need to evolve.
And remember that culture change only happens when people take action. So start there. While articulating a mission and changing company structures are important, it’s often a more successful approach to tackle those sorts of issues after you’ve been able to show people the change you want to see.
- BWBryan Walker is a Partner and Managing Director at IDEO San Francisco.
- SSSarah A. Soule is the Morgridge Professor of Organizational Behavior an Senior Associate Dean for Academic Affairs at the Stanford Graduate School of Business. She studies organizational theory, social movements, and political sociology including topics like gender bias in the craft beer industry and the impact of women’s protest on congressional attention.
Article link: https://hbr.org/2017/06/changing-company-culture-requires-a-movement-not-a-mandate?

