healthcarereimagined

Envisioning healthcare for the 21st century

  • About
  • Economics

MITRE Recommends Comprehensive Approach to Modernize Legacy Systems – Nextgov

Posted by timmreardon on 04/03/2023
Posted in: Uncategorized.

The recommendations focus on executable actions for the Office of Management and Budget, agencies, Congress and industry

MITRE made 10 recommendations this week to help the federal government modernize legacy systems, citing that “significant numbers of critical federal information technology systems that provide vital support to agencies’ missions are operating with known security vulnerabilities and unsupported hardware and software.”

According to the March 29recommendations, the government must move away from legacy systems to fully leverage technology and fulfill critical missions. The recommendations focus on execution and were directed at the Office of Management and Budget, agencies, Congress and industry.

For example, MITRE suggests OMB provide guidance on legacy systems inventories and IT modernization plans in addition to progress transparency mechanisms. Congress should introduce legislation to reduce legacy IT and should make adjustments to the Federal Information Technology Acquisition Reform Act—or FITARA—scorecard by adding an IT Modernization Planning and Delivering category.

Meanwhile, agencies should develop inventories, modernization plans and budgets to support this, in addition to progress reports that detail acquisition and legacy system retirement. Lastly, industry should partner with the government to further facilitate these processes. 

“If you look at our recommendations, there’s a premise here that it starts with putting in place some really good policies both in the executive branch and on the legislative side of the house,” said Dave Powner, executive director of MITRE’s Center for Data-Driven Policy and one of the authors of the recommendations. “So you can think of it as starting with OMB really requiring comprehensive modernization plans that focus on decommissioning some of these old systems and [then] that is backed with sound legislation. I think if you start with those policies in place from both sides—executive and legislative branches—that would be a good start to ensure that we’re all on the same page and marching to the same beat here.”

However, co-author Dr. Nitin Naik, a technical fellow at MITRE, noted that while policies and funding are necessary, there are other critical components to this process.

“You want to make sure that you have good implementation plans, and you need to have industry partnership because we don’t want the industry to continue to profess that the old technology can continue to meet the needs,” Naik said. “We want them to be an active participant to say, ‘Okay, let’s try to see how we can take this and bring it to the new industry standard.’”

Noting there have been several other efforts to modernize legacy systems—from previous bills to cyber budgets and the National Cybersecurity Strategy—Powner explained, “our recommendations really get at the execution of those plans.”

“And how do we execute those plans—having transparency mechanisms that you report progress, having industry as a key partner, thinking differently about the digital services team. And could agencies operate within their organizations, but also go to OMB or [a] central organization out of the White House for help?” Powner said. “And this is a collective game here—it’s the policymakers, the agencies and industry, all kind of collectively working together.”

For example, one recommendation suggests that agencies partner with industry, labs and federally-funded research and development centers to help with innovation and take advantage of new technologies, according to Naik.

Another recommendation for agencies focuses on using technology like artificial intelligence and automation to improve the modernization process.  

And while many agencies have modernization plans in place, there can be several challenges.

“The question is, are [agencies’] IT modernization plans really getting at these mission critical legacy applications?” Powner said. 

“All the systems we are talking about are delivering services 24/7, 365, so, you cannot have a stoppage of work in any way that will bring tremendous problems,” Naik said. “The question is—what is a good strategy to sort of start reengineering this, testing it out on the side, and then slowly one-by-one, migrating things over while it is an interconnected system.”

Article link; https://www.nextgov.com/it-modernization/2023/03/mitre-recommends-comprehensive-approach-modernize-legacy-systems/384675/

FDA will refuse new medical devices for cybersecurity reasons on Oct. 1 – SC MEDIA

Posted by timmreardon on 04/02/2023
Posted in: Uncategorized.

Jessica Davis March 28, 2023

The Food and Drug Administration announced March 29 that it will begin to “refuse to accept” medical devices and related systems over cybersecurity reasons beginning Oct. 1. All new device submissions must include detailed cybersecurity plans beginning March 29.

As such, device manufacturers will need to submit plans to monitor, identify and address in a “reasonable timeframe” any determined post-market cybersecurity vulnerabilities and exploits, including coordinated vulnerability disclosures and plans.

Developers must now design and maintain procedures able to show, with reasonable assurance, “that the device and related systems are cybersecure” and create post-market updates and patches to the device and connected systems that address “on a reasonably justified regular cycle, known unacceptable vulnerabilities,” according to the guidance.

If discovered out-of-cycle, the manufacturer must also make public “critical vulnerabilities that could cause uncontrolled risks,” as soon as possible.

Submissions will also need to include a software bill of materials, which must contain all commercial, open-source, and off-the-shelf software components, while complying with other FDA requirements “to demonstrate reasonable assurance that the device and related systems are cybersecure.”

These plans should come as no surprise to device manufacturers, as they were included in the new authorities granted by the Consolidated Appropriations Act of 2023, which was signed into law on Dec. 29.

The law created “long desired FDA authorities” that were left out of previous resolutions and includes requirements for premarket submissions proposed by the Protecting and Transforming Cyber Health Care (PATCH) Act.

The December inclusion yielded overwhelming support from healthcare stakeholders, who’ve long requested federal support to curtail systemic challenges with securing medical devices. Healthcare delivery organizations have long borne the onus of securing the vast, complex device ecosystem, and even the most equipped health systems do not fully meet the task.

The December Omnibus included statements that required the FDA to take the actions announced March 29 within 90 days of the law’s passage. The final guidance titled “Cybersecurity in Medical Devices: Refuse to Accept Policy for Cyber Devices and Related Systems,” includes all requirements for new submissions.

The new cybersecurity requirements don’t apply to applications or submissions submitted to the FDA before March 29. And the “refuse to accept” decisions for premarket submissions based solely on cyber reasons will not go into effect until Oct. 1.

Rather, the FDA says it intends to “work collaboratively with sponsors of such premarket submissions as part of the interactive and/or deficiency review process.” The agency expects that cyber device sponsors “will have had sufficient time to prepare premarket submissions” to include the cyber requirements contained in the finalized guidance.

“And FDA may refuse to accept premarket submissions that do not,” according to its notice. A a medical device is considered a “cyber device” if it includes “software validated, installed, or authorized by the sponsor,” can connect to the internet, and contains any tech characteristics validated, installed, or authorized that could be vulnerable to cybersecurity threats.

The guidance did not go through the typical public comment period, as “prior public participation is not feasible or appropriate.” Officials added that “although this policy is being implemented immediately without prior comment, FDA will consider all comments received and revise the guidance document as appropriate.”


Jessica Davis

The voice of healthcare cybersecurity and policy for SC Media, CyberRisk Alliance, driving industry-specific coverage of what matters most to healthcare and continuing to build relationships with industry stakeholders.

Article link: https://www.scmagazine.com/news/device-security/fda-will-refuse-new-medical-devices-for-cybersecurity-reasons-on-oct-1

Researchers achieve the first silicon integrated ECRAM for a practical AI accelerator – TechXplore

Posted by timmreardon on 04/02/2023
Posted in: Uncategorized.

by Michael O’Boyle , University of Illinois Grainger College of Engineering

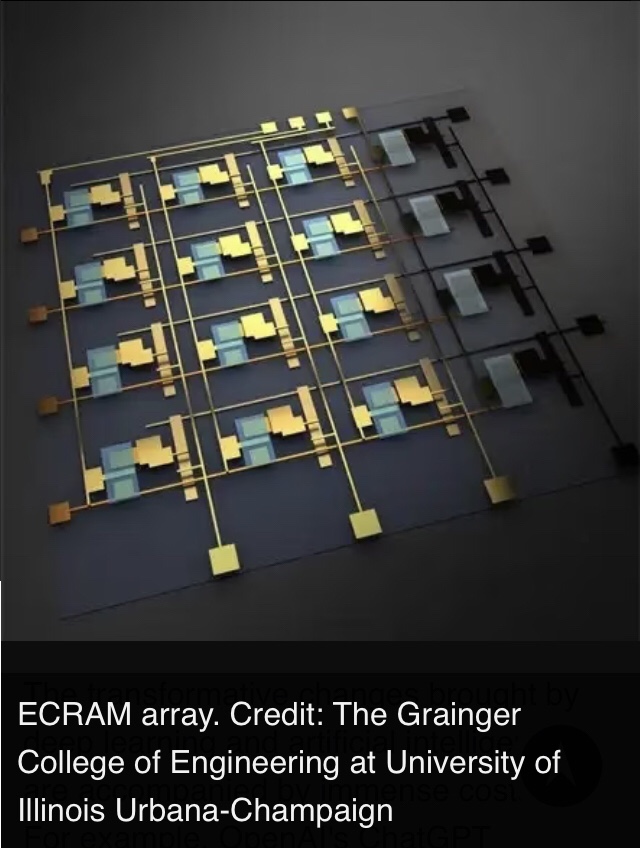
The transformative changes brought by deep learning and artificial intelligence are accompanied by immense costs. For example, OpenAI’s ChatGPT algorithm costs at least $100,000 every day to operate. This could be reduced with accelerators, or computer hardware designed to efficiently perform the specific operations of deep learning. However, such a device is only viable if it can be integrated with mainstream silicon-based computing hardware on the material level.

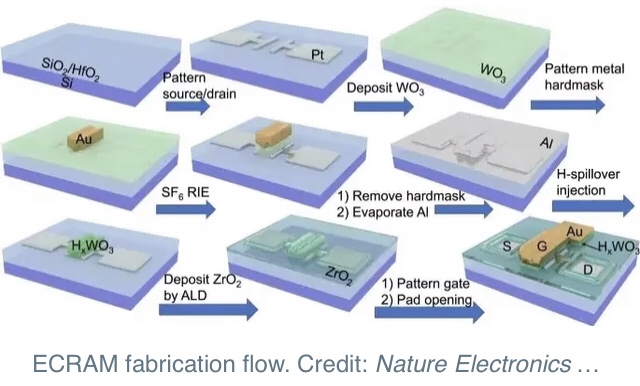
This was preventing the implementation of one highly promising deep learningaccelerator—arrays of electrochemical random-access memory, or ECRAM—until a research team at the University of Illinois Urbana-Champaign achieved the first material-level integration of ECRAMs onto silicon transistors. The researchers, led by graduate student Jinsong Cui and professor Qing Cao of the Department of Materials Science & Engineering, recently reported an ECRAM device designed and fabricated with materials that can be deposited directly onto silicon during fabrication in Nature Electronics, realizing the first practical ECRAM-based deep learning accelerator.

“Other ECRAM devices have been made with the many difficult-to-obtain properties needed for deep learning accelerators, but ours is the first to achieve all these properties and be integrated with silicon without compatibility issues,” Cao said. “This was the last major barrier to the technology’s widespread use.”

ECRAM is a memory cell, or a device that stores data and uses it for calculations in the same physical location. This non-standard computing architecture eliminates the energy cost of shuttling data between the memory and the processor, allowing data-intensive operations to be performed very efficiently.

ECRAM encodes information by shuffling mobile ions between a gate and a channel. Electrical pulses applied to a gate terminal either inject ions into or draw ions from a channel, and the resulting change in the channel’s electrical conductivity stores information. It is then read by measuring the electric current that flows across the channel. An electrolyte between the gate and the channel prevents unwanted ion flow, allowing ECRAM to retain data as a non-volatile memory.

The research team selected materials compatible with silicon microfabrication techniques: tungsten oxide for the gate and channel, zirconium oxide for the electrolyte, and protons as the mobile ions. This allowed the devices to be integrated onto and controlled by standard microelectronics. Other ECRAM devices draw inspiration from neurological processes or even rechargeable battery technology and use organic substances or lithium ions, both of which are incompatible with silicon microfabrication.

In addition, the Cao group device has numerous other features that make it ideal for deep learning accelerators. “While silicon integration is critical, an ideal memory cell must achieve a whole slew of properties,” Cao said. “The materials we selected give rise to many other desirable features.”

Since the same material was used for the gate and channel terminals, injecting ions into and drawing ions from the channel are symmetric operations, simplifying the control scheme and significantly enhancing reliability. The channel reliably held ions for hours at time, which is sufficient for training most deep neural networks. Since the ions were protons, with the smallest ion, the devices switched quite rapidly. The researchers found that their devices lasted for over 100 million read-write cycles and were vastly more efficient than standard memory technology. Finally, since the materials are compatible with microfabrication techniques, the devices could be shrunk to the micro- and nanoscales, allowing for high density and computing power.

The researchers demonstrated their device by fabricating arrays of ECRAMs on silicon microchips to perform matrix-vector multiplication, a mathematical operation crucial to deep learning. Matrix entries (neural network weights) were stored in the ECRAMs, and the array performed the multiplication on the vector inputs, represented as applied voltages, by using the stored weights to change the resulting currents. This operation as well as the weight update was performed with a high level of parallelism.

“Our ECRAM devices will be most useful for AI edge-computing applications sensitive to chip size and energy consumption,” Cao said. “That’s where this type of device has the most significant benefits compared to what is possible with silicon-based accelerators.”

The researchers are patenting the new device, and they are working with semiconductor industry partners to bring this new technology to market. According to Cao, a prime application of this technology is in autonomous vehicles, which must rapidly learn their surrounding environment and make decisions with limited computational resources. Cao is collaborating with Illinois electrical & computer engineering faculty to integrate their ECRAMs with foundry-fabricated silicon chips and Illinois computer science faculty to develop software and algorithms taking advantage of ECRAM’s unique capabilities.

More information: Jinsong Cui et al, CMOS-compatible electrochemical synaptic transistor arrays for deep learning accelerators, Nature Electronics (2023). DOI: 10.1038/s41928-023-00939-7

Journal information: Nature Electronics

Article link: https://techxplore-com.cdn.ampproject.org/c/s/techxplore.com/news/2023-03-silicon-ecram-ai.amp

What is agile? – McKinsey

Posted by timmreardon on 03/31/2023
Posted in: Uncategorized.

March 27, 2023 | Article

Agile is a way of working that seeks to harness the inevitability of change rather than resist it.

DOWNLOADS

Article (8 pages)

Quick on your feet: think for a minute of your favorite athlete. Unless this person is a bodybuilder, strength and sheer power are only part of the story. For most sportsmen and women, real success on the playing field comes with a certain hard-to-teach nimbleness—the ability to quickly take in new information and adjust strategy to achieve a specific result. Part of the appeal of sports is the excitement that comes with constant change, and—discounting the vicissitudes of luck—the result comes down to how athletes apply their abilities in response.

Change is also a constant in business (and, yes, life). Agile, in business, is a way of working that seeks to go with the flow of inevitable change rather than work against it. The Agile Manifesto, developed in 2001 as a way of optimizing software development, prioritizes individuals over processes, working prototypes over thorough documentation, customer collaboration over closed-door meetings, and swift response to change over following a set plan. In the years since its inception, agile has conferred competitive advantage to the organizations that have applied it, in and out of the IT department.

As our business, social, economic, and political environments become increasingly volatile, the only way to meet the challenges of rapidly changing times is to change with them. Read on to learn more about agile and how to adopt an agile mindset.

Learn more about McKinsey’s People & Organizational Performance Practice.

What is an agile organization?

Let’s go back to sports for a minute. Maybe you’re a great free throw shooter in basketball. You make nine out of ten shots when you’re by yourself in your driveway, shooting around for fun. But when you meet friends for a pickup game at a nearby court, your shot is off. People keep jumping in front of you when you’re trying to line up, and maybe the sun is shining in your eyes from an unfavorable angle. You make maybe a couple of shots the whole game. The following week, disappointed by your performance on the court, you decide to make a change. Rather than doubling your practice time shooting in your driveway, you mix up your routine, practicing your shot at a couple of different courts at different times of day. Maybe you also ask a friend to run some defense drills with you so you can get used to shooting under pressure. Maybe you add a layup to your shot practice. This is a shift to an agile approach—and increases the likelihood that you’ll perform better the next time you play pickup.

Traditional organizations are—much like you shooting free throws in your driveway—optimized to operate in static, siloed situations of structural hierarchy. Planning is linear, and execution is controlled. The organization’s skeletal structure is strong but frequently rigid and slow moving.

Agile organizations are different. They’re designed for rapid change. An agile organization is a technology-enabled network of teams with a people-centered culture that operates in rapid-learning and fast-decision cycles. Agility adds speed and adaptability to stability, creating a competitive advantage in uncertain conditions.

What is kanban and what is scrum?

Kanban and scrum are two organizational frameworks that fall under the umbrella of agile.

Kanban originated in the manufacturing plants of postwar Japan. Kanban, which is Japanese for “signboard,” was first developed to prioritize “just in time” delivery—that is, meeting demand rather than creating a surplus of products before they’re needed. With kanban, project managers create lanes of work that are required to deliver a product. A basic kanban board would have vertical lanes for processes—these processes could be “to do,” “doing,” “done,” and “deployed.” A product or assignment would move horizontally through the board.

The idea of scrum was invented by two of the original developers of agile methodology. A team of five to nine people is led by a scrum leader and product owner. The team sets its own commitments and engages in ceremonies like daily stand-up meetings and sprint planning, uniting in a shared goal.

Scrums, kanban, and other agile product management frameworks are not set in stone. They’re designed to be adapted and adjusted to fit the requirements of the project. One critical component of agile is the kaizenphilosophy—a pillar of the Toyota production model—which is one of continuous improvement. With agile methodologies, the point is to learn from each iteration and adjust the process based on what’s learned.

Learn more about McKinsey’s People & Organizational Performance Practice.

What are the hallmarks of an agile organization?

A team or organization of any size or industry can be agile. But regardless of the details, all agile groups have five things in common.

  1. North Star embodied across the organizationAgile organizations set a shared purpose and vision for the organization that helps people feel personally invested—that’s a North Star. This helps align teams with sometimes wildly varied remits and processes.
  2. Network of empowered teamsAgile organizations typically replace top-down structures with flexible, scalable networks of teams. Agile networks should operate with high standards of alignment, accountability, expertise, transparency, and collaboration. Regardless of the configuration of the network, team members should feel a sense of ownership over their work and see a clear connection between their work and the business’s North Star.
  3. Rapid decision and learning cyclesAgile teams work in short cycles—or sprints—then learn from them by collecting feedback from users to apply to a future sprint. This quick-cycle model accelerates the pace throughout the organization, prioritizing quarterly cycles and dynamic management systems—such as objectives and key results (OKRs)—over annual planning.
  4. Dynamic people model that ignites passionAn agile culture puts people at the center, seeking to create value for a much wider range of stakeholders, including employees, investors, partners, and communities. Making change personally meaningful for employees can build transformational momentum.
  5. Next-generation enabling technologyRadical rethinking of an organizational model requires a fresh look at the technologies that enable processes. These include, for example, real-time communication and work management tools that support continually evolving operating processes.

Agility looks a little different for every organization. But the advantages in stability and dynamism that the above trademarks confer are the same—and are critical to succeeding in today’s rapidly changing competitive environment.

How should an organization implement an agile transformation?

According to a McKinsey survey on agile transformations, the best way to go about an agile transformation is for an entire organization to transition to agile, rather than just individual departments or teams. This is ambitious but possible: New Zealand–based digital-services and telecommunications company Spark NZ managed to flip the entire organization to an agile operating model in less than a year.

Any enterprise-wide agile transformation needs to be both comprehensive and iterative: comprehensive in the sense that it addresses strategy, structure, people, process, and technology and iterative in its acceptance that things will change along the way.

Transformations vary according to the size, industry, and scope of the business, but there are a common set of elements that can be divided into two components.

  1. The first phase of an agile transformation involves designing and piloting the new agile operating model. This usually starts with building the top team’s understanding and aspirations, creating a blueprint for how agile will add value, and implementing pilots.
  2. The second phase is about improving the process and creating more agile cells throughout the organization. Here, a significant amount of time is required from key leaders, as well as willingness to role model new mindsets. The best way to accomplish this phase is to recognize that not everything can be planned for, and implementation requires continuous measurement and adjustment.

Culture is a critical part of any agile transformation. Agile is a mindset; it’s not something an organization does—it’s something an organization is. Getting this transition right is key to overall success.

Learn more about McKinsey’s People & Organizational Performance Practice.

Agile is a mindset; it’s not something an organization does—it’s something an organization is.

Who should lead an agile transformation?

The single most important trait for the leader of an agile organization is an agile mindset, or inner agility. Simply put, inner agility is a comfortable relationship with change and uncertainty. And research has shown that a leader’s mindset, and how that mindset shapes organizational culture, can make or break a successful agile transformation.

Leaders need three sets of capabilities for agile transformations:

  • Leaders must evolve new mindsets and behaviors.For most of us, the natural impulse is to react. Research shows that people spend most of their time in a reactive mindset—reacting to challenges, circumstances, or other people. Because of this natural tendency, traditional organizations were designed to run on the reactive.Agile organizations, by contrast, run on creative mindsets built on curiosity. A culture of innovation, collaboration, and value creation helps nurture the ability to flexibly respond to unexpected change. Creative mindsets also help members of an organization, at all levels, tap into their core passions and purposes.Roche, a legacy biotech company, recognized the importance of a mindset shift at the leadership level. When the organization decided to build an agile culture, it invited more than 1,000 leaders to a four-day immersion program designed to enable leaders to shift from a reactive mindset to a creative one. Today, agility has been widely deployed within Roche, engaging tens of thousands of people in applying agile mindsets.
  • Leaders must help teams work in new and more effective ways.Agility spells change for both leaders and their teams. Leaders need to give more autonomy and flexibility to their teams and trust them to do the right thing. For their part, teams should embrace a design-thinking mentality and build toward working more efficiently, assuming more responsibility for the outcomes of their projects and being more accountable to customers.
  • Leaders must cocreate an agile organizational purpose, design, and culture.A critical organization-level skill for leaders is the ability to distill and communicate a clear, shared, and compelling purpose, or North Star. Next, leaders need to design the strategy and operating model of the organization based on agile principles and practices. Finally, leaders need to shape a new culture across the organization, based on creative mindsets of discovery, partnership, and abundance.

For tips on how to develop agile leaders, see “Leading agile transformation: The new capabilities leaders need to build 21st-century organizations.”

How can we build inner agility?

Inner agility can feel counterintuitive. Our impulse as humans is to simplify and solve problems by applying our expertise. But complex problems require complex solutions, and sometimes those solutions are beyond our expertise. Recognizing that our solutions aren’t working can feel like failure—but it doesn’t have to. To train themselves to address problems in a more agile way, leaders need to learn to think beyond their normal ways of solving problems.

Here are five ways to build inner agility:

  1. Pause to move fasterThis can be tough for leaders used to moving quickly. But pausing in the middle of the fray can create space for clearer judgment, original thinking, and purposeful action. This can take many forms: one CEO McKinsey has worked with takes a ten-minute walk outside the office without his cell phone. Others do breathing exercises between meetings. These practices can help leaders interrupt habits to create space for something different.
  2. Embrace your ignoranceBeing a know-it-all no longer works. The world is changing so fast that new ideas can come from anywhere. Competitors you’ve never heard of can suddenly reshape your industry. As change accelerates, listening and thinking from a place of not knowing is crucial to encouraging the discovery of original, surprising, breakthrough ideas.
  3. Radically reframe the questionsWe too frequently interrogate our ideas, asking ourselves questions we already know the answers to—and worse, questions whose answers confirm what we already believe. Instead, seek to ask truly challenging, open-ended questions. Those types of questions allow your employees and stakeholders to creatively discuss and describe what they’re seeing, and potentially unblock existing mental frameworks.
  4. Set direction, not destinationIn the increasing complexity of our era, solutions are rarely straightforward. Instead of setting a path from one point to another, share a purposeful vision with your team. Then join your team in heading toward a general goal, and in exploring and experimenting together to reach common goals.
  5. Test your solutions—and yourselfIdeas may not work out as planned. But quick, cheap failures allow you to see what works and what doesn’t—and avoid major, costly disasters.

In times of stress, we often feel ourselves challenged. Rather than falling back on old habits, inner agility enables us to embrace complexity and use it to grow stronger.

Learn more about McKinsey’s People & Organizational Performance Practice.

What is deliberate calm?

Deliberate calm is a mindset that helps leaders keep a cool head during a crisis and steer their ships through a storm. It’s not something that comes naturally: in times of uncertainty, the human brain is wired to react rather than stay calm. The ability to step back and choose actions suited to a given situation is a skill that must be cultivated. In their 2022 book Deliberate Calm, McKinsey veterans Jacqueline Brassey, Aaron De Smet, and Michiel Kruyt describe their personal self-mastery practices to offer lessons in effective leadership through crises.

One important lesson? Not all crises are created equal. Inspired by the thinking of Harvard Business School professor Herman “Dutch” Leonard, De Smet differentiates between routine emergencies and crises of uncertainty. Routine emergencies can be dealt with using past experiences and training. But crises of uncertainty are different. In these moments, where you don’t know how deep the rabbit hole goes, you can’t fall back on what you know. “If you are in an uncertain situation,” says De Smet, “the most important thing you can do is calm down. Take a breath. Take stock. ‘Is the thing I’m about to do the right thing to do?’ And in many cases, the answer is no. If you were in a truly uncertain environment, if you’re in new territory, the thing you would normally do might not be the right thing.”

For more from De Smet and his coauthors, check out their discussion on The McKinsey Podcast, their Author Talksinterview, or order Deliberate Calm.

What is an agile transformation office?

Establishing an agile transformation office (ATO) can help improve the odds that an agile transformation will be successful. Embedded within an existing organizational structure, an ATO shapes and manages the transformation, brings the organization along, and—crucially—helps it achieve lasting cultural change.

To set up an ATO for success, an organization has to make three design decisions:

  1. Agree on the ATO’s purpose and mandateAn ATO needs a purpose just as an agile organization needs a North Star. This step links an ATO specifically to the “why” of the transformation. An ATO’s mandate can include driving the transformation strategy, building capabilities, championing change, coaching senior leaders, managing interdependencies, and creating and refining best practices.
  2. Define the ATO’s place within the organizationWhile an ATO’s reporting lines will depend on the organization, usually the leader of successful ATOs reports to the CEO or one of the CEO’s direct reports. This ensures tight alignment and support from top leadership.
  3. Determine the ATO’s roles and responsibilitiesRegardless of an ATO’s size or mandate, the following core capabilities should be managed by a strong transformation leader:Execution leaders own the transformation road map, assessing and adjusting it on an ongoing basis.Methodology owners gather lessons from the transformation and refine and evolve agile practices and behaviors.Agile coaches guide teams through their transformations, helping to instill an agile culture and mindset.Change management and communications expertsmaintain lines of communication through periods of change.

As agile principles become the norm across industries, an ATO can help usher in an agile transformation regardless of the design choices an organization makes in setting it up.

Can remote teams practice agile?

Agile teams typically rely on the camaraderie, community, and trust made possible by co-location. The remote work necessitated by the COVID-19 crisis has put this idea—along with many other assumptions about work and office culture—to the test.

While the shift was sudden, talented agile teams working through the crisis proved that productivity can be maintained with the right technology in place. Here are some targeted actions agile leaders can take to recalibrate their processes and sustain an agile culture with remote teams.

  1. Revisit team normsTools to ease teams into remote work abound—these include virtual whiteboards, instant chat, and videoconferencing. But they still represent a change from the in-person tools agile teams usually rely on for ceremonies. Team members need to help one another quickly get up to speed on how best to shift to virtual. Teams also need to make extra effort to capture the collective view, a special challenge when working remotely.
  2. Cultivate bonding and moraleIn the absence of in-person bonding activities, like lunches or spontaneous coffees, team members can bond virtually, such as by showing each other around their homes on a video call, introducing pets or family members, or sharing music or other personal interests. Being social is important in the virtual space, as well as in person, to nurture team cohesion.
  3. Adapt coaching and developmentTeam leaders who normally do one-on-one coaching over coffee should transition as seamlessly as possible to remote coaching—coffee and all.
  4. Establish a single source of truthIn person, agile team processes are usually informal. Teams make decisions with everyone in the room, so there’s not usually much need to record these discussions. In the virtual space, however, people might be absent or distracted, so it’s important to document team discussions in a way that can be referenced later.
  5. Adjust to asynchronous collaborationMessaging boards and chats can be useful in coordinating agile teams working remotely. But they should be used carefully, as they can also lead to team members feeling isolated.
  6. Adapt a leadership approachWhen working with remote teams, leaders need to be deliberate in guiding team members and interacting with external customers and stakeholders. Simply put, they need to show—in tone and approach—that everyone is in this together.

Now that it seems likely that remote work is here to stay, it’s all the more important that teams reinforce productivity by purposefully working to sustain an agile culture.

How can public-sector organizations benefit from agile?

The pandemic era and its attendant sociopolitical and economic crises have placed new pressures on public-sector organizations. In these situations of urgency, agile can help public-sector organizations better serve citizens by being more responsive.

Compared with the private sector, where agile has had a clear impact on the overall health of organizations, the public sector doesn’t immediately seem to be a great candidate for agile methodology. Government processes are often slower moving than their private-sector counterparts, and agencies are frequently in competition for funding, which can discourage collaboration. Finally, public-sector organizations are usually hierarchical; agile methodology works best in flat organizational structures.

But according to McKinsey analysis and experience, agile tools can still have an impact on public-sector productivity. As with any agile transformation, the approach should be tailored to each specific department, team, and organization.

Government entities, for example, might focus on short-term, results-driven management styles. OKRs and quarterly business reviews (QBRs) are agile concepts that can transform planning and resource allocation for governments. Agencies, for their part, can benefit from increased collaboration and cross-pollination made possible by agile operating models.

For a more in-depth exploration of these topics, see McKinsey’s People & Organizational Performance Practice. Also check out agile-related job opportunitiesif you’re interested in working at McKinsey.

Articles referenced include:

  • “When things get rocky, practice deliberate calm,” November 10, 2022, Jacqueline Brassey and Aaron De Smet
  • “In pursuit of value—not work,” October 24, 2022, Elena Chong, Christopher Handscomb, Tomasz Maj, Rishi Markenday, Leslie Morse, and Dave West
  • “Why an agile transformation office is your ticket to real and lasting impact,” June 30, 2021, Amit Anand, Khushpreet Kaur, Noor Narula, and Belkis Vasquez-McCall
  • “The impact of agility: How to shape your organization to compete,” May 25, 2021, Wouter Aghina, Christopher Handscomb, Olli Salo, and Shail Thaker
  • “Doing vs being: Practical lessons on building an agile culture,” August 4, 2020, Nikola Jurisic, Michael Lurie, Philippine Risch, and Olli Salo
  • “All in: From recovery to agility at Spark New Zealand,” McKinsey Quarterly, June 11, 2019, Simon Moutter, Jolie Hodson, Joe McCollum, David Pralong, Jason Inacio, and Tom Fleming
  • “The journey to an agile organization,” May 10, 2019, Daniel Brosseau, Sherina Ebrahim, Christopher Handscomb, and Shail Thaker
  • “Leading agile transformation: The new capabilities leaders need to build 21st-century organizations,” October 1, 2018, Aaron De Smet, Michael Lurie, and Andrew St. George
  • “Agile with a capital ‘A’: A guide to the principles and pitfalls of agile development,” February 12, 2018, Hugo Sarrazin, Belkis Vasquez-McCall, and Simon London
  • “The five trademarks of agile organizations,” January 22, 2018, Wouter Aghina, Karin Ahlback, Aaron De Smet, Gerald Lackey, Michael Lurie, Monica Murarka, and Christopher Handscomb
  • “A business leader’s guide to agile,” July 25, 2017, Santiago Comella-Dorda, Krish Krishnakanthan, Jeff Maurone, and Gayatri Shenai
  • “ING’s agile transformation,” McKinsey Quarterly, January 10, 2017, Peter Jacobs, Bart Schlatmann, and Deepak Mahadevan

Article link:
https://www.mckinsey.com/featured-insights/mckinsey-explainers/what-is-agile?
Announcing the Thirteenth Annual USMC IT Day! – Cyber Bytes Foundation

Posted by timmreardon on 03/31/2023
Posted in: Uncategorized.

The AFCEA Quantico-Potomac chapter will be hosting their 13th Annual USMC IT Day on Thursday, May 11, 2023.

Leadership from DC I, MCSC, and IC4 is confirmed with an exciting lineup of speakers from PEO Digital, PEO MLB, NIWC Atlantic, DON CIO, OSD, and others!

This will be an in-person event with a luncheon, keynote speakers, panels, and a mixer.

This event will be held here at the Cyber Bytes Foundations, Quantico Cyber Hub, located at 1010 Corporate Dr., Stafford.

For more details on how to register, or if you are interested in a Sponsorship, please contact Jeremy Rockett.

Website: https://lnkd.in/ehGssZQk

Jeremy Rockett
Vice President, Sponsorships
703.489.9899
jeremy.rockett@govini.com

https://www.afcea-qp.org/usmc-it-day/usmc-it-day-2023/

#work #opportunities #share #networking #connections #like #event #events #engagement #cyber #cybertraining #quanticocyberhub #cyberbytesfoundation #cyberseminar #cybersecurity #cybersecurityawareness #cyberdefense #cybernews #cyberawareness #cybereducation #cybermixer #innovation #technology #technologytrends #technologysolutions #technologyjobs #networkingevent #networkingopportunities #networkingbusiness #digital

Dr. Paul de Souza | ♦️Amanda S. | Jonathan Payton | Joel Scharlat | Matthew Weaver | Kaleb Hunter | Katharine Reinboldt | Jeff Rose | Michael Schwartz and CHEVERLY | Donovan Applewhite | Luke Wright | Sam Hanson | Steve Karam | Brian McCarthy | Brian DeMuth | Vernon Hood Taylor | Fredericksburg Regional Chamber of Commerce

NIST Debuts Trustworthy and Responsible AI Resource Center – Nextgov

Posted by timmreardon on 03/31/2023
Posted in: Uncategorized.

By ALEXANDRA KELLEYMARCH 30, 2023 12:46 PM ET

The new resource builds upon NIST’s previously-issued framework and playbook, while offering a visual roadmap for the safe creation and risk management of AI systems.

The new Trustworthy & Responsible Artificial Intelligence Resource Center built by the National Institute of Standards and Technology will now serve as a repository for much of the current federal guidance on AI, featuring easy access to previously issued materials to help public and private entities alike create responsible AI systems.

Formally launched on Thursday, the new AI Resource Center builds upon NIST’s AI Resource Management Framework and AI Playbook to support industry best practices in researching and developing socially responsible AI and machine learning systems absent overarching federal law.   

“The AIRC supports all AI actors in the development and deployment of trustworthy and responsible AI technologies,” the homepage reads.

Illustrated on the Resource Center homepage is a visualization of the AI Roadmap, containing several key pillars of the RMF, including U.S. alignment with international tech standards, expanding the Department of Defense’s Test and Evaluation, Verification and Validation efforts, using data to measure the RMF’s efficacy, enhancing RMF guidance and interpretability, expanded use cases, and more context on the human-AI component in risk management.

“The Roadmap identifies key activities for advancing the AI RMF that could be carried out by NIST in collaboration with private and public sector organizations—or by those organizations independently,” the homepage says. “Work described in the Roadmap is intended to help fill gaps in knowledge, practice or guidance and be useful to broader audience [sic] in pursuit of trustworthy and responsible AI.”

The homepage added that the Roadmap’s activities and plans stand to change as AI technologies evolve. NIST noted on the website that it expects “in the coming months” to add enhancements to the Resource Center to include new document links, access to an international standards hub, metrics resources for AI systems testing and software tools. 

In addition to quick access to the RMF and Playbook, NIST’s AI resource website offers a formal glossary of definitions to further establish a fundamental vernacular integral to the AI industry. A section spotlighting new events, such as training workshops and visiting fellows research, related to NIST’s AI agenda, is also featured on the site.

Article link: https://www.nextgov.com/emerging-tech/2023/03/nist-debuts-trustworthy-and-responsible-ai-resource-center/384618/

Streamlining the Joint Capabilities Integration and Development System (JCIDS) Processes – Acquisition Innovation Research Center

Posted by timmreardon on 03/31/2023
Posted in: Uncategorized.

In support of the Department of Defense(DoD) response to Congressional concerns regarding delays in JCIDSprocesses, the Acquisition Innovation Research Center (AIRC) assessed how it can improve the efficiency of developing and approving capability requirements and develop a model to show the effects of proposed alternatives.  

In a presentation titled “Assessments of the Process for Developing Capability Requirements for DoD Acquisition Programs” on research into a validation process used by the DoD to identify, develop, and meet the needs and requirements of warfighters, AIRC modeled JCIDS processes and proposed improvements such as incorporating lean approaches to the requirements validation process, rapid prototyping, changes to policy, and training for a cadre of requirements professionals.  

Currently, it takes more than two years to identify capability gaps and choose a solution approach through JCIDS, leaving interoperability between military forces at risk and warfighters vulnerable to threats. 

“That is a problem,” said Dr. Donald Schlomer, Acquisition Program Manager SOF AT&L – Policy Manager, US Special Operations Command, who spent three years researching JCIDS processes for his doctoral dissertation, “How do you use current technology if it takes you two and a half years just to get a requirement validated to address and acquire a technology?” 

Schlomer worked alongside Dr. Mo Mansouri, Stevens Institute of Technology, and Dr. Michael McGrath, AIRC Fellow, to develop a problem-focused approach to remedy JCIDS delays and identify improvements. The three researchers presented their findings at the 2022 Annual Research Review, during which they described how they modeled the requirements process based on a sample of Navy programs, assessed the interface between services and joint staff, and identified automotive industry and foreign acquisition best practices to produce a trio of recommended improvements that can potentially streamline the requirements validation process.  

“The idea was to figure out what’s causing the delays in the process and see if we can patch that in the best way using all of the optimization methodologies that we had in mind and could apply,” said Mansouri. 

Their approach relied heavily on the simulation model based on Joseph Wirthlin’s research on acquisition at MIT. “It didn’t include software acquisition programs,” Mansouri said. “We updated it, but we worked on the same level because that was a good baseline for us.” Then, they applied Value Stream Mapping based on Hugh McManus’ handbook for product development, a process first used by Toyota. “We used the same principles and methodology to make the process linear,” Mansouri continued. “The qualitative methodology was mostly focused on interviews with other companies and entities that have a similar approach to requirement development.”  

The first recommended improvement focuses on lean approaches and doesn’t require any policy changes but has the potential to reduce end-to-end time by 25 percent. The second recommendation is more intensive and requires an overhaul of the entire JCIDS process to combine the Initial Capabilities Document and Capabilities Development Document into one integrated document that, according to Mansouri, would “reduce the time by 50 percent, from 852 days to 444 days.” The third approach aligns JCIDS with the Defense Acquisition System using the Adaptive Acquisition Framework and will require significant changes in the law, policies, and manuals. 

“What we discovered here is a capability gap in the JCIDS process itself,” said McGrath. “There’s no authoring system, but authoring a requirement is a challenging thing. You’ve got this handbook that’s 341 pages. You’ve got a policy directive that’s another 114 pages. And the only professionals who really understand that in-depth are the gatekeepers in joint staff and services. The last recommendation was one that we thought was needed. Just as there are acquisition professionals and budget process professionals, there needs to be a cadre of requirements professionals.”  

McGrath continued: “When you look at the agile acquisition framework, we heard that there’s a strong incentive for middle-tier acquisition work around the delays of the JCIDS process. Rapid prototyping and putting a prototype in the hands of a warfighter and then using that as the basis for defining the requirement for what you want to go to production offers a much faster path and one that can keep pace with technology.” 

As is the case with many exploratory research projects, there were constraints. Because of how the project was defined, the team had to look at this problem from the perspective of gatekeepers. “That was one caveat of this research: the level of abstraction was set for us,” said Mansouri. And the model relied on a limited data set. “That’s another restriction of this research. Obviously, they couldn’t give us a lot of these cases, and it has to be sanitized and categorized based on the type of program as well.” 

As further developments occur, success will hinge on embracing better end-to-end governance processes, streamlined documents and staffing, agile requirements, and missions and systems engineering solutions — indicating that digital transformation is integral to improving JCIDS processes. 

“Automating whatever we can is a principle of lean systems — an AI-assisted workflow management that enforces a schedule and is also useful in collecting data,” said Mansouri. “Digitalization is upon us, and that’s probably one of the most important things we should invest in.” 

View the recording from the third quarterly AIRC-DAU Research Forum to learn more about this ongoing research. Follow AIRC on LinkedIn for updates on acquisition innovation.

EXECUTIVE SUMMARY AND REPORT

Article link: https://acqirc.org/news/treamlining-the-joint-capabilities-integration-and-development-system-jcids-processes/

FDA requires medical devices be secured against cyberattacks CNN

Posted by timmreardon on 03/30/2023
Posted in: Uncategorized.

By Jennifer Korn

Published 3:56 PM EDT, Wed March 29, 2023

New YorkCNN — 

The Food and Drug Administration will now require medical devices meet specific cybersecurity guidelines after years of concerns that a growing number of internet-connected products used by hospitals and healthcare providers could be hit by hacks and ransomware attacks. 

Under FDA guidance issued this week, all new medical device applicants must now submit a plan on how to “monitor, identify, and address” cybersecurity issues, as well as create a process that provides “reasonable assurance” that the device in question is protected. Applicants will also need to make security updates and patches available on a regular schedule and in critical situations, and provide the FDA with “a software bill of materials,” including any open-source or other software their devices use.

The new security requirements came into effect as part of the sweeping $1.7 trillion federal omnibus spending bill signed by President Joe Biden in December. As part of the new law, the FDA must also update its medical device cybersecurity guidance at least every two years. 

A 2022 report released by the FBI cited research finding 53% of digital medical devices and other internet-connected products in hospitals had known critical vulnerabilities. The report listed a number of medical devices that are susceptible to cyber attacks, including insulin pumps, intracardiac defibrillators, mobile cardiac telemetry and pacemakers. 

“Malign actors who compromise these devices can direct them to give inaccurate readings, administer drug overdoses, or otherwise endanger patient health,” according to the FBI report.

In 2021, a group of researchersinvestigating software used in medical devices and machinery used in other industries found over a dozen vulnerabilities that, if exploited by a hacker, could cause critical equipment such as patient monitors to crash.

The FDA has faced criticisms over the years for not doing enough. 

A 2018 report from the US Department of Health and Human Services’ Office of the Inspector General said the FDA was not adequately protecting devices from getting hacked.

“FDA had plans and processes for addressing certain medical device problems in the postmarket phase, but its plans and processes were deficient for addressing medical device cybersecurity compromises,” the report said. 

CNN’s John D. Sutter contributed to this report.

Article link: https://www.cnn.com/2023/03/29/tech/fda-medical-devices-secured-cyberattacks/index.html

How fear of future quantum hacks could expose sensitive data now – Bulletin of the Atomic Scientists

Posted by timmreardon on 03/30/2023
Posted in: Uncategorized.

By Nicolas Ayala Arboleda | March 30, 2023

Quantum computers that can crack standard encryption algorithms may arrive in a few years, a few decades, or maybe never. However, they are already having a significant impact. A new cryptographic arms race is developing around quantum computers, in a dynamic that threatens much of the modern world’s digital infrastructure.

Governments and big tech companies are frantically searching for ways to apply and counter the power of this technology. Most notably, they are developing encryption schemes that would be resistant to cyberattacks from quantum computers, also known as post-quantum encryption schemes. The challenge: Quantum-resistant algorithms can be vulnerable to conventional hacking.

Last summer, a classical computer that is not even capable of running Windows 11 broke a quantum-resistant encryption algorithm in less than an hour. For comparison, classical computers require hundreds of trillions of years to break the public key encryption schemes that are standard in everything from banking to security systems. The cracked algorithm, Microsoft’s SIKE (Supersingular Isogeny Key Encapsulation), was one of the US government’s late-stage candidates for modernizing current cryptography standards and preventing potential adversaries with quantum computers from unveiling highly sensitive data.

There is a real danger that, by attempting to address the risk of quantum hacking, security architectures might be opening another more devastating and immediate vulnerability. Had SIKE been prematurely deployed on critical systems, and its weakness been discovered by an adversary, the economic and security consequences would have been terrible.

However, continuing to rely on potentially outdated conventional encryption may be equally dangerous. If quantum computers were to break public key encryption, there would be significant consequences for the economy, privacy, and security. For example, hackers could use this capability to compromise US national security systems. This would potentially expose classified information, including intelligence and military data. Moreover, financial transactions, emails, digital signatures, and other confidential information could be decrypted.

A lack of understanding of quantum technologies in policy circles, international tensions, and infrastructural challenges further complicate the dilemma and increase the risk of miscalculations.

The race to post-quantum. Most current public key encryption relies on mathematical operations that are easy to solve but difficult to reverse. For example, it is easy to multiply two large prime numbers. However, finding these exact numbers by factorizing their product is extremely time-consuming for a classical computer.

Quantum computers could approach factorization by either turning it into an optimization problem or by applying a method called Shor’s algorithm. Shor’s is one of the few currently known algorithms that could allow quantum computers to perform dramatically better than conventional computers. This improved capability could crack the most popular types of public key encryption exponentially fasterthan classical computers.

The systems theoretically capable of these feats are known as “cryptographically significant” quantum computers, and they are likely decades away from existing. Initially, only powerful governments and big tech companies are expected to have access to these systems, because of their enormous cost and complexity.

These quantum computers would threaten encrypted messages sent before and after their invention. Countries are currently intercepting and storing data with the hope of decrypting it later, if these countries manage to develop a capable quantum computer. This method is known as “harvest now, decrypt later.” Some expertsestimate that every message sent today is being collected by at least two countries or private organizations. However, the real extent of this practice is unknown.

The US National Institute of Standards and Technology is attempting to improve public key encryption by establishing a new post-quantum cryptographic standard. The new algorithms that the institute is compiling do not require quantum computers for their development. However, the schemes have taken considerable time to engineer. After a six-year competition, the organizers selected four initial winners and short-listed four additional algorithms as finalists for possible future implementation. SIKE was among the latter group.

Will DIANA—NATO’s DARPA-style innovation hub—improve or degrade global stability?

After announcing the results, the institute encouraged the cryptography community to try to break the new algorithms. This vetting process brought in outside perspectives, in an attempt to identify issues that insiders might have overlooked. Only a month after the announcement, cryptographers from the research university KU Leuven were able to break SIKE’s encryption. Their research showed that a single-core computer, which applies mathematics developed in the 1990s and 2000s, can decrypt the algorithm in about an hour.

This type of hack is partial proof that the vetting process is working. If members of the public find vulnerabilities and communicate them to standard-setters, the standards institute can prevent malicious actors from exploiting these flaws at a later stage. In SIKE’s case, Microsoft encouraged hackers in the general public to share their findings by offering a $50,000 bounty. The reward system was successful in this instance. However, it is unclear whether money will always be enough to prevent hackers from trying to sell their findings to higher bidders.

There might be other reasons to worry. Jonathan Katz, a professor of computer science at the University of Maryland and core faculty member in the Maryland Cybersecurity Center, told Ars Technica: “It is perhaps a bit concerning that this is the second example in the past six months of a scheme that made it to the 3rd round of the [National Institute of Standards and Technology] review process before being completely broken using a classical algorithm.”

The other algorithm Katz refers to is Rainbow, which researchers cracked earlier in the year. Katz goes on to advise caution, noting that three of the four winners of the institute’s process “rely on relatively new assumptions whose exact difficulty is not well understood.”

Additionally, vetters do not currently have a cryptographically significant quantum computer to deploy against these new encryption schemes. Therefore, standard-setters are limited to running purely theory-based testing. Until post-quantum schemes undergo practical tests, there will be questions surrounding the algorithms’ reliability.

The dangers of fear. Quantum technologies have gained an aura of extreme complexity and occasional urgency. Periodically, a flurry of headlines on the imminent impact of quantum technologies rouses policy makers and industry members who do not understand how the technology works. This combination of alleged inexplicability and urgency is counterproductive, even dangerous.

Q-Day is a clear example. Q-Day is a narrative claiming that a large quantum computer will one day be able to suddenly crack existing public key encryption systems. In this scenario, the quantum computer would almost immediately decrypt crucial elements of international security and finance. Catastrophic consequences for defense would follow, along with monetary losses and a collapse of trust in the international financial and security architectures. It is a grim picture.

While Q-Day does identify a few genuine potential risks, some of its assumptions are contestable. Chief among them is viewing the advent of cryptographically significant quantum computers as a question of “when” and not “if.” Experts and institutions have argued that there is no guarantee cryptographically significant quantum computers will ever be a reality.

Additionally, Q-Day’s apocalyptic scenario assumes that quantum computers will develop explosively, almost overnight. Considering the numerous significant technical challenges that remain, it is unlikely that quantum computers will improve at this pace, although it is difficult to predict when or if breakthroughs will happen.

Finally, the Q-Day narrative treats certain important hurdles for conducting quantum hacking as trivial. For example, it ignores that hackers bent on decrypting data would require access to encrypted files and time on a quantum computer, which would be a precious finite resource.

Unchecked, these assumptions could lead policy makers to rush standard-setting processes, producing vulnerabilities in cryptography schemes. Policy makers can prevent this by refusing to see quantum technology as an impenetrable domain, and instead making an effort to better understand it. Free resources published by nations, companies, and science communicators can help the “quantum curious” learn about this new technology.

International competition is also putting pressure on the United States, European Union, China, and other nations to develop quantum-resistant cryptography. Every so often, one of these competitors claims to be on the cusp of breaking public key encryption. The latest episode featured a group of Chinese researchers claiming that they had engineered a new quantum decryption algorithm. This method would allegedly work on significantly smaller quantum computers than initially thought necessary for efficient cryptanalysis. However, as is often the case in this field, the results were not as significant as initially thought.

Given the highly sensitive nature of technologies used for quantum cryptography, it is very difficult to assess the true progress being made. International tensions and imperfect information allow fears of strategic surprise to fester. A strategic surprise is an unexpected change that challenges current strategic assumptions. In this case, the development would be societies losing an essential, secure channel of communications. A government could develop and use a cryptographically significant quantum computer without the knowledge of others, leaving competitors guessing whether they are being hacked or not.

Mitigating the risk of strategic surprise will require careful development and implementation of robust post-quantum encryption. The issue has recently gained more political attention in the United States, with the Senateand the Biden administrationtaking action. The latter instructed federal agencies to begin preparing for the transition to post-quantum encryption. However, a wider migration will require software and hardware changes to an extensive set of devices, likely taking at least a decade and costing billions of dollars. This level of effort and time horizon will require consistent action.

There is a long road ahead before societies can achieve a reliable post-quantum public key encryption system. However, companies and governments can currently implement security measures to better protect data and support the transition to quantum-resistant encryption. These measures range from less technical, such as risk assessments, to highly complex, such as implementing quantum key distribution. Data managers can also set up honeypots(encrypted but useless data) to mislead attackers, and compartmentalize their data and encrypt each part separately.

Beyond these technical solutions, governments and industry can educate themselves to avoid falling prey to hype. Governments could partly ease international tensions by holding—or at least not preventing—dialogues between scientists, engineers, and policy makers to better communicate and understand threat perceptions. These discussions could help avoid unwanted confrontations.

Moreover, discussing quantum hacking in policy and military doctrines could help clarify its use. However, it would be difficult for outsiders to verify whether countries are following doctrines or international agreements that may limit the use of quantum computers.

Ideally, governments and industry should mitigate the technical and political risks of quantum hacking, a capability that might never come to fruition—while also being careful not to provide everyone who has a moderately modern computer with the tools to hack government secrets.

Article link: https://thebulletin.org/2023/03/how-fear-of-future-quantum-hacks-could-expose-sensitive-data-now/

Technologists, Experts Call for Halt on Advanced AI Development Over ‘Risks to Society’ – Nextgov

Posted by timmreardon on 03/30/2023
Posted in: Uncategorized.

High-profile signees include Tesla and SpaceX chief Elon Musk and Apple co-founder Steve Wozniak.

More than 1,000 artificial intelligence experts, industry chiefs and technologists have signed an open letter calling for a six-month pause in developing more advanced artificial intelligence systems, citing “profound risks to society and humanity.”

The open letter, authored by the non-profit Future of Life Institute, comes as OpenAI launches the next iteration of its ChatGPT AI platform—ChatGPT-4—the successor to ChatGPT-3.5, which generated headlines for its ability to perform human-like activities, like writing reports and engaging in realistic conversation.

The technology has also caused controversy, from its potential to eliminate certain jobs to its ability to produce powerful disinformation in the hands of bad actors. The letter calls on AI labs to “immediately pause for at least 6 months the training of AI systems more powerful than ChatGPT-4.”

“Contemporary AI systems are now becoming human-competitive at general tasks, and we must ask ourselves: Should we let machines flood our information channels with propaganda and untruth?” the letter states.

“Should we automate away all the jobs, including the fulfilling ones? Should we develop nonhuman minds that might eventually outnumber, outsmart, obsolete and replace us? Should we risk loss of control of our civilization?” the letter continued. “Such decisions must not be delegated to unelected tech leaders. Powerful AI systems should be developed only once we are confident that their effects will be positive and their risks will be manageable.”

The letter has accumulated the signatures of numerous high-profile technologists, scientists and AI and policy experts. Among them: Elon Musk, chief executive officer at SpaceX, Tesla and Twitter; Steve Wozniak, co-founder of Apple; Max Tegmark, MIT Center for Artificial Intelligence & Fundamental Interactions and professor of physics; and Lawrence M. Krauss, president of The Origins Project Foundation.

The government is not yet a major consumer of ChatGPT-4-like AI systems, though officials at the Defense Department have promoted the potential benefits of using similar technologies in recent months. At the state and local levels of government, officialshave suggested these technologies could work in areas that don’t require human subjectivity, like transcribing and summarizing constituent calls. At the federal level, the National Institute of Standards and Technology recently released its Artificial Intelligence Risk Management Framework, which seeks to guide agencies and organizations toward developing “low-risk AI systems.”

However, NIST officials early this month stressed that creating responsible AI presents “major technical challenges” for technologists.

“When it comes [to] measuring technology, from the viewpoint of ‘Is it working for everybody?’ ‘Is AI systems benefiting all people in [an] equitable, responsible, fair way?’, there [are] major technical challenges,” Elham Tabassi, chief of staff at NIST’s Information Technology Laboratory, saidMarch 6 in a panel discussion.

“It’s important when this type of testing is being done, that the impact of community are identified so that the magnitude of the impact can also be measured,” she said. “It cannot be over emphasized, the importance of doing the right verification and validation before putting these types of products out. When they are out, they are out with all of their risks there.”

Article link: https://www.nextgov.com/emerging-tech/2023/03/technologists-experts-call-halt-advanced-ai-development-over-risks-society/384573/

Posts navigation

← Older Entries
Newer Entries →
  • Search site

  • Follow healthcarereimagined on WordPress.com
  • Recent Posts

    • By Barring Profits on Basic Coverage, Switzerland Keeps Insurers from Denying Care – Commonwealth Fund 10/19/2026
    • Patients’ Perspectives on AI in Primary Care – Commonwealth Fund 09/11/2026
    • Bitcoin Mining Energy Footprint 08/06/2026
    • Closing the AI Hype Gap 08/05/2026
    • Why Artificial Intelligence is Neither Artificial, Nor Intelligent 07/31/2026
    • Agentic AI, explained 07/05/2026
    • Heeding the pope’s call to ensure AI protects human dignity – MIT Sloan Management 06/01/2026
    • Association between Wealth and Mortality in the United States and Europe – New England Journal of Medicine 05/30/2026
    • U.S. Health Care from a Global Perspective, 2026 – The Commonwealth Fund 05/30/2026
    • Anthropic co-founder Chris Olah’s remarks on Pope Leo XIV’s encyclical “Magnifica humanitas” 05/28/2026
  • Categories

    • Accountable Care Organizations
    • ACOs
    • AHRQ
    • American Board of Internal Medicine
    • Big Data
    • Blue Button
    • Board Certification
    • Cancer Treatment
    • Data Science
    • Digital Services Playbook
    • DoD
    • EHR Interoperability
    • EHR Usability
    • Emergency Medicine
    • FDA
    • FDASIA
    • GAO Reports
    • Genetic Data
    • Genetic Research
    • Genomic Data
    • Global Standards
    • Health Care Costs
    • Health Care Economics
    • Health IT adoption
    • Health Outcomes
    • Healthcare Delivery
    • Healthcare Informatics
    • Healthcare Outcomes
    • Healthcare Security
    • Helathcare Delivery
    • HHS
    • HIPAA
    • ICD-10
    • Innovation
    • Integrated Electronic Health Records
    • IT Acquisition
    • JASONS
    • Lab Report Access
    • Military Health System Reform
    • Mobile Health
    • Mobile Healthcare
    • National Health IT System
    • NSF
    • ONC Reports to Congress
    • Oncology
    • Open Data
    • Patient Centered Medical Home
    • Patient Portals
    • PCMH
    • Precision Medicine
    • Primary Care
    • Public Health
    • Quadruple Aim
    • Quality Measures
    • Rehab Medicine
    • TechFAR Handbook
    • Triple Aim
    • U.S. Air Force Medicine
    • U.S. Army
    • U.S. Army Medicine
    • U.S. Navy Medicine
    • U.S. Surgeon General
    • Uncategorized
    • Value-based Care
    • Veterans Affairs
    • Warrior Transistion Units
    • XPRIZE
  • Archives

    • October 2026 (1)
    • September 2026 (1)
    • August 2026 (2)
    • July 2026 (2)
    • June 2026 (1)
    • May 2026 (12)
    • April 2026 (4)
    • March 2026 (9)
    • February 2026 (6)
    • January 2026 (8)
    • December 2025 (11)
    • November 2025 (9)
    • October 2025 (10)
    • September 2025 (4)
    • August 2025 (7)
    • July 2025 (2)
    • June 2025 (9)
    • May 2025 (4)
    • April 2025 (11)
    • March 2025 (11)
    • February 2025 (10)
    • January 2025 (12)
    • December 2024 (12)
    • November 2024 (7)
    • October 2024 (5)
    • September 2024 (9)
    • August 2024 (10)
    • July 2024 (13)
    • June 2024 (18)
    • May 2024 (10)
    • April 2024 (19)
    • March 2024 (35)
    • February 2024 (23)
    • January 2024 (16)
    • December 2023 (22)
    • November 2023 (38)
    • October 2023 (24)
    • September 2023 (24)
    • August 2023 (34)
    • July 2023 (33)
    • June 2023 (30)
    • May 2023 (35)
    • April 2023 (30)
    • March 2023 (30)
    • February 2023 (15)
    • January 2023 (17)
    • December 2022 (10)
    • November 2022 (7)
    • October 2022 (22)
    • September 2022 (16)
    • August 2022 (33)
    • July 2022 (28)
    • June 2022 (42)
    • May 2022 (53)
    • April 2022 (35)
    • March 2022 (37)
    • February 2022 (21)
    • January 2022 (28)
    • December 2021 (23)
    • November 2021 (12)
    • October 2021 (10)
    • September 2021 (4)
    • August 2021 (4)
    • July 2021 (4)
    • May 2021 (3)
    • April 2021 (1)
    • March 2021 (2)
    • February 2021 (1)
    • January 2021 (4)
    • December 2020 (7)
    • November 2020 (2)
    • October 2020 (4)
    • September 2020 (7)
    • August 2020 (11)
    • July 2020 (3)
    • June 2020 (5)
    • April 2020 (3)
    • March 2020 (1)
    • February 2020 (1)
    • January 2020 (2)
    • December 2019 (2)
    • November 2019 (1)
    • September 2019 (4)
    • August 2019 (3)
    • July 2019 (5)
    • June 2019 (10)
    • May 2019 (8)
    • April 2019 (6)
    • March 2019 (7)
    • February 2019 (17)
    • January 2019 (14)
    • December 2018 (10)
    • November 2018 (20)
    • October 2018 (14)
    • September 2018 (27)
    • August 2018 (19)
    • July 2018 (16)
    • June 2018 (18)
    • May 2018 (28)
    • April 2018 (3)
    • March 2018 (11)
    • February 2018 (5)
    • January 2018 (10)
    • December 2017 (20)
    • November 2017 (30)
    • October 2017 (33)
    • September 2017 (11)
    • August 2017 (13)
    • July 2017 (9)
    • June 2017 (8)
    • May 2017 (9)
    • April 2017 (4)
    • March 2017 (12)
    • December 2016 (3)
    • September 2016 (4)
    • August 2016 (1)
    • July 2016 (7)
    • June 2016 (7)
    • April 2016 (4)
    • March 2016 (7)
    • February 2016 (1)
    • January 2016 (3)
    • November 2015 (3)
    • October 2015 (2)
    • September 2015 (9)
    • August 2015 (6)
    • June 2015 (5)
    • May 2015 (6)
    • April 2015 (3)
    • March 2015 (16)
    • February 2015 (10)
    • January 2015 (16)
    • December 2014 (9)
    • November 2014 (7)
    • October 2014 (21)
    • September 2014 (8)
    • August 2014 (9)
    • July 2014 (7)
    • June 2014 (5)
    • May 2014 (8)
    • April 2014 (19)
    • March 2014 (8)
    • February 2014 (9)
    • January 2014 (31)
    • December 2013 (23)
    • November 2013 (48)
    • October 2013 (25)
  • Tags

    Business Defense Department Department of Veterans Affairs EHealth EHR Electronic health record Food and Drug Administration Health Health informatics Health Information Exchange Health information technology Health system HIE Hospital IBM Mayo Clinic Medicare Medicine Military Health System Patient Patient portal Patient Protection and Affordable Care Act United States United States Department of Defense United States Department of Veterans Affairs
  • Upcoming Events

Blog at WordPress.com.
healthcarereimagined
Blog at WordPress.com.
  • Subscribe Subscribed
    healthcarereimagined
    Join 149 other subscribers

    Have a WordPress.com account? Log in now.

  • healthcarereimagined
    View site in Reader
    Manage subscriptionsSign upLog in
    Report this content
    Collapse this bar
Loading Comments...