Opinion
02 May 2023 7 mins
Leading complex, interrelated digitive initiatives is challenging enough without setting back your strategy by falling prey to these common DX leadership mistakes.

Despite the best of intentions, CIOs and their organizations often struggle to deliver business outcomes from digital transformation strategies. According to research firm Gartner, 89% of corporate boards say digital is embedded in all business growth strategies, but only 35% of organizations are on track to achieve digital transformation goals. And while KPMG reportsthat 72% of CEOs have aggressive digital investment strategies, McKinsey details a harsh reality that 70% of transformations fail.
Stats such as these raise the question: How can CIOs and digital transformation leaders better recognize failure signs and proactively address issues?
My experience leading many digital transformations is that failures stem from a series of derailments, many of which are inadvertent. Even if digital transformation leaders avoid outright failure, these derailments delay initiatives, create avoidable organizational stress, and often yield underwhelming business outcomes.
Five years ago, I shared that the No. 1 reason digital transformations fail is that executives fail to recognize that digital initiatives are bottom-up transformations that require change across the organization. Employees must understand the why behind digital strategies and have incentives to participate in transformation initiatives. CIOs like to say, “Digital transformation is a journey,” but I believe leaders must strive to lead transformation as a core organizational competency.
CIOs can’t be involved in every strategic discussion or dive into every initiative’s details, but there are several high-level signs that indicate a digital transformation may be destined to underperform, especially as CIOs add initiatives. In my experience assessing digital transformations, the following five are the most common.
1. Prioritize too many initiatives without a shared vision
“One of the most common ways to derail digital transformation efforts is ignoring the importance of a clear strategy and defined goals,” says Arturo Garcia, CEO of DNAMIC.
CIOs must communicate strategy and goals when making investment cases and garnering support from the CEO, executives, and the board. As challenging as it is to get to a yes, it’s what comes next that often derails digital transformations at the very start.
CIOs must facilitate a discussion on priorities. Having too many number-one priorities sets unrealistic expectations with business stakeholders and stresses team leaders. Worse is when prioritized initiatives don’t have a documented shared vision, including a definition of the customer, targeted value propositions, and achievable success criteria.
When I survey transformation leaders and their teams, I privately ask each person three questions: What’s your top priority, why is it important, and how many other initiatives are also taking up your time? The risk of derailments increases as I hear inconsistent answers or too many conflicting priorities.
2. Neglect to set collaboration and communication principles
Digital transformations can start with one initiative, defined goals, and a dedicated team. But CIOs are under pressure to accelerate and find digital transformation force multipliers. That means growing the number of leaders and teams that can plan innovations and deliver transformative impacts.
“Innovation does not happen in isolation: It occurs when organizations encourage and nurture it, often with processes to enable nontraditional ways of thinking, working, and the space to try out ideas in a safe environment,” says Hasmukh Ranjan, CIO of AMD.
Here’s how I spot derailments: Ask initiative leaders to share access to their roadmaps, agile backlogs, collaboration tools, stakeholder communications, and internal documentation. I seek information completeness, communication consistency, and ease-of-use factors. When CIOs struggle to grow beyond one transformation initiative, the root cause is often gaps in collaboration and communication principles.
3. Customize solutions to meet everyone’s requirements
Many organizations use agile methodologies when planning and executing digital transformation and assign multidisciplinary teams to manage releases, sprints, and backlogs. But are product managers developing market- and customer-driven roadmaps and prioritized backlogs? Unfortunately, many digital transformation initiatives succumb to stakeholders dominating priorities with neverending wishlists and poorly defined requirements.
One recent study shows that only 50% follow a product-centric operating model focusing on customer centricity and delivering delightful customer experiences. “Companies that leverage high-quality data, center their enterprise around responsible risk-taking, and organize around products are the most likely to experience profitable growth from their digital transformation journey,” says Anant Adya, EVP of Infosys Cobalt.
Subject matter experts and internal stakeholders should be contributors to priorities and requirements, not decision-makers or backlog dictators. Digital transformations derail when CIOs miss the opportunity to establish and communicate product management responsibilities for creating and evolving market- and customer-driven roadmaps.
4. Underinvest in developing digital trailblazers
In its 2023 State of Digital Transformation report, TEKSystems found that 48% of tech and business decision-makers report needing to revise the nature of their organization’s talent base, and another 34% acknowledge needing new types of talent. “Organizations can derail their digital transformation journey by failing to map out goals, objectives, and tactics prior to launch and not valuing the right mix of IT and business stakeholders in the planning stages,” says Ricardo Madan, senior vice president at TEKSystems.
CIOs invest in skills development, and HR usually offers leadership development programs, but these approaches often don’t address the knowledge and skills needed to lead digital transformation initiatives.
Digital trailblazers, including product managers, program managers, architects, agile delivery managers, and data scientists, need specialized learning programs and coaching to build their confidence in handling transformation responsibilities. Derailments can happen when transformation leaders seize up when negotiating priorities, fail to facilitate decisions on requirements, or struggle when handling conflicts or blow-up moments. Digital trailblazers face many people challenges when guiding employees through a transformation, and CIOs should identify coaches and development programs to prepare their leaders.
5. Drive KPIs and data-driven decisions without a data strategy
Building digital products, improving customer experiences, developing the future of work, and encouraging a data-driven culture are all common digital transformation themes. Leaders should define new KPIs and OKRsthat help people understand the objectives and recognize how their work contributes to the organization’s transformation goals.
But there are common pitfalls, such as selecting the wrong KPIs, monitoring too many metrics, or not addressing poor data quality. “Having bad data, or an inability to realize the value and take action from data, is a surefire way for a digital transformation project to go south quickly, says Dwaine Plauche, senior manager of product marketing at AspenTech. “Without useful, contextual data that can be scaled and used throughout the organization, digital transformation efforts may simply become one-off projects that get stalled at the pilot phase, leading C-suite leaders to believe the technology was a failure or the investment was a waste.”
This derailment stems from having no defined data strategy or having one not aligned with digital transformation objectives.
Consider how it looks to nontechnical executives when every digital transformation initiative has customized dashboards, different KPIs, and metrics with underlying data quality issues. Instead of initiatives telling a cohesive story, it leaves results open to interpretation and challenges. The data strategy should include guidelines on the types of KPIs, standards for dashboarding metrics, and responsibilities for improving data quality.
The five derailments I focus on here fall within the CIO’s responsibilities to address. They are important for CIOs leading multiple transformation initiatives to deliver against several business strategies. The practices that worked when digital transformations started small with one initiative must evolve into a digital culture and a transformation operating model. It’s in this transition where increasing derailments can lead to digital transformation failures.
Isaac Sacolick, President of StarCIO, a digital transformation learning company, guides leaders on adopting the practices needed to lead transformational change in their organizations. He is the author of Digital Trailblazer and the Amazon bestseller Driving Digitaland speaks about agile planning, devops, data science, product management, and other digital transformation best practices. Sacolick is a recognized top social CIO, a digital transformation influencer, and has over 900 articles published at InfoWorld, CIO.com, his blog Social, Agile, and Transformation, and other sites.
The opinions expressed in this blog are those of Isaac Sacolick and do not necessarily represent those of IDG Communications, Inc., its parent, subsidiary or affiliated companies.

April 25, 2023 | Article
By Aamer Baig, Sven Blumberg, Arun Gundurao, and Basel Kayyali
Develop data-driven insights to build a strategy for paying down the tech debt that stands in the way of business modernization.
A large B2B business faced an agonizing quandary: its leadership team was considering dozens of modernization initiatives that could bring a $2 billion margin expansion opportunity. But 70 percent of them depended on technology that would cost a staggering $400 million—much higher than expected. The reason for such a high price tag? Its tech stack had become massively complex after years of building quick workarounds and one-off solutions to favor speed over good design for the long term.
This reality forced the company to ratchet back its investment to about $300 million and walk away from 25 percent of the potential margin expansion. Cutting back on these tech initiatives had a compounding effect, though, because the unaddressed issues would continue to fester and undermine future projects. That became painfully clear two and a half years later when the team was able to complete only half of the planned work because of ongoing technical issues.
This example is all too typical across businesses today. As much as 71 percent of the impact from business transformations depends on technology, according to our research (Exhibit 1). This is particularly concerning given that so many companies need to modernize if they are to remain competitive.

While many companies understand the importance of technology in meeting their strategic goals, the silent killer of technology modernization efforts—technical debt—often stands in their way. Technical debt is basically the “tax” a company pays on any development to redress existing technology issues, and it accounts for about 40 percent of IT balance sheets, according to our research. Companies pay an additional 10 to 20 percent to address tech debt on top of the costs of any project.1 Some 30 percent of CIOs we surveyed believe that more than 20 percent of their technical budget ostensibly dedicated to new products is diverted to resolving issues related to tech debt.
As such, the benefits of paying down technical debt can be game changing. They include: freeing up engineers to spend as much as 50 percent more of their time working on value-generating products and services; reducing costs by cutting back on time needed to manage complexities; and improving uptime and resiliency. Cutting back tech debt is the key to becoming tech forward: a company where technology is an engine for continual growth and productivity.
So how can organizations begin paying down their technical debt? It starts with insights—knowing which aspects of technical debt are most tied to value offers a path into a more strategic approach to resolving technical debt.
A closer look: Technical debt’s vicious cycle
Technical debt is the result of a range of practices. These can include making temporary fixes that inevitably become permanent, not updating solutions that become outdated, favoring fast technology delivery over long-term benefits, or implementing one-off solutions to meet business priorities. Many of these decisions make sense at the time and are necessary. But complexity builds, and future projects become more difficult. This vicious downward cycle translates into an enormous cost for the business in the form of lost opportunities and wasted resources (Exhibit 2).

These layers of tech debt create a huge drag on any business transformation effort—it’s like trying to run while pulling an increasingly heavy anchor behind you. CIOs estimate that tech debt amounts to 20 to 40 percent of the value of their entire technology estate (before depreciation), according to our research.2Companies in the bottom 20th percentile in terms of tech debt severity are 40 percent more likely to have incomplete or canceled IT modernizations than those in the top 20 percent.
Escaping this vicious cycle is not easy. Knowing where and how to start is a serious challenge. A poorly sequenced approach can easily result in time and money spent without much change to the tech debt profile. The business side of the house may be overwhelmed by the task and want to delegate the problem to IT, but both sides will need to work together to identify solutions that allow the organization to compete and build value.
Article link: https://www.mckinsey.com/capabilities/mckinsey-digital/our-insights/breaking-technical-debts-vicious-cycle-to-modernize-your-business?
Oracle Health Chairman David Feinberg sat down with Healthcare Dive at HIMSS to give an update on the Cerner-Oracle integration.
Published April 21, 2023

David Feinberg has worn multiple hats in his three decades in healthcare, including chief executive of major health systems UCLA and Geisinger and leader of Google Health. Most recently, Feinberg stepped up as CEO of EHR company Cerner in 2021, as the vendor looked to reorient from a focus on legacy EHR systems to becoming a software-as-a-service business.
A few months after Feinberg started, Cerner announced it was being acquiredby software giant Oracle, for $28.3 billion, as Oracle looked to expand its cloud business in the hospital market.
Healthcare Dive chatted with Feinberg — now chairman of Oracle Health — at the HIMSS conference in Chicago about the company’s integration, Oracle’s progress in creating a national health records database and Cerner’s plan to help auto-adjudicate payment disputes between payers and providers.
This interview has been lightly edited for clarity and brevity.
HEALTHCARE DIVE: Oracle closed its buy of Cerner in June, calling it an anchor asset as Oracle elbows further into the healthcare space. How has the integration gone?
DAVID FEINBERG: It’s gone way better than I thought. My bias is oftentimes technology companies think those of us in healthcare are not really sophisticated, and if we did things their way things would get better. Oracle has been the exact opposite. So the integration has been pretty smooth. I think part of the reason is that two-thirds of the people at Oracle are there via acquisition, so Oracle knows how to do this.
I think there’s great excitement for what Oracle can bring from a technology standpoint, coupled with Cerner’s long-standing history of partnering with health systems around the world. The timing just feels right.
When the deal closed, Oracle said it planned to focus the unit on medical software usability and voice-enabled user interfaces, and would expand Cerner’s business to more countries. Can you give me an update on these priorities?
FEINBERG: I remember those three things being listed. It’s more now. Our vision is to create a cloud-enabled health platform that brings all kinds of information together to make individuals and communities healthier around the world. That includes the electronic health record, and Oracle’s human capital management, enterprise resource planning, supply chain management, claims processing, clinical trials — so we have a platform that normalizes data and then tees it up for whoever needs it, a mom taking care of kids at home, or a government looking at public health issues.
Oracle founder Larry Ellison announced Oracle plans to build a health records database to link the thousands of separate hospital databases. How is this going?
FEINBERG: It’s going great. We have a new product we just launched called Seamless Exchange. A clinician gets a new patient, and this patient has records from multiple places. With one click, we take all of that information and we make a longitudinal story of that patient. In all that, there’s a lot of duplicate information — it may say 40 times that you had a knee surgery. So we de-duplicate it. And if that information’s from a trusted source, like another health system I trust, it automatically writes it into the record for me.
To Larry’s vision of everybody having their records available in a secure way, no one wants all their medical records, because I don’t want to see 900 times the same cholesterol level that I had drawn. So the first step in getting to that vision is organizing disparate data sets and making them accessible and useful, and it’s EHR agnostic through an API.
What are the next steps?
FEINBERG: I don’t ever want to be more visionary than Larry Ellison. But I think it’s even broader than what he’s saying. Because not only do I want my whole electronic health data, I want all information that’s applicable to my health. That includes social determinants, that includes claims processing, so many other pieces of information — like, if there’s a claim on me, but not a documented note, that shows I had a cardiac ablation. So it’s more than just your EHR information from multiple sources, it’s multiple sources of information that pertain to your health.
How will Oracle pull that additional data?
FEINBERG: Oracle Financial Services processes 80% or 90% of the world’s credit card transactions. All that is is an agreement between the merchants and the banks to let Oracle be in the middle and make that transaction happen. In healthcare, there’s so much friction between the payer and the provider. So they agree on a contract, and a patient comes in and gets care. The coding takes place on the provider side, it goes over to the payer side, and they deny. Why did that happen? They each interpreted the contract a little differently. That never happens with a credit card.
Article link: https://www.healthcaredive.com/news/david-feinberg-cerner-oracle-health-records-database/648262/
By NATALIE ALMSAPRIL 21, 2023
The management of the government’s IT acquisitions and operations is also on the Government Accountability Office’s biennial high risk list update this year, as it has been since 2015.
The Government Accountability Office released its biennial list of government operations considered high risk on Thursday.
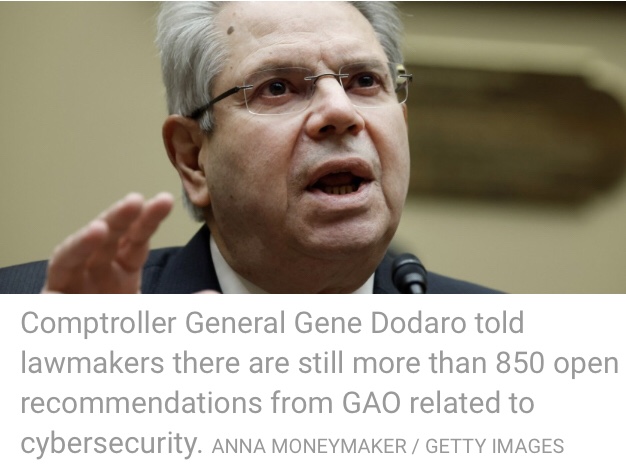
Cybersecurity is on the list, as it has been since 1997. Comptroller General Gene Dodaro told lawmakers Thursday that, “The federal government is still not operating at a pace commensurate with the evolving threat.”
There are over 850 open recommendations from GAO related to cybersecurity – which Dodaro called out as an area needing significant attention – that haven’t been implemented, including 52 of 133 recommendations deemed high priority for agency and department heads by GAO.
Cybersecurity is one of 34 areas considered to be high risk. The list also includes other tech-related areas. NASA has improved its acquisition management, for example, but still has work to do, as do the departments of Defense, Veterans Affairs and Energy.
The Department of Homeland Security’s IT and Financial Management and DOD business systems modernization are also called out on the list.
In terms of cybersecurity, the White House released a new national cybersecurity strategy in March.
But Dodaro emphasized the importance of the forthcoming implementation plan promised by the administration, listing off unanswered questions – “Who’s responsible for what? How much money do we need? How are we going to measure performance and improvements in those areas?”
Other cybersecurity challenges delineated in the report include “fully developing” privacy management programs in agencies and securing the government’s own systems and those of critical infrastructure sectors.
“I don’t think the federal government really knows the preparedness of many of these important sectors of our economy as much as they should, in terms of the electricity grid, the communications networks, the financial markets and many other areas,” said Dodaro of critical infrastructure cybersecurity. “There needs to be much more partnership between the federal government and the private sector in this area.”
GAO witnesses also talked with lawmakers about shortages in the cybersecurity workforce, something the White House’s Office of the National Cyber Director is working on a plan to address.
The management of the government’s IT acquisitions and operations has also been on the list for eight years, although GAO noted that OMB and agencies have actually made progress on implementing these recommendations since the last update, with 73% fully implemented.
Still, “this is kind of a vexing problem,” said Dodaro. “A lot of these systems weren’t built with security and so it’s complicating our ability [in the] cybersecurity area. The cost is expensive. There are efforts to try to replace them, but they often fail because of lack of discipline [and] IT management issues.”
GAO says that 15 federal agencies haven’t implemented recommendations around the role and authorities of their chief information officers, although there have been improvements in “aligning the CIO with agency leadership,” said Nick Marinos, managing director of GAO’s IT and cybersecurity team. That gives them “the ability to see across a federal agency where IT dollars are being spent,” he said.
Planning around the tech workforce and modernizing or replacing legacy systems are also areas that have open recommendations, and there’s also an unrealized push from GAO for Congress to formalize the federal CIO position.
“Having a strong federal CIO presence would allow that individual to bring federal agencies to the table… to know not only are they spending money wisely, but if there are opportunities to leverage that buying power,” said Marinos. “And then the other side of it is ultimately to hold CIOs accountable and federal agency heads accountable towards those CIOs as well.”
Sixteen high risk areas total saw improvements since 2021, said Dodaro. Two topics – the 2020 Decennial Census and the Pension Benefit Guaranty Corporation – were removed from the list completely, and one added – management of the federal prison system.
GAO also added the Department of Health and Human Services’ leadership and coordination during health emergencies, as well as the unemployment system to the list in 2022.
In terms of what it takes to make progress, Dodaro wrote in his testimony that, “it has typically involved three essential elements: congressional action or oversight, commitment from top leaders at agencies and active involvement by the Office of Management and Budget.”
Article link: https://www.nextgov.com/cybersecurity/2023/04/cybersecurity-still-high-risk-gaos-book-after-over-25-years/385473/
Companies including OpenAI and TikTok have signed up to a new set of guidelines designed to help them be more transparent around generative AI.
By Melissa Heikkila February 27, 2023
A group of 10 companies, including OpenAI, TikTok, Adobe, the BBC, and the dating app Bumble, have signed up to a new set of guidelines on how to build, create, and share AI-generated content responsibly.
The recommendations call for both the builders of the technology, such as OpenAI, and creators and distributors of digitally created synthetic media, such as the BBC and TikTok, to be more transparent about what the technology can and cannot do, and disclose when people might be interacting with this type of content.
The voluntary recommendations were put together by the Partnership on AI (PAI), an AI research nonprofit, in consultation with over 50 organizations. PAI’s partners include big tech companies as well as academic, civil society, and media organizations. The first 10 companies to commit to the guidance are Adobe, BBC, CBC/Radio-Canada, Bumble, OpenAI, TikTok, Witness, and synthetic-media startups Synthesia, D-ID, and Respeecher.
“We want to ensure that synthetic media is not used to harm, disempower, or disenfranchise but rather to support creativity, knowledge sharing, and commentary,” says Claire Leibowicz, PAI’s head of AI and media integrity.
One of the most important elements of the guidelines is a pact by the companies to include and research ways to tell users when they’re interacting with something that’s been generated by AI. This might include watermarks or disclaimers, or traceable elements in an AI model’s training data or metadata.
Regulation attempting to rein in potential harms relating to generative AI is still lagging behind. The European Union, for example, is trying to include generative AI in its upcoming AI law, the AI Act, which could include elements such as disclosing when people are interacting with deepfakes and obligating companies to meet certain transparency requirements.
Related Story
A quick guide to the most important AI law you’ve never heard of
The European Union is planning new legislation aimed at curbing the worst harms associated with artificial intelligence.
While generative AI is a Wild West right now, says Henry Ajder, an expert on generative AI who contributed to the guidelines, he hopes they will offer companies key things they need to look out for as they incorporate the technology into their businesses.
Raising awareness and starting a conversation around responsible ways to think about synthetic media is important, says Hany Farid, a professor at the University of California, Berkeley, who researches synthetic media and deepfakes.
But “voluntary guidelines and principles rarely work,” he adds.
While companies such as OpenAI can try to put guardrails on technologies they create, like ChatGPT and DALL-E, other players that are not part of the pact—such as Stability.AI, the startup that created the open source image-generating AI model Stable Diffusion—can let people generate inappropriate images and deepfakes.
“If we really want to address these issues, we’ve got to get serious,” says Farid. For example, he wants cloud service providers and app stores such as those operated by Amazon, Microsoft, Google, and Apple, which are all part of the PAI, to ban services that allow people to use deepfake technology with the intent to create nonconsensual sexual imagery. Watermarks on all AI-generated content should also be mandated, not voluntary, he says.
Another important thing missing is how the AI systems themselves could be made more responsible, says Ilke Demir, a senior research scientist at Intel who leads the company’s work on the responsible development of generative AI. This could include more details on how the AI model was trained, what data went into it, and whether generative AI models have any biases.
The guidelines have no mention of ensuring that there’s no toxic content in the data set of generative AI models. “It’s one of the most significant ways harm is caused by these systems,” says Daniel Leufer, a senior policy analyst at the digital rights group Access Now.
The guidelines include a list of harms that these companies want to prevent, such as fraud, harassment, and disinformation. But a generative AI model that always creates white people is also doing harm, and that is not currently listed, adds Demir.
Farid raises a more fundamental issue. Since the companies acknowledge that the technology could lead to some serious harms and offer ways to mitigate them, “why aren’t they asking the question ‘Should we do this in the first place?’”
Article link: https://www.technologyreview.com/2023/02/27/1069166/how-to-create-release-and-share-generative-ai-responsibly/?
GSA Administrator Robin Carnahan explains how her agency is committed to ensuring government technology works for everyone and taking responsibility when things go wrong.

BYROBIN CARNAHAN. APRIL 24, 2023
As we emerge from the pandemic, millions more Americans have come to rely on digital delivery of services, including those from government. They expect publicly funded technology and websites that they can trust. They want interactions to be simple, streamlined, and secure. And that’s exactly what they deserve.
At the U.S. General Services Administration, which I lead, our Technology Transformation Services (TTS) works across government to help federal agencies meet that expectation. This work represents an essential component of what has always been GSA’s core mission: helping government deliver efficiently and cost-effectively for the American people. In other words, providing a strong digital infrastructure that gives the public what they need is a natural evolution of GSA’s long-standing work to deliver value through federal acquisitions and real estate.
As we do this work, we’re guided by some fundamental principles. We believe government websites should work for all Americans, including vulnerable communities. We believe government technology should be developed for the public benefit, not private gain, and that individuals – not corporations – should control access to their own sensitive information.
Above all, we believe that accessible, equitable, and secure digital infrastructure – developed for the public by an accountable government – is vital to delivering the services Americans need, when they need them.
Our commitment to accountability also means owning up to mistakes and taking responsibility when we fail to meet the high standards taxpayers expect and deserve.
For example, over a year ago, GSA leadership found out that Login.gov, a secure sign-on service operated out of TTS, had been representing that it was compliant with a technology standard when, in fact, it wasn’t.
Misrepresentations like that are unacceptable, and we spent the last year working to bolster trust and transparency with Login.gov customers, to strengthen oversight and management controls, and to take other steps to prevent something like that from happening again. This included alerting the Inspector General, putting in place new leadership, and improving the Login.gov product offering. As a result, Login.gov is now stronger than ever — offering enhanced anti-fraud controls, 24×7 bilingual customer support, and in-person identity verification at over 18,000 U.S. Postal Service Post Office locations nationwide.
We know there is still work to be done to restore trust with our customers and the public, and I’m committed to seeing that work through and to delivering secure, effective, and accessible digital services to the millions of people we serve.
The ability of the American people to securely and equitably interact with their government online is critically important, and we are committed to making sure government technology works for everyone, including those who need it the most.
That’s why we’re working in a comprehensive way to strengthen and expand our technology programs so they can deliver even more effectively for the American people.
We established a new Technology Law Division within the Office of the General Counsel to support programs like Login.gov. We’re strengthening the leadership team TTS-wide, hiring a new TTS director in December and, this month, a new deputy director and a new senior adviser for operations. And we’re ramping up our efforts to deliver impactful, lasting solutions that save money for taxpayers and help agency partners deliver excellent customer experiences for the American people — from veterans seeking healthcare to seniors accessing Social Security benefits to farmers and ranchers needing consistent and streamlined information.
After all, technological advances in areas like artificial intelligence make it more important than ever that our government recruits talented, dedicated technologists to thoughtfully and responsibly buy, build, and oversee government technology in ways that are consistent with our values and serve the public interest.
Turning away from that responsibility is not an option, and this administration will continue to scale up its commitment to technology modernization as we prepare for the future.
Robin Carnahan currently serves as Administrator of the U.S. General Services Administration.
Article link: https://fedscoop.com/americans-deserve-government-tech-that-delivers/
Blockchain is considered an essential underpinning of emerging innovations like Web3. Yet some early adopters of the distributed ledger technology have experienced high-profile failures over the past 18 months, most notably in cryptocurrency and early enterprise applications.
As companies wonder where to begin, a new research briefing from the MIT Center for Information Systems Research outlines four business approaches to blockchain:
• Wait and see. This approach is suitable for companies in highly regulated industries that are risk-averse. These businesses are often content to leave early experimentation to others until there is clarity around profitability, regulations, and other market forces.
• Experiment. An exploratory path enables companies to try out blockchain-based products and services on a small scale without risk to mission-critical operations.
• Provide targeted offerings. This approach goes beyond experimentation to expand blockchain into targeted areas — typically those that aren’t mission critical.
• Go all in. This is the preferred route of startups or industry disruptors committed to building new businesses based on decentralized blockchain-enabled products and services.
When it comes to building new business opportunities, 80% of companies succeed in ideating and incubating new ideas, but only 16% successfully scale them, according to research by innovation advisory firm Change Logic.
Writing recently in MIT Sloan Management Review, Change Logic’s Andy Binns and Christine Griffin shared insights from their study of 30 successful and unsuccessful corporate ventures. They found that most successful companies follow a “scaling path” that provides leaders with a language and structure to reach their innovation goals.
Scaling paths comprise a clarity of ambition; an understanding of assets needed to access the customers, capabilities, and capacity the new business requires; and a willingness to use a variety of techniques to assemble those assets into a coherent strategy for attaining scale.
This approach to scaling helps leaders of new ventures learn and iterate as they go, adding new options and eliminating those that become dead ends, the authors write.
“Scaling is both art and science, and with the help of a scaling path, it can be managed with the same level of discipline and success that we have come to expect of ideation and incubation,” they conclude.
Minority households in the U.S. face significant hurdles when trying to buy a home. Government figures show that in the second quarter of 2022, the homeownership rate for white households was 75%, compared with 45% for Black households.
It will take “a big pivot” to close a gap that large and persistent, said Edward Golding, executive director of the the MIT Golub Center for Finance and Policy. “We really do have to make fundamental changes.”
Toward that end, the Golub Center and the MIT Department of Urban Studies and Planning recently hosted a lecture series on creating more equality in the U.S. housing market. Some ideas offered by experts in civil rights, lending, and government:
• Modify underwriting requirements to account for the effects of past discrimination and racism. • Involve a wider variety of banks, such as regional banks and those that are part of the Federal Home Loan Bank System, in government home loan programs.
• Prioritize community reinvestment in the Deep South, a region one local lender characterized as “capital-starved” and lacking philanthropic giving and major banks.
• Create public banks managed by the government to build community wealth and bring more affordable housing to underserved markets.
Article link: https://www.linkedin.com/pulse/4-business-approaches-blockchain-mit-sloan-school-of-management
By AARON BOYDAPRIL 25, 2023
Agencies are approaching the White House’s mandate with an eye for getting important information and access to as many people as possible.
While the Biden administration’s biggest customer experience—or CX—effort to date is being led by technologists in the Office of Management and Budget, the nine “Life Experience” projects are, for the most part, decidedly low-tech.
The administration is pursuing major improvements to the way Americans interact with the government, beginning with nine projects across five “life experiences,” with a focus on improving that customer interaction without regard for traditional barriers and siloes erected around agencies.
“Technology underpins everything we do as the federal government,” Federal Chief Information Officer Clare Martorana told Nextgov in an interview. However, “it isn’t necessarily the individual piece of software or the code we’re shipping. It comes down to how are we bringing all of these people along on the journey: both our vendor partners—the external people that are helping us build technology—but also our federal employees—making sure that they have the right knowledge and training—and building off of the best practices … that [the U.S. Digital Service] drives across government.”
Those efforts are only tangentially related to technology and, of the nine projects at the center of the Life Experience CX program, only four of them have any meaningful technology component.
That is a feature of most of these projects, not a bug.
“How do we ensure that as we’re building out solutions we’re building them in a way that it’s accessible and addresses everybody in the population and does so equitably—not just the most tech savvy people with the newest phones and the fastest broadband,” USDS Administrator Mina Hsiang told Nextgov.
“We all have different degrees of technological access, technological literacy and engagement with a bunch of other aspects of the economy that affect how we appear in technological spaces,” such as a person’s credit history—or lack thereof—Hsiang noted. “All of these things affect your access to different tools as they’re developed.”
For example, under the program targeted toward families with children in the 0-5 age range, only one of three projects relies on technology: a pilot to create a text messaging service that state-run programs can use to inform families of available benefits and send reminders about upcoming deadlines.
While the program promises to help families who are most in need of these benefits, not all have access to a cell phone or the necessary broadband service to take advantage. That said, cell phone access among low-income Americans is incredibly high. A 2021 Pew survey found 97% of Americans had a cell phone—a number that held across multiple low-income brackets, including people making less than $30,000, $30,000-$49,999 and $50,000-$74,999
The 0-5 program doesn’t have the resources or authority to provide cell phones and service to those without, officials told Nextgov, but that doesn’t mean those people will be left without help.
“All three of our portfolio projects under 0-5 are designed to be responsive to feedback we heard directly from families,” said Maya Mechenbier, project lead at USDS for the 0-5 projects. “We asked about modes of communication and support in which we could support families through this life experience—and modes of communication that fit into their lives. So, meeting families where they are.”
For the majority, the best mode of communication is SMS, which sparked creation of the U.S. Notify program through the General Services Administration’s Public Benefits Studio.
But the 0-5 program wanted to ensure they reached everyone, prompting the other two low-tech projects: offering a physical newborn supply kit with things every family needs in the early days after a baby is born and creating a “benefits bundle” that social workers can help tailor to each family’s unique needs.
Even the choice to use SMS was guided by the preference toward low-tech. For example, email and other similar forms of digital communication require smart phones or computers and reliable broadband access, which can all create more barriers for low-income families. SMS—while still technically digital—offered the lowest-tech option.
“The theme here is that it doesn’t have to be too scary or too complicated,” one 0-5 program official told Nextgov.
“[If] I’m an individual who has just experienced a natural disaster or just lost my job, I don’t care about what the different agencies are and the programs at different agencies and which ones I might be eligible for. I have a need,” Hsiang said. “One of the interesting challenges for us to work through is how do we make those appear more seamless to the user.”
While in some cases that might mean creating a better website, fine-tuning an app or gathering better data for analytics, people and processes always come into play.
“I haven’t found a technology problem in government that we hadn’t solved many years ago in the private sector,” Martorana said. “We have policy, budget, legacy IT challenges, people who are unfamiliar with modern technology in [an] agency and haven’t had the opportunity to be trained or be exposed. … It’s as much the people and the process needing to change. It’s why I think this EO is one of the most significant things from this administration—in addition to equity.”
Martorana also stressed the importance of continuing improvement work long after these specific projects have wrapped—particularly when it comes to the technology components.
null
“If you’re not shipping code every day, every week, you have to build the discipline out to be able to achieve that,” she said. “Otherwise, you get so disconnected from your customer that you have to put customer demands on a backlog.”
Support from the top
Where there is a technology component, the administration is sending support from USDS—a group designed to parachute into other agencies to help with particularly complex or challenging IT deployments.
The group has a mixed success rate. It was established after a team of industry technologists joined the Obama administration to fix the healthcare.gov portal and has had successful offshoots at the Veterans Affairs Department andDefense Department; meanwhile at other agencies—like the Small Business Administration—the engagements have been less successful.
For these CX projects, Hsiang said USDS can act as a bridge between siloed federal agencies.
“To a certain extent, we’re inventing a path forward. One of our capabilities is that we can work between agencies,” she said. “We can help bring agencies together and help provide some of that connective tissue and work through the complex questions.”
But the biggest support provided by USDS is institutional knowledge from folks who have done these things before—though usually from outside government.
“Obviously, USDS doesn’t have enough people to deploy to every single agency that has anything that they want to do in CX. But we really are focused on supporting agencies and helping provide capacity for major programs and consultations in areas where that’s helpful,” Hsiang said. “[We’re] bringing the expertise and folks who have done it in the past.”
The Federal CIO’s Office is helping with financial support, primarily through the Technology Modernization Fund, a central account managed by OMB and the General Services Administration from which agencies can borrow—or be granted—funds for impactful IT modernization projects.
The TMF Board set aside $100 million for CX projects, for which OFCIO is hoping the nine projects will apply.
“They are all eligible to apply,” Martorana confirmed. “We’ve been strongly encouraging them to apply. But each individual agency takes their own time in the process.”
Meanwhile, OMB is also working to connect agencies—through these nine projects and other CX efforts—going through similar experiences or working through similar problems.
“We don’t have to start at every agency on a blank piece of paper,” Martorana said. “That is why it’s really important that we’re writing these playbooks down.”
If these nine projects are successful, Martorana and Hsiang hope those playbooks will be the ignition for an explosion of CX programs throughout government.
“A lot of what we want to do is tell stories of how this can be successful,” Hsiang said. “The more that we have worked on this and we have agencies and programs where we have done this and it has gone well … it de-risks it and it makes it something that feel[s] like you can take it on.”
Barbara Morton, Veterans Affairs’ deputy chief veterans experience officer and lead for the Transitioning to Civilian Life project—who has been working on her agency’s customer experience issues since 2016—sees similar potential here.
Morton said, from her perspective, there are two main goals for the project:
“First and foremost, really responding to the pain points that we hear from transitioning servicemembers. We know in VA, data shows us that roughly half of transitioning servicemembers don’t engage with VA. … We’re curious why might that be,” she told Nextgov.
But there is a secondary potential benefit, as well.
“I love this as a pretty juicy, giant proof of concept,” she said. “To step outside of just the VA space, as well, and apply human-centered design insights and see how we can create solutions that cut across different agencies and bust the barriers—the siloes—of bureaucracy. … Understanding that for us—the collective ‘us’ in government—to be able to be what the people want us to be: Really give those services and support.”
She added that the aim is to understand how government as a whole can provide services “in a more human-centered way, rather than any of us feeling more like transactions.”
And that includes improving services for those who are not tech-savvy or tech-enabled.
“I do understand the concept of, ‘You want to provide as much bang for your buck with the resources you have,’ and maybe the digital option would be the most popular or the most widely utilized,” Morton said. “But that can’t eliminate our need and duty, frankly—and our opportunity—to think about the functional equivalent non-digital solution as well.”
This is the first in a multipart series exploring the Biden administration’s push to improve citizens’ experiences with government. The series will take a deeper dive on several projects mentioned in this article.
Article link: https://www.nextgov.com/cxo-briefing/2023/04/low-tech-side-bidens-push-improve-life-experiences-government/385564/
.

