healthcarereimagined

Envisioning healthcare for the 21st century

  • About
  • Economics

A new operating system for health care – MIT Technology Review

Posted by timmreardon on 07/20/2023
Posted in: Uncategorized.

A reimagined IT infrastructure for health care could reorient us from sickness to wellness.

By MIT Technology Review Insights

April 26, 2023

Health data is all around us. Your electronic health records (EHRs) include your medical issues, test results, vital signs, allergies, prescriptions, and surgeries. Your health insurer’s database collects the claims paid on your behalf. Your pharmacy may record your flu and covid-19 shots. Maybe a smartwatch counts your steps and measures your heart rate; perhaps a genetic testing company has your DNA. Some people have pacemakers that transmit information to their cardiologist or implanted sensors that continuously track their blood sugar.

What we don’t have is a way to make this data all work together—a “personal health ecosystem,” says Bharat Sutariya, MD, managing director in health care for Deloitte Consulting LLP and an emergency medicine specialist. The endocrinologist treating your diabetes doesn’t have ready access to your eye exam results, which could help them preserve your eyesight. Your phone might contain vital medical information that emergency room (ER) staff needs to properly take care of you, but it has to be able to connect with the hospital’s systems to transmit that data.

Dramatically better integration, however, is coming in the not-so-distant future, Sutariya says. And when it does, today’s health information management will seem as antiquated as sending a telegram. “The cloud infrastructure that’s becoming ubiquitous is going to unleash that potential,” Sutariya says. “If you choose to share your data, your doctor will know about your steps and your stress level from the apps you use, and smart pill packs will be able to record whether you’re taking your medication. If you have chest pain, paramedics will be able to access your records in the ambulance, and they’ll exchange pre-hospital intervention history with the receiving hospital. The ER doctor will have your treatment already staged because they’ve got your complete risk profile, and they’ll get you right to the cath lab.”

A new understanding of the power of connected health data may kick off this shift. In the U.S., for example, the historically decentralized nature of health care has been a blocker, but recent legislation mandating interoperable core EHR data and asserting patients’ ownership of their health data is changing this. 

“These two provisions have started a movement that I believe is unstoppable,” says Sutariya. “It’s a game changer already, because the law says providers must share this data anywhere that the patient—who owns the data—tells them to share it.” After an extended period of rulemaking, those provisions went into effect late in 2022.

Download the report

This content was produced by Insights, the custom content arm of MIT Technology Review. It was not written by MIT Technology Review’s editorial staff.

Article link: https://www-technologyreview-com.cdn.ampproject.org/c/s/www.technologyreview.com/2023/04/26/1071762/a-new-operating-system-for-health-care/amp/

What really works when it comes to digital and AI transformations? – McKinsey

Posted by timmreardon on 07/20/2023
Posted in: Uncategorized.

July 13, 2023 | Podcast

By Eric Lamarre, Kate Smaje, and Rodney Zemmel

McKinsey’s Rewireddistills the lessons from successful digital and AI transformations so companies can build competitive advantage.

DOWNLOADS

Article (7 pages)

By now, most leaders understand the importance—or, increasingly, the inevitability—of digital and AI transformation. But fewer executives are clear about how to knit systems, people, and processes together in the most productive way. McKinsey senior partners Eric Lamarre, Kate Smaje, and Rodney Zemmel have written Rewired: The McKinsey Guide to Outcompeting in the Age of Digital and AI (Wiley, June 2023) with that disconnect in mind. Rewired offers clear, customizable paths that organizations can take to succeed with their digital transformations—and stay nimble in the face of constant change.

The authors discuss the book on this episode of The McKinsey Podcast, which is hosted by McKinsey editorial director Roberta Fusaro.

This transcript has been edited for clarity.

https://omny.fm/shows/the-mckinsey-podcast/what-really-works-when-it-comes-to-digital-and-ai/embed?style=Artwork&uniq=2956Audio

Difficult but doable

Roberta Fusaro: A massive number of companies are going through some sort of digital transformation—just about 90 percent of them, according to McKinsey research. All with varying levels of success.

Rodney Zemmel: It is “show me the money” time for digital transformations. To succeed in a digital transformation, it needs to be a CEO agenda item. It needs to mobilize cross-functional teams across the company in a unique way. It’s going to need some investment to sustain it.

Roberta Fusaro: That’s McKinsey senior partner Rodney Zemmel. It’s pretty easy to define what needs to happen in digital and AI transformations. But not so easy to get it done, says McKinsey senior partner Kate Smaje.

Kate Smaje: It’s very easy in some ways to sort of put an additional lick of paint over everything you do and come up with the “what.” The how of it is incredibly hard.

Roberta Fusaro: Especially when you’re trying to keep up with the latest technology.

Eric Lamarre: Data architecture and all the technology around that has evolved furiously over the past 18 to 24 months.

Roberta Fusaro: That’s McKinsey senior partner Eric Lamarre. He, Kate, and Rodney have worked with hundreds of clients going through digital and AI transformations. Their new book, Rewired, was inspired by both the frustrations and bottom-line pressures that companies are facing as they try to digitize. The authors describe Rewired as a how-to manual that lets companies take matters into their own hands and compete successfully in the age of digital and AI.

Rodney Zemmel: Frankly, we’ve all read the business books where you read the intro chapter, and then there’s pages of the same thing, just more examples than there were in the intro chapter. This is not designed to be that.

Kate Smaje: It is not the theory. It’s the practicality of, what does it really take to move the needle? What does it really take to be a leader and not a laggard in this space? And how do you make sure you’re not one of the vast majority that stalls in their transformation in some way, shape, or form? Or, if you have, what’s the unlock? What’s the pivot that’s going to get you out of that?

Forget the short-term fixes

Roberta Fusaro: For companies feeling stuck, some pixie dust probably sounds pretty good. But companies can’t just wave a magic wand . . .

Kate Smaje: . . . and end up with architecture overnight. Many of our clients are suffering with huge swaths of technology debt. And often what is slowing them down today is not actually their ability to create the latest application, but all of the integration complication that’s sitting underneath that.

Roberta Fusaro: Technology debt is part of the issue, but what really hobbles companies is the lack of focus on longer-term measures and the focus on value. A company has to measure its digital and AI transformation . . .

Rodney Zemmel: . . . with the same degree of rigor that you would measure any cost or revenue transformation. And that’s the first step in taking it from something hard and mysterious into something practical.

Roberta Fusaro: It also means recognizing that digital transformations are ongoing.

Kate Smaje: One of the things that actually annoys me about the term “digital transformation” is it has this connotation that at some point I am done, right? I don’t think you’re ever done with digital transformation. It’s a muscle that you’re constantly building and you’re constantly honing to get better at.

I don’t think you’re ever done with digital transformation. It’s a muscle that you’re constantly building and you’re constantly honing to get better at.Kate Smaje

Learn to speak ‘technology’

Roberta Fusaro: Eric Lamarre agrees and says his golden rule for leaders beginning a digital transformation is to get educated.

Eric Lamarre: You don’t start anything other than take your top team and go and learn for three, four, five months. What does that mean, go and learn? Go visit other companies that have done this, that are further along their journey. Now, start to create a common language: What is a data engineer?

What’s a technology stack? What do you mean by data architecture? What does it mean when you say “track the value”? How do we do that for a digital solution? You have to start to create a common language so that all the team players play the same sport.

Roberta Fusaro: The leader of that team is the CEO. And that’s where some rewiring kicks in.

Rodney Zemmel: The world is going from, you have a CIO on your team and this is the task of the CIO who is maybe joined with a business leader, to technology being fully embedded in the business. Business leaders need to be technology leaders.

Roberta Fusaro: And so we see a shift from chief information officer, or CIO, to CEO. A McKinsey survey from last year revealed that success with digitization is more likely when you’ve got C-suite leaders who understand tech—even a little bit. A company’s chance of . . .

Rodney Zemmel: . . . ending up in the top quartile of economic performers are much higher than if you’ve got one or two tech-savvy members of your team.

Eric Lamarre: I see the CEO as the chief orchestrator. There’s a dance. Everybody’s got to do their part, otherwise the value is not going to be there. And so that’s the primary job of the CEO: raise expectations, set a drumbeat, and get the dance to unfold.

Rodney Zemmel: So your orchestra analogy is right in that the CEO needs to get the team to actually align on the business-led technology road map. And that, then, needs to be a contract for how they all work together to really drive it, rather than they just start the music and then wave from the side.

Roberta Fusaro: Kate says that when CEOs model a learning mindset, their organizations can transform more quickly.

Kate Smaje: And one of the differences I see between CEOs that are getting it right and getting it wrong is when something does go wrong, rather than saying, “Why did that happen? What was the problem here?” they say, “What can we learn from it?” And just that slight nuance in the question that they ask can have a massive impact on the cultural adherence to the transformation.

Talent at the center

Roberta Fusaro: And the authors make no bones about it—every digital transformation is a people transformation at its core.

Kate Smaje: This doesn’t have to be an entirely new team. There’s a large component of this, of, who can I upskill? Who could really get to a different level on this? How do I take some of the capabilities I have and maybe make them more technology enabled without having to throw the baby out with the bathwater?

And for those trying to hire from outside the organization, I think one of the most common mistakes that I see is that the effort goes on the recruiting pipeline. And don’t get me wrong; that’s hard. But people over focus, right? They’re 99 percent focused on, how do I get them in the door? And where I see the best players work is when they’re about 50–50 of, how do I get them in the door, and then how do I make them wildly successful once they’re here?

Roberta Fusaro: Rethinking some elements of talent management can help, such as . . .

Kate Smaje: . . . how you remap career pathways, for example. How you think about compensation models, and really rewarding skills versus tenure, or time-in-role and so on.

Roberta Fusaro: Eric adds that when it comes to compensation, it’s important to understand the nuances of the job. For instance, if you look at data engineers . . . 

Eric Lamarre: Not all data engineers are the same. There are data engineers who are at the very top of their field. They have a breadth of tools that they have mastered. They are really thought leaders in the space. They are problem-solvers extraordinaire. They have a track record of developing real, working products, based on data. And then you have people who are more novices. They are just starting out. Your ability as a company to tell the difference between this one and that one is fundamental to be able to pay them differently, because otherwise, you’re unfair.

Roberta Fusaro: This differentiation can help leaders manage expectations.

Eric Lamarre: You can tell people, “I’m paying you at this level because these are the things that I know you’re able to do. But if you want to be paid at this level, that’s what I would want to be able to do.” And you’re able to have a variety of profiles live under the same roof.

Roberta Fusaro: To ensure productivity under that roof, the CEO can pick from one of three core operating-model designs. They’re all good; it just depends on what works best for the company. Choice one is to run a bunch of teams in a kind of digital factory model.

Eric Lamarre: What is that exactly? Essentially it’s a construct where you’re still running small cross-functional teams. People from the business come from their position to be inside those teams. People from technology come inside those teams. And then you share some commonality around data and infrastructure services and things like that. But it tends to be more of a stand-alone unit where people go to do the job of developing solutions.

Roberta Fusaro: Choice two is called the product and platform model. It’s similar to the digital factory option and it’s the model favored by more and more tech-intensive companies, such as banks, retailers, and, of course, software companies.

Eric Lamarre: This time it’s everybody in the business and operations side, and everybody in the technology side who gets regrouped into these small teams and they start to develop technology-based solutions.

Roberta Fusaro: The third model is called enterprise-wide agility. The benefits of agile—or the use of small, customer-focused teams that continually test and learn—shouldn’t be confined to tech-intensive parts of the company. Other business functions can use it to their advantage, too. This model requires a serious multiyear commitment by the CEO. But no matter which model the CEO chooses, each relies on a critical role: the product manager.

Eric Lamarre: The product manager becomes quite important in figuring out, “Where’s the need? What are we going to develop, in what sequence? And how are we going to make sure it’s going to get adopted?” And you’re going to say, “OK, that’s obvious. We need those. I’d like three dozen.” But it’s hard to get for an established company because this is not a role that you can hire so easily from the outside. Why? Because having knowledge of the enterprise, knowledge of the business, the customers, the process, the operations, is quite valuable in playing that role of “mini-CEO.”

Rodney Zemmel: This is a well-rounded skill set of people who can lead technical work, people who can understand and derive customer insights and bring those two things together to set the right direction for a product.

Roberta Fusaro: And product managers don’t just execute orders. They synthesize.

Kate Smaje: Often, getting that product lead role right can involve tension, partly because maybe the organization’s used to, when they’re developing technology, throwing it over the fence and saying, “Here’s my set of requirements. Go build me X.” And that’s not the role that the product owner is there to do. They are there to really understand, what are the outcomes that we’re trying to achieve? And they will find the best solution to get to those outcomes, not just be given a menu of requirements for how to do it.

Roberta Fusaro: Those outcomes should meet the needs of the entire organization—not just the technology team.

Kate Smaje: Whether that’s data, software products, applications, whatever it may be, perhaps even ways of working in terms of code. Ultimately, what you want is the business, the user, the end user—wherever they happen to sit—to be able to draw on that as fast as possible, right? Because you’re also trying to think about how to make sure that you have upskilled the people who will need to draw on it, and that you’re thinking about a modernized, reusable technology stack. So every component that you have, or as many as possible, should be reusable. They should be modular in how that works. And that’s a very different architecture from what most companies have.

Roberta Fusaro: At the end of the day, any model the CEO chooses must be resilient and positioned for growth.

Democratizing data

Rodney Zemmel: It’s very easy to hire some data scientists and to come up with some clever algorithms for doing something in your business well. But, again, you run into the scaling problem. It becomes incredibly costly and organizationally complex to scale. But from a technology standpoint, instead you could really push on reuse at the code base you’re developing. At McKinsey, we find that the solutions we develop for our insurance clients have a more than 50 percent overlap with the code base that we use with our mining clients. There are big components that are fully reusable. How do you make sure that when you’ve developed your model, it’s stable? That, as the world changes or the data changes, it’s not doing crazy things. How do you make sure that it continues to be valid?

Roberta Fusaro: One way is to think about how you’re managing your data.

Eric Lamarre: Why? Because this data sometimes will be labeled differently. And so now we don’t have very good data. This is where data products come in. Data product is that small, cross-functional team, optimized for data. But their job is to curate customer data product, if that’s what we focus on, or operations data product or supply chain data product.

It’s a refined product that can be consumed with just the call of an API by any of the teams for which we have given access to this data. So it helps really accelerate the deployment of business intelligence, or even AI models, because now I have made it possible for everybody in the organization to consume something where the data is well-structured.

Rodney Zemmel: Two other thoughts on that. We’ve seen, way too many times, this approach: first, we’ll build a giant data lake, we’ll get all the data in the company, and we’ll find clever ways to mix it with all the data from the outside world. That’s a project that will take five years to build before you actually get any value from it. And then point two is that data is a marketplace, with a supply side and a demand side, and you have to measure both sides. You’d be amazed how many companies have put giant investments into data lakes that aren’t used or are barely used.

Dollars and sense required

Roberta Fusaro: So, what’s the key to adoption and scaling? It’s money, sure, but you also need to think about the users.

Rodney Zemmel: Investing should be behind it, not in a fluffy change-management way but in really thinking through the incentives, what it means for the business model, how it changes, how people spend their time.

A simple test question for whether companies are on the right side of how to do this is to ask, “Who’s responsible for adoption?” If the answer to that is the digital team or the chief digital officer, that’s the wrong answer. Adoption needs to be owned by the business owner of that area.

So the first thing to spend money on is actually, is adoption incentivized in the right way? A few dollars on incentive will often go a lot further than lots of dollars on the change story, and conducting workshops on why we need to change, and all that kind of stuff. The other thing, then, is having the teams work with frontline people right from the beginning, before a line of code is written.

Kate Smaje: There should be a clear link between how that adoption is then going to be used to scale toward the value that’s going to be created. So it’s very important not to just stop at adoption. I’ll give you a very simple example of this. This was a number of years ago, involving a company with a big warehouse operation. They said, “Kate, while you’re here, we have to show you this new app that we’ve created. It’s brilliant.”

They had a sort of prototype version of this app on an iPad. And the data that they had was exactly the sort of thing that would make this warehouse operator make better decisions. No question. It was a beautiful front end and they were so proud of it. A member of my team very quietly, slightly timidly said, “Don’t the warehouse people wear gloves?”

And there was this sort of audible, “Oh, what on earth are we going to do now?” moment, where they just hadn’t thought it through because they weren’t obsessed enough with the user to think about not just the technology to make this brilliant set of decisions but also how are they going to use it? And these warehouse operators wear gloves because it’s really cold in there. You have to wear gloves as part of the safety procedure.

So you’ve got to put yourself in the mindset of, “How is this technology going to be used?” Because, ultimately, if it can’t be used differently and you can’t change a business model around it, then it’s just technology.

Rodney Zemmel: So, how you’re developing things in a way that there is more value accruing to the user of the thing than there is to the collector of the data is an incredibly important part of the art here.

Roberta Fusaro: Part art, but mostly talent and grit. And to go back to what Rodney said at the beginning . . .

Rodney Zemmel: To succeed in a digital transformation, it needs to be a CEO agenda item. It needs to mobilize cross-functional teams across the company in a unique way. It’s going to need some investment to sustain it.

Roberta Fusaro: And Rewired lays out the method for all those things.

Rodney Zemmel: We know that there is a real learning curve to applying the method. So we’re also hoping that, by publishing the book, we’re not making ourselves obsolete. But I guess we’ll see.

Roberta Fusaro: For more information about Rewired and the challenges and opportunities of digital transformation, visit McKinsey.com.

Eric Lamarre

Eric LamarreSenior Partner, Boston

LinkedInEmail

Kate Smaje

Kate SmajeSenior Partner, London

LinkedInEmail

Rodney ZemmelSenior Partner, New York

LinkedInEmail

Roberta Fusaro is an editorial director in the Waltham, Massachusetts, office.

Article link: https://www.mckinsey.com/capabilities/mckinsey-digital/our-insights/what-really-works-when-it-comes-to-digital-and-ai-transformations?

NIST adds 40 potential quantum-resistant algorithms to growing roster – Nextgov

Posted by timmreardon on 07/19/2023
Posted in: Uncategorized.

By ALEXANDRA KELLEY JULY 17, 2023

The standards agency’s work to identify and standardize post-quantum cryptographic encryption methods was highlighted as crucial to U.S. cybersecurity implementation plans.

Forty new algorithms were selected as additional candidates for the National Institute of Standards and Technology’s post-quantum cryptography digital signature schemes, part of the agency’s ongoing effortsto help U.S. networks prepare for the advent of an advanced operational quantum computer.

Announced on Monday, the latest potential additions to the PQC standardization catalog come from a September 2022 call for additional submissions. In July 2022 NIST announced the selection of four quantum-resistant algorithms that had passed agency evaluation, and these four will be standardized for network deployment. 

“NIST initiated a public process to select quantum-resistant public-key cryptographic algorithms for standardization in response to the substantial development and advancement of quantum computing,” the agency noted on its project page.

Out of the 50 submissions received in response to the September 2022 call, the agency determined 40 to be complete, according to the submission requirements. Evaluating those 40 is estimated to last “several years,” according to the agency.

NIST’s call for submissions for quantum-resistant algorithms officially began in December 2016. This latest call was the official fourth round of algorithm candidate submissions, and the agency anticipates holding a fifth round in April 2024.

“NIST greatly appreciates all of the candidate submission teams for their continued efforts in the standardization process,” the agency wrote.

Preparing for the advent of quantum computing has become synonymous with good cybersecurity practices in the past several years, as the federal government allocates more research and initiatives to updating the nation’s algorithmic infrastructure to a quantum-resilient environment. 

The recently-released National Cybersecurity Implementation Strategy also highlighted the importance of NIST’s PCQ standardization and solicitation efforts as important to implementing a stronger cybersecurity posture across the nation.

Article link: https://www.nextgov.com/emerging-tech/2023/07/nist-adds-40-potential-quantum-resistant-algorithms-growing-roster/388577/

5 Behaviors of Leaders Who Embrace Change – HBR

Posted by timmreardon on 07/18/2023
Posted in: Uncategorized.
  • Edith Onderick-Harvey

May 18, 2018

Summary

Successful change-agile leaders at all levels in the organization respond to changes in the business environment by seizing opportunities, including throwing out old models and developing new ways of doing business. They try to make change thinking contagious, embedding it into everything they do from the most fundamental daily interactions to the most complex strategy. Change-agile leaders demonstrate several integrated behaviors that, together, create a competitive advantage for the organization. They share a compelling, clear purpose with employees. They look ahead and see new opportunities. They create a safe psychological space for teams to discuss the challenges of working together and of the integration overall. They promote calculated risk-taking and experimentation, and encourage cross-boundary collaborations to build products, attract customers, and achieve results.

At best, mergers and acquisitions (M&A’s) have a 50/50 chance of reaching their intended results. Study after study puts the failure rate closer to 70-90%. Why is the failure rate so high? Repeatedly, research cites the human factor as the leading reason why mergers and acquisitions fail.

Part of the issue is how organizations view the human aspect of the closing date, which is usually treated as the end of the transaction, when it’s really just the start of change. Organizations, processes, and cultures will be integrated for weeks and months after the organizations come together, causing disruption and uncertainty. Leaders in the M&A environment are managing an organization that hasn’t existed before. Their people are no longer part of the organization they joined. Their sense of normal is disrupted. In response, they may choose to hold on to the past and what’s comfortable or feel a bit disoriented as they search for their place in the new company. In the midst of the disruption, new challenges and opportunities will arise not just in the integration of the new organization, but in its marketplace and among its customers. And, the merger or acquisition won’t be the last change they are facing. CEB reports that the average organization has undergone five enterprise-wide changes in the past three years and 73% expect change to accelerate (URL: https://www.cebglobal.com/insights/change-management.html). In this environment, change agility needs to be part of the new organization’s and leaders’ DNA. It can’t just exist in a few people in the organization; it needs to be the way business gets done.

Successful change-agile leaders at all levels in the organization respond to changes in the business environment by seizing opportunities, including throwing out old models and developing new ways of doing business. They try to make change thinking contagious, embedding it into everything they do from the most fundamental daily interactions to the most complex strategy.

Change-agile leaders demonstrate five integrated behaviors that, together, create a competitive advantage for the organization. They:

Share a compelling, clear purpose:Purpose is the guardrail for actions. Change agility requires an answer to the question “Why?”, so that people can fight the natural instinct to resist change. The answer needs to tap into what’s meaningful and important, providing an irresistible invitation to come along. As CEO Shoei Yamana of Konica Minolta has said, “My belief is that people don’t work for numbers…they need to share the same belief that they are creating value in some way.” If you can’t articulate a clear purpose behind the changes being made, it’s unlikely that your employees will be able to implement them.

Look ahead and see opportunity: Most leaders view this as the role of senior executives. To infuse change agility into your culture, mid- and front-line leaders — who are closest to the markets, customers, and daily operations — need to be encouraged and incented to see opportunities in what they do every day. They need to look beyond this month or this year to identify trends and take action. History is littered with market leaders who didn’t see the opportunities ahead or take action on them. Kodak, Sears, and Motorola are just a few.  To build this behavior into the organization, leaders should:

  • Make opportunity-seeking part of the regular conversation. Simply asking questions like “What are our customers talking about? What do you think they will want a year or two from now? What new trends do you think will impact us?” sends the message that looking ahead is important.
  • Provide space to experiment. When a potential opportunity is identified, allow individuals or groups to experiment with ways to take advantage of it. Minimize the need for multiple layers of sign-off.  It makes the culture too risk averse and squelches momentum.
  • Advertise successes. Nothing breeds success like success. Tell the stories at company events and recognize middle and front-line leaders who are looking ahead and identifying opportunities. Show that the status quo is not enough anymore.

Seek out what’s not working: The old adage says that bad news doesn’t travel up. During the integration of an acquisition or even in the internal merger of business units, there will be bad news that the organization needs to learn from. But for real learning to occur, people need to feel psychologically safe to share the good, the bad, and the ugly.

Consider this example: Derek was leading the integration of several internal units into a merged organization. This integration created a new team of direct reports for him. Over the course of the integration, he worked on creating the psychological safety for his team to discuss the challenges of working together and of the integration overall. They used a trust framework to openly talk about what they were doing to build and breakdown trust with each other. Individuals discussed what they brought to the team and what they needed from their fellow team members.  They did pulse checks to assess their alignment and where there was work to do. They had difficult conversations. This type of open conversation and psychological safety cascaded through the new 250-person organization. It culminated in a two-day meeting for the entire organization that included open conversations about what was working well and what opportunities and challenges this new organization needed to address for its clients. The meeting also included a read-out of the employee engagement survey scores that, in the midst of the turbulence of an integration, were among the highest in the company’s history.

Promote calculated risk-taking and experimentation: Robert Kennedy, paraphrasing George Bernard Shaw, said, “There are those who look at things the way they are, and ask why. I dream of things that never were, and ask why not?” Too often, our traditional organizations’ first response to a risk is to ask, “Why?”  Change agility requires leaders to ask “why not?” and to establish opportunities for pilots, prototypes, and experimentation. Experimentation is an integral part of R&D. While an overall strategy informs the researchers’ focus, any R&D scientist will tell you that there are sometimes dozens of experiments that don’t get results and that, without the failures, they couldn’t find the successes.

Look for boundary-spanning partnerships: As work becomes more complex, it takes teams and cross-boundary collaborations to build products, attract customers, and achieve results.  Change-agile leaders and organizations are replacing functional silos with formal and informal organizations that allow for the rapid flow of information and decision-making around a product, customer, or region. For example, Maureen is a mid-level learning and development leader at a global tech company that’s growing rapidly through acquisition. Having growth and development opportunities for key talent has been critical for retention, and enhancing the employee experience is a strategic focus. Learning and development teams are dispersed across the organization, working independently to address business unit needs. Looking ahead, Maureen sensed that the company was also going to be focusing on efficiency in response to market changes and the continued integration of the acquired companies. Seeing the opportunity to improve the employee experience and create cost efficiencies across the learning organizations, she brought together her fellow learning leaders. They designed and implemented a new shared services organization that centralizes training development and vendor management. It will create standardized branding and processes, leverage tools, and create cost savings from consistently negotiated contracts. This creates a more consistent employee experience across learning functions and more efficiently addresses learning needs across the company.

These five behaviors, when used in concert with each other, create culture shifts that increase change agility. They are shifts that need to be made at all levels of leadership. They can mean the difference between M&A success and being an also-ran.

Edith Onderick-Harvey is managing partner at NextBridge Consulting, an organization change and leadership development consulting firm focused on helping clients stay ahead of the curve. She is a widely-recognized consultant, speaker, and author who has helped clients embrace change for over 25 years. Edith is the author of the Marshall Goldsmith endorsed book “Getting Real: Strategies for Leadership in Today’s Innovation-Hungry, Time-Strapped, Multi-Tasking World of Work.”

Article link: https://hbr.org/2018/05/5-behaviors-of-leaders-who-embrace-change?

SIX PERSPECTIVES ON AGILE SOFTWARE DELIVERY – Army PEO EIS

Posted by timmreardon on 07/18/2023
Posted in: Uncategorized.

Erika Christ, PEO EIS Strategic Communication Directorate

July 13, 2023

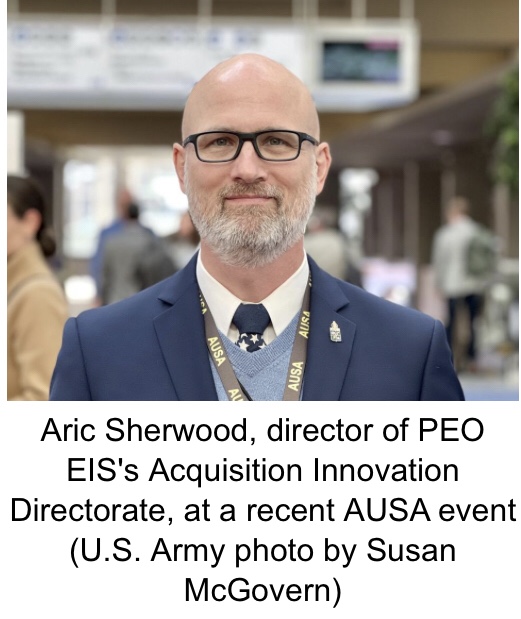
As the director of PEO EIS’s Acquisition Innovation Directorate, one of Aric Sherwood’s responsibilities is establishing the organization’s Lean Agile Center of Excellence (LACE). The LACE will support program managers (PMs) on their Agile journey through Agile coaching, standardizing metrics and reducing impediments to successful value delivery. The LACE will also interface with Army senior leaders, supporting organizations and functional requirements owners to ensure they understand the Agile software delivery model and what they will be expected to do in support. Sherwood recently shared his thoughts on six topics related to delivering software at speed and scale.

1.  Best practices in using the DOD’s Software Acquisition Pathway: 

“We’re just starting this journey but having a willing partner on the functional side is key. They play a critical role in Agile software development, and their participation is far greater than in traditional waterfall development. That said, a well-developed user agreement is one thing that needs to be focused on to fully codify that relationship.” 


2.  Ways to improve the Software Acquisition Pathway: 

“I would like to see a ‘software’ appropriation, very similar to BA-08, that would allow flexibility in how we fund software development. While we can plan for appropriate funding, it is often not aligned with the reality of what happens two years into a development. Being able to flow from Research, Development, Test and Evaluation (RDT&E) to Procurement — and even Operations and Maintenance — without having to do budget drills would be valuable.” 

 
3.  Advice to PMs considering Agile and DEVSECOPS: 

“DO IT! The Soldier’s direct involvement in what gets delivered and the speed at which value is deployed are both key reasons why. The DOD should be looking to apply Agile methodologies to not just software, but materiel development as well.” 

 
4. Ways to measure progress and ensure successful partnerships: 

“Again, we’re just starting our journey and have limited data points, but we plan to measure progress at the sprint and program increment levels based on value delivered. We want to understand our velocity and value delivery to ‘fail fast,’ learn and adjust. We plan to partner with industry in a non-traditional way — contracting for manpower versus for a delivered product. We’re working with our supporting Army Contracting Commands on what that might look like, but it will be more capacity-based.”   

 
5.  Successful policies and practices PEO EIS has implemented: 

“We’ve been adapting the DODI 5000.87 Software Acquisition Pathway to our enterprise business systems to the greatest extent possible. Army leadership has been very supportive of this approach, and we are leading the way by making the Software Acquisition Pathway the default recommendation for all new efforts, as well as transitioning many of our legacy systems to Agile development — even if we don’t transition to the Software Acquisition Pathway. This allows direct Soldier input into the systems they use to manage their career, pay, etc., while delivering value incrementally and sooner.” 

 
6. Skills and training that PMs need: 

“To quote Yoda, ‘You must unlearn what you have learned.’ I joke that the Agile Manifesto is largely 180 degrees from traditional DOD and Army thinking about software development. In addition to the Army’s digital transformation efforts, we are upskilling our workforce from PMs on down to understand the shift to Agile thinking, and they are jumping in and executing. We know we won’t get it right the first time, and — dare I say it — that’s OK. We will learn and adjust. As long as we have the support of our leadership, we will succeed.”

Article link: https://www.eis.army.mil/newsroom/news/peo-eis-wide/six-perspectives-agile-software-delivery

New White House cyber plan leaves digital identity action items out – Nextgov

Posted by timmreardon on 07/17/2023
Posted in: Uncategorized.

By NATALIE ALMSJULY 13, 2023

Officials noted that identity action items could still be included in later iterations of the national cybersecurity strategy implementation plan.

The White House’s implementation plan for the national cybersecurity strategy has 69 initiatives for agencies to carry out, but lacks any action items on digital identity, a shock to stakeholders who want action.

“The Brits invented the word ‘gobsmacked’ to describe things like this,” Jeremy Grant, longtime digital identity expert who has worked at the National Institute of Standards and Technology and now runs the Better Identity Coalition interest group, told Nextgov/FCW.

The strategy, released in March, had “[supporting] development of a digital identity ecosystem” as a strategic objective and previewed government investments in digital identity solutions, like providing attribute validation services, updating standards and developing digital identity platforms.

But the new “roadmap,” as acting national cyber director Kemba Walden called it in a briefing with reporters, doesn’t include anything on digital identity, the only objective left out other than data privacy.

When asked about the absence, a senior administration official told reporters: “This is an iterative document, so just because you’re not seeing an initiative tied to a strategic objective today doesn’t mean it won’t be there for the next go-round.”

The White House’s current efforts on digital identity, they said, are going to be coming from other ongoing efforts around digital identity and fraud.

“You’ve heard… the administration several times talk about work on digital identity actions in the context of identity fraud and combating that, and that is fundamentally what is holding that space right now,” the official said. “The administration is committed to action in that space, and that is still pre-decisional activity, but we would expect that follow-on actions from the identity fraud work would come into future iterations of the implementation plan.”

President Biden first promised an executive order on the topic in his 2022 State of the Union address, although it has yet to materialize. 

Related articles

White House says an anticipated executive order on identity theft is coming, here’s what experts want in it

Login.gov is still ‘vital’ despite setbacks, GSA official says

“When you have this many departments and you actually have an executive order that is requiring an actual change of behavior, it requires a level of vetting from Justice Department, the [Office of Legal Counsel] and each counsel’s office that is a bit more from other executive orders,” White House senior advisor Gene Sperling told reporters in March during a call about a $1.6 billion anti-fraud proposal, including $600 million for identity theft and fraud prevention.

“It should be out soon, but I don’t want to predict what I can’t control, which is the time it takes to get everybody to completely — every counsel’s office to completely sign off,” said Sperling.

As for the impact of the omission, the original strategy itself noted that “the lack of secure, privacy-preserving, consent-based digital identity solutions allows fraud to flourish, perpetuates exclusion and inequity and adds inefficiency to our financial activities and daily life.”

There were 14,817 identity crimes reported in 2022, according to the nonprofit Identity Theft Resource Center. The center’s president and CEO Eva Velasquez told Nextgov/FCW via email that “the U.S. needs a digital identity strategy to help reduce identity fraud and the number of people who are victims of identity crimes.”

“I think it was a huge oversight,” Linda Miller — former deputy executive director of the government’s Pandemic Response Accountability Committee and founder and CEO of boutique consultancy Audient Group — told Nextgov/FCW via email about the lack of digital identity in the implementation plan. “It is very surprising and disappointing to me.

“Identity theft is a primary threat vector for government fraud at the federal, state and local levels of government,” she said. “We saw historic levels of identity theft-based fraud in unemployment assistance during the pandemic, and nation state actors used stolen identities to defraud many other pandemic programs as well.”

Jordan Burris, former chief of staff in the Office of the Federal CIO from 2017 to 2021 and current vice president and head of public sector strategy at digital identity company Socure said via email that although “it is understood that the plan may not encompass all the activities underway by the administration,” the omission of digital identity is “deeply concerning.

“I fear that the failure to include digital identity in the cybersecurity implementation plan signals this critical work is being deferred, all the while we continue to see an uptick in identity theft, synthetic fraud and AI-driven attacks targeting government programs,” he said. “There appears to be little momentum at the federal level to change the status quo.”

A draft of the promised executive order obtained by Nextgov/FCW in February focused heavily on scaling the General Services Administration’s identity service, Login.gov  —although nothing is official policy until an actual order is issued. Since then, GSA’s inspector general issued a report in March which found that GSA has misled agencies about the level of identity proofing standards Login.gov met. 

Grant’s identity-focused trade group, meanwhile, has urged the White House to focus on digitizing identity credentials with a task force, noting that “White House leadership is essential,” given the dispersion of issuers of identity documents across levels of government. 

Grant told Nextgov/FCW that the “hope is that in the weeks ahead, we’ll see additional details from the administration outlining how they will protect millions of Americans from identity-related cybercrime and identity theft, by strengthening the security and privacy of digital credentials.”

As for when action items on digital identity might be added to the implementation plan, Walden said that the document will “evolve” over time, with a 2.0 version coming next year as the first of annual updates.

“The implementation plan does not capture all of the cybersecurity activities in the federal government, nor does it intend to,” she said. “What it does do is capture key initiatives that we must get done in the near term.”

The White House declined to comment on the promised executive order.

Editor’s note: This article has been updated to include comment from Eva Velasquez and White House response.

Article link: https://www.nextgov.com/cybersecurity/2023/07/new-white-house-cyber-plan-leaves-digital-identity-action-items-out/388466/

Want to track pandemic relief spending? Data problems make that difficult, committee says – Nextgov

Posted by timmreardon on 07/17/2023
Posted in: Uncategorized.

By NATALIE ALMSJULY 11, 2023

“These challenges limit the degree of transparency into the use of pandemic relief funds,” a new report from the Pandemic Response Accountability Committee says.

Even government watchdogs run into data gaps when they try to track pandemic spending, according to a new report by the Pandemic Response Accountability Committee and 10 inspectors general offices.

“You may want to know how much pandemic relief money your community received from the federal government,” the PRAC websitereads. “But getting the answers can be difficult because of the quality and availability of federal spending data.”

The PRAC — a group of inspectors general set up by Congress to coordinate and support oversight of pandemic relief — picked six random communities across the country to try to find out how much pandemic spending they received from the over $5 trillion doled out through grants, loans, contracts, direct assistance and other forms. Future reporting will focus on how the six communities used the funding.

Over 40 federal agencies and hundreds of programs were responsible for dispersing pandemic relief spending, the report states, but the watchdogs zeroed in on funding given by 10 agencies specifically. The group found a topline of about $2.65 billion in pandemic relief funding went to these six communities via 89 programs and subprograms in those agencies from March 2020 to September 2021. 

But getting that information was no easy task: “Tracking pandemic funds to the community level required the use of multiple federal, state and local data systems, and ultimately we had to contact state and local entities directly to gain a better understanding and fill data gaps,” the report said.

Data collection and system shortcomings and differences in data formats occurred across federal, state and local levels of government.

“Sometimes data was either unreliable or unavailable. In other cases, we had to use data sources that the public can’t access,” the website said. “One partner had to access five federal non-public databases to determine the recipients in a single program.”

For example, the primary source of federal government spending data, USAspending.gov, “does not definitively track COVID-19 supplemental spending at the subrecipient level,” the PRAC previously reported. 

The newest report notes that “attempts to only use USAspending.gov would not enable full identification of pandemic funding due to differences among USAspending.gov and other non-public data sources not accounted for on the publicly available USAspending.gov website.”

The group is “continuing to explore” how these differences affect the quality of data on the site, it says, and for now, advises that “continuing to disclose data limitations in USAspending.gov or pursuing other efforts around data reporting can help increase transparency of federal spending for the public.”

The latest report didn’t come with new recommendations, but it did point to previously made recommendations to the Office of Management and Budget about federal spending data gaps, including creating a feasibility study on how to better track subrecipient funding and engaging with lawmakers to consider “extending independent oversight of USAspending.gov data submissions.”

“While it may not be practical for every federal spending dollar to be integrated into USAspending.gov, opportunities exist to increase federal spending data transparency, a shared interest for all stakeholders, especially when the federal government administers large emergency spending programs to address nationwide challenges and respond to new disasters,” the report said.

For now, “we believe these challenges limit the degree of transparency into the use of pandemic relief funds,” the report said.

“If the PRAC Oversight Team — comprised of auditing and data experts from across the accountability community — had such difficulty tracking the funds, then the general public and even members of Congress will likely also experience challenges in understanding how much of taxpayer funds were provided to communities,” the report concluded.

Article link: https://www.nextgov.com/analytics-data/2023/07/want-track-pandemic-relief-spending-data-problems-make-difficult-committee-says/388385/

DoD on House Oversight hot Seat for Financial Systems

Posted by timmreardon on 07/15/2023
Posted in: Uncategorized.

BY: JOSE RASCON

JUL 13, 2023 2:17 PM

House members today grilled officials from the Department of Defense (DoD) on a long-standing and vexing issue for Congress – the Pentagon’s inability to produce a clean audit opinion on its financial statements since that requirement went into effect for Federal agencies in 1990.

In a May 2023 report, the Government Accountability Office (GAO) explained that although DoD is responsible for about half of the Federal government’s discretionary spending, “DOD remains the only major federal agency that has never been able to receive a clean audit opinion on its financial statements.”

Since 1995, GAO has designated DOD financial management as high risk “because of pervasive deficiencies in its financial management systems, business processes, internal controls, and financial reporting,” the watchdog agency said.

“DOD should not get a free pass from the law, especially when other agencies that invest in priorities like health care, education, climate change, or economic growth are under high scrutiny and take important and difficult steps to comply with statutory auditing requirements,” stated Rep. Robert Garcia, D-Calif., today during a joint subcommittee hearing of the House Oversight and Accountability Committee.

John Tenaglia, principal director of Defense Pricing and Contracting at the DoD, blamed the current procurement system as one factor that’s stopping DoD from keeping better tabs on its finances.

“The standard procurement system needs to be retired. It’s a legacy system. It works, but we’re working with the comptroller on the standards to make sure that it communicates with the financial system, so it’s really all about the data standards behind that,” stated Tenaglia.

Asif Khan, director of Financial Management and Assurance at the GAO, discussed some of the reasons that DoD has not been able to produce a clean audit, including its use of older financial systems.

“It is helping that DoD is embracing technology” including robotic process automation in its financial work, Khan said. “It is freeing up the resources to be able to do more analytical work, but the problems are very pervasive across DoD and that’s why it’s taking them time,” to generate the ability to produce a clean audit, he said.

The issue of antiquated systems at DoD to manage the department’s finances was something that Rep. Gerry Connolly, D-Va., said can also be a hallmark of introducing cybersecurity risks.

“This directly affects the security of our missions, of our intelligence, of our defense planning on our new weapons systems development,” said Rep. Connelly.

Earlier this year, GAO released a new set of recommendations for the DoD on steps that the department needs to take to produce a clean audit.

Article link: https://www.meritalk.com/articles/dod-on-house-oversight-hot-seat-for-financial-systems/

How a Cloud Flaw Gave Chinese Spies a Key to Microsoft’s Kingdom – Wired

Posted by timmreardon on 07/14/2023
Posted in: Uncategorized.

Microsoft says hackers somehow stole a cryptographic key, perhaps no from its own network, that let them forge user identities and slip past cloud defenses.

FOR MOST IT professionals, the move to the cloud has been a godsend. Instead of protecting your data yourself, let the security experts at Google or Microsoft protect it instead. But when a single stolen key can let hackers access cloud data from dozens of organizations, that trade-off starts to sound far more risky.

Late Tuesday evening, Microsoft revealed that a China-based hacker group, dubbed Storm-0558, had done exactly that. The group, which is focused on espionage against Western European governments, had accessed the cloud-based Outlook email systems of 25 organizations, including multiple government agencies.

Those targets encompass US government agencies including the State Department, according to CNN, though US officials are still working to determine the full scope and fallout of the breaches. An advisory from the US Cybersecurity and Infrastructure Security Agencysays the breach, which was detected in mid-June by a US government agency, stole unclassified email data “from a small number of accounts.”

China has been relentlessly hacking Western networks for decades. But this latest attack uses a unique trick: Microsoft says hackers stole a cryptographic key that let them generate their own authentication “tokens”—strings of information meant to prove a user’s identity—giving them free rein across dozens of Microsoft customer accounts.

“We put trust in passports, and someone stole a passport-printing machine,” says Jake Williams, a former NSA hacker who now teaches at the Institute for Applied Network Security in Boston. “For a shop as large as Microsoft, with that many customers impacted—or who could have been impacted by this—it’s unprecedented.”

In web-based cloud systems, users’ browsers connect to a remote server and, when they enter credentials like a username and password, they’re given a bit of data, known as a token, from that server. The token serves as a kind of temporary identity card that lets users come and go as they please within a cloud environment while only occasionally reentering their credentials. To ensure that the token can’t be spoofed, it’s cryptographically signed with a unique string of data known as a certificate or key that the cloud service possesses, a kind of unforgeable stamp of authenticity.

Microsoft, in its blog postrevealing the Chinese Outlook breaches, has described a kind of two-stage breakdown of that authentication system. First, hackers were somehow able to steal a key that Microsoft uses to sign tokens for consumer-grade users of its cloud services. Second, the hackers exploited a bug in Microsoft’s token validation system, which allowed them to sign consumer-grade tokens with the stolen key and then use them to instead access enterprise-grade systems. All of this occurred despite Microsoft’s attempt to check for signatures from different keys for those different grades of token.

Microsoft says it has now blocked all tokens that were signed with the stolen key and replaced the key with a new one, preventing the hackers from accessing victims’ systems. The company adds that it has also worked to improve the security of its “key management systems” since the theft occurred.

But exactly how such a sensitive key, allowing such broad access, could be stolen in the first place remains unknown. WIRED contacted Microsoft, but the company declined to comment further.

In the absence of more details from Microsoft, one theory of how the theft occurred is that the token-signing key wasn’t in fact stolen from Microsoft at all, according to Tal Skverer, who leads research at the security Astrix, which earlier this year uncovered a token security issue in Google’s cloud. In older setups of Outlook, the service is hosted and managed on a server owned by the customer rather than in Microsoft’s cloud. That might have allowed the hackers to steal the key from one of these “on-premises” setups on a customer’s network.

Then, Skverer suggests, hackers might have been able to exploit the bug that allowed the key to sign enterprise tokens to gain access to an Outlook cloud instance shared by all the 25 organizations hit by the attack. “My best guess is that they started from a single server that belonged to one of these organizations,” says Skverer, “and made the jump to the cloud by abusing this validation error, and then they got access to more organizations that are sharing the same cloud Outlook instance.”

But that theory doesn’t explain why an on-premises server for a Microsoft service inside an enterprise network would be using a key that Microsoft describes as intended for signing consumer account tokens. It also doesn’t explain why so many organizations, including US government agencies, would all be sharing one Outlook cloud instance.

Another theory, and a far more troubling one, is that the token-signing key used by the hackers was stolen from Microsoft’s own network, obtained by tricking the company into issuing a new key to the hackers, or even somehow reproduced by exploiting mistakes in the cryptographic process that created it. In combination with the token validation bug Microsoft describes, that may mean it could have been used to sign tokens for any Outlook cloud account, consumer or enterprise—a skeleton key for a large swath, or even all, of Microsoft’s cloud.

The well-known web security researcher Robert “RSnake” Hansen says he read the line in Microsoft’s post about improving the security of “key management systems” to suggest that Microsoft’s “certificate authority”—its own system for generating the keys for cryptographically signing tokens—was somehow hacked by the Chinese spies. “It’s very likely there was either a flaw in the infrastructure or configuration of Microsoft’s certificate authority that led an existing certificate to be compromised or a new certificate to be created,” Hansen says.

If the hackers did in fact steal a signing key that could be used to forge tokens broadly across consumer accounts—and, thanks to Microsoft’s token validation issue, on enterprise accounts, too—the number of victims could be far greater than 25 organizations Microsoft has publicly accounted for, warns Williams.

To identify enterprise victims, Microsoft could look for which of their tokens had been signed with a consumer-grade key. But that key could have been used to generate consumer-grade tokens, too, which might be far harder to spot given that the tokens might have been signed with the expected key. “On the consumer side, how would you know?” Williams asks. “Microsoft hasn’t discussed that, and I think there’s a lot more transparency that we should expect.”

Microsoft’s latest Chinese spying revelation isn’t the first time state-sponsored hackers have exploited tokens to breach targets or spread their access. The Russian hackers who carried out the notorious Solar Winds supply chain attack also stole Microsoft Outlook tokens from victims’ machines that could be used elsewhere on the network to maintain and expand their reach into sensitive systems.

For IT administrators, those incidents—and particularly this latest one—suggest some of the real-world trade-offs of migrating to the cloud. Microsoft, and most of the cybersecurity industry, has for years recommended the move to cloud-based systems to put security in the hands of techgiants rather than smaller companies. But centralized systems can have their own vulnerabilities—with potentially massive consequences.

“You’re handing over the keys to the kingdom to Microsoft,” says Williams. “If your organization is not comfortable with that now, you don’t have good options.”

Andy Greenberg is a senior writer for WIRED, covering hacking, cybersecurity and surveillance. He’s the author of the new book Tracers in the Dark: The Global Hunt for the Crime Lords of Cryptocurrency. His last book was *[Sandworm: A New Era of Cyberwar and the Hunt for the Kremlin’s Most… Read more

Article link: https://www.wired.com/story/microsoft-cloud-attack-china-hackers/

FACT SHEET: Biden-⁠Harris Administration Publishes the National Cybersecurity Strategy Implementation Plan

Posted by timmreardon on 07/14/2023
Posted in: Uncategorized.

Read the full Implementation Plan here

President Biden has made clear that all Americans deserve the full benefits and potential of our digital future. The Biden-Harris Administration’s recently released National Cybersecurity Strategy calls for two fundamental shifts in how the United States allocates roles, responsibilities, and resources in cyberspace:

  1. Ensuring that the biggest, most capable, and best-positioned entities – in the public and private sectors – assume a greater share of the burden for mitigating cyber risk
  2. Increasing incentives to favor long-term investments into cybersecurity

Today, the Administration is announcing a roadmap to realize this bold, affirmative vision. It is taking the novel step of publishing the National Cybersecurity Strategy Implementation Plan (NCSIP) to ensure transparency and a continued path for coordination. This plan details more than 65 high-impact Federal initiatives, from protecting American jobs by combatting cybercrimes to building a skilled cyber workforce equipped to excel in our increasingly digital economy. The NCSIP, along with the Bipartisan Infrastructure Law, CHIPS and Science Act, Inflation Reduction Act, and other major Administration initiatives, will protect our investments in rebuilding America’s infrastructure, developing our clean energy sector, and re-shoring America’s technology and manufacturing base.

Each NCSIP initiative is assigned to a responsible agency and has a timeline for completion. Some initiatives, such as the issuance of the Administration’s Cybersecurity Priorities for the Fiscal Year 2025 Budget, have been completed ahead of schedule. Other completed activities, such as the transmittal of the May 26th Department of Defense 2023 Cyber Strategy to Congress, and the June 20th creation of a new National Security Cyber Section by the Justice Department, are key milestones in completing initiatives. This is the first iteration of the plan, which is a living document that will be updated annually.

Eighteen agencies are leading initiatives in this whole-of-government plan demonstrating the Administration’s deep commitment to a more resilient, equitable, and defensible cyberspace. The Office of the National Cyber Director (ONCD) will coordinate activities under the plan, including an annual report to the President and Congress on the status of implementation, and partner with the Office of Management and Budget (OMB) to ensure funding proposals in the President’s Budget Request are aligned with NCSIP initiatives. The Administration looks forward to implementing this plan in continued collaboration with the private sector, civil society, international partners, Congress, and state, local, Tribal, and territorial governments. As an example of the Administration’s commitment to public-private collaboration, ONCD is also working on a request for information regarding cybersecurity regulatory harmonization that will be published in the near future. 

The NCSIP is not intended to capture all Federal agency activities in support of the NCS. The following are sample initiatives from the plan, which is organized by the NCS pillars and strategic objectives.

Pillar One | Defending Critical Infrastructure

  • Update the National Cyber Incident Response Plan (1.4.1): During a cyber incident, it is critical that the government acts in a coordinated manner and that private sector and SLTT partners know how to get help. The Cybersecurity and Infrastructure Security Agency (CISA) will lead a process to update the National Cyber Incident Response Plan to more fully realize the policy that “a call to one is a call to all.” The update will also include clear guidance to external partners on the roles and capabilities of Federal agencies in incident response and recovery.

Pillar Two | Disrupting and Dismantling Threat Actors

  • Combat Ransomware (2.5.2 and 2.5.4): Through the Joint Ransomware Task Force, which is co-chaired by CISA and the FBI, the Administration will continue its campaign to combat the scourge of ransomware and other cybercrime. The FBI will work with Federal, international, and private sector partners to carry out disruption operations against the ransomware ecosystem, including virtual asset providers that enable laundering of ransomware proceeds and web fora offering initial access credentials or other material support for ransomware activities. A complementary initiative, led by CISA, will include offering resources such as training, cybersecurity services, technical assessments, pre-attack planning, and incident response to high-risk targets of ransomware, like hospitals and schools, to make them less likely to be affected and to reduce the scale and duration of impacts if they are attacked.

Pillar Three | Shaping Market Forces and Driving Security and Resilience

  • Software Bill of Materials (3.3.2): Increasing software transparency allows market actors to better understand their supply chain risk and to hold their vendors accountable for secure development practices. CISA continues to lead work with key stakeholders to identify and reduce gaps in software bill of materials (SBOM) scale and implementation. CISA will also explore requirements for a globally-accessible database for end of life/end of support software and convene an international staff-level working group on SBOM.

Pillar Four | Investing in a Resilient Future

  • Drive Key Cybersecurity Standards (4.1.3, 4.3.3): Technical standards are foundational to the Internet, and U.S. leadership in this area is essential to the vibrancy and security of cyberspace. Consistent with the National Standards Strategy, the National Institute of Standards and Technology (NIST) will convene the Interagency International Cybersecurity Standardization Working Group to coordinate major issues in international cybersecurity standardization and enhance U.S. federal agency participation in the process. NIST will also finish standardization of one or more quantum-resistant publickey cryptographic algorithms.

Pillar Five | Forging International Partnerships to Pursue Shared Goals

  • International Cyberspace and Digital Policy Strategy (5.1.1 and 5.1.2): Cyberspace is inherently global, and policy solutions must reflect close collaboration with our partners and allies. The Department of State will publish an International Cyberspace and Digital Policy Strategy that incorporates bilateral and multilateral activities. State will also work to catalyze the development of staff knowledge and skills related to cyberspace and digital policy that can be used to establish and strengthen country and regional interagency cyber teams to facilitate coordination with partner nations.

Article link: https://www.whitehouse.gov/briefing-room/statements-releases/2023/07/13/fact-sheet-biden-harrisadministration-publishes-thenational-cybersecurity-strategyimplementation-plan/

Posts navigation

← Older Entries
Newer Entries →
  • Search site

  • Follow healthcarereimagined on WordPress.com
  • Recent Posts

    • By Barring Profits on Basic Coverage, Switzerland Keeps Insurers from Denying Care – Commonwealth Fund 10/19/2026
    • Patients’ Perspectives on AI in Primary Care – Commonwealth Fund 09/11/2026
    • Bitcoin Mining Energy Footprint 08/06/2026
    • Closing the AI Hype Gap 08/05/2026
    • Why Artificial Intelligence is Neither Artificial, Nor Intelligent 07/31/2026
    • Agentic AI, explained 07/05/2026
    • Heeding the pope’s call to ensure AI protects human dignity – MIT Sloan Management 06/01/2026
    • Association between Wealth and Mortality in the United States and Europe – New England Journal of Medicine 05/30/2026
    • U.S. Health Care from a Global Perspective, 2026 – The Commonwealth Fund 05/30/2026
    • Anthropic co-founder Chris Olah’s remarks on Pope Leo XIV’s encyclical “Magnifica humanitas” 05/28/2026
  • Categories

    • Accountable Care Organizations
    • ACOs
    • AHRQ
    • American Board of Internal Medicine
    • Big Data
    • Blue Button
    • Board Certification
    • Cancer Treatment
    • Data Science
    • Digital Services Playbook
    • DoD
    • EHR Interoperability
    • EHR Usability
    • Emergency Medicine
    • FDA
    • FDASIA
    • GAO Reports
    • Genetic Data
    • Genetic Research
    • Genomic Data
    • Global Standards
    • Health Care Costs
    • Health Care Economics
    • Health IT adoption
    • Health Outcomes
    • Healthcare Delivery
    • Healthcare Informatics
    • Healthcare Outcomes
    • Healthcare Security
    • Helathcare Delivery
    • HHS
    • HIPAA
    • ICD-10
    • Innovation
    • Integrated Electronic Health Records
    • IT Acquisition
    • JASONS
    • Lab Report Access
    • Military Health System Reform
    • Mobile Health
    • Mobile Healthcare
    • National Health IT System
    • NSF
    • ONC Reports to Congress
    • Oncology
    • Open Data
    • Patient Centered Medical Home
    • Patient Portals
    • PCMH
    • Precision Medicine
    • Primary Care
    • Public Health
    • Quadruple Aim
    • Quality Measures
    • Rehab Medicine
    • TechFAR Handbook
    • Triple Aim
    • U.S. Air Force Medicine
    • U.S. Army
    • U.S. Army Medicine
    • U.S. Navy Medicine
    • U.S. Surgeon General
    • Uncategorized
    • Value-based Care
    • Veterans Affairs
    • Warrior Transistion Units
    • XPRIZE
  • Archives

    • October 2026 (1)
    • September 2026 (1)
    • August 2026 (2)
    • July 2026 (2)
    • June 2026 (1)
    • May 2026 (12)
    • April 2026 (4)
    • March 2026 (9)
    • February 2026 (6)
    • January 2026 (8)
    • December 2025 (11)
    • November 2025 (9)
    • October 2025 (10)
    • September 2025 (4)
    • August 2025 (7)
    • July 2025 (2)
    • June 2025 (9)
    • May 2025 (4)
    • April 2025 (11)
    • March 2025 (11)
    • February 2025 (10)
    • January 2025 (12)
    • December 2024 (12)
    • November 2024 (7)
    • October 2024 (5)
    • September 2024 (9)
    • August 2024 (10)
    • July 2024 (13)
    • June 2024 (18)
    • May 2024 (10)
    • April 2024 (19)
    • March 2024 (35)
    • February 2024 (23)
    • January 2024 (16)
    • December 2023 (22)
    • November 2023 (38)
    • October 2023 (24)
    • September 2023 (24)
    • August 2023 (34)
    • July 2023 (33)
    • June 2023 (30)
    • May 2023 (35)
    • April 2023 (30)
    • March 2023 (30)
    • February 2023 (15)
    • January 2023 (17)
    • December 2022 (10)
    • November 2022 (7)
    • October 2022 (22)
    • September 2022 (16)
    • August 2022 (33)
    • July 2022 (28)
    • June 2022 (42)
    • May 2022 (53)
    • April 2022 (35)
    • March 2022 (37)
    • February 2022 (21)
    • January 2022 (28)
    • December 2021 (23)
    • November 2021 (12)
    • October 2021 (10)
    • September 2021 (4)
    • August 2021 (4)
    • July 2021 (4)
    • May 2021 (3)
    • April 2021 (1)
    • March 2021 (2)
    • February 2021 (1)
    • January 2021 (4)
    • December 2020 (7)
    • November 2020 (2)
    • October 2020 (4)
    • September 2020 (7)
    • August 2020 (11)
    • July 2020 (3)
    • June 2020 (5)
    • April 2020 (3)
    • March 2020 (1)
    • February 2020 (1)
    • January 2020 (2)
    • December 2019 (2)
    • November 2019 (1)
    • September 2019 (4)
    • August 2019 (3)
    • July 2019 (5)
    • June 2019 (10)
    • May 2019 (8)
    • April 2019 (6)
    • March 2019 (7)
    • February 2019 (17)
    • January 2019 (14)
    • December 2018 (10)
    • November 2018 (20)
    • October 2018 (14)
    • September 2018 (27)
    • August 2018 (19)
    • July 2018 (16)
    • June 2018 (18)
    • May 2018 (28)
    • April 2018 (3)
    • March 2018 (11)
    • February 2018 (5)
    • January 2018 (10)
    • December 2017 (20)
    • November 2017 (30)
    • October 2017 (33)
    • September 2017 (11)
    • August 2017 (13)
    • July 2017 (9)
    • June 2017 (8)
    • May 2017 (9)
    • April 2017 (4)
    • March 2017 (12)
    • December 2016 (3)
    • September 2016 (4)
    • August 2016 (1)
    • July 2016 (7)
    • June 2016 (7)
    • April 2016 (4)
    • March 2016 (7)
    • February 2016 (1)
    • January 2016 (3)
    • November 2015 (3)
    • October 2015 (2)
    • September 2015 (9)
    • August 2015 (6)
    • June 2015 (5)
    • May 2015 (6)
    • April 2015 (3)
    • March 2015 (16)
    • February 2015 (10)
    • January 2015 (16)
    • December 2014 (9)
    • November 2014 (7)
    • October 2014 (21)
    • September 2014 (8)
    • August 2014 (9)
    • July 2014 (7)
    • June 2014 (5)
    • May 2014 (8)
    • April 2014 (19)
    • March 2014 (8)
    • February 2014 (9)
    • January 2014 (31)
    • December 2013 (23)
    • November 2013 (48)
    • October 2013 (25)
  • Tags

    Business Defense Department Department of Veterans Affairs EHealth EHR Electronic health record Food and Drug Administration Health Health informatics Health Information Exchange Health information technology Health system HIE Hospital IBM Mayo Clinic Medicare Medicine Military Health System Patient Patient portal Patient Protection and Affordable Care Act United States United States Department of Defense United States Department of Veterans Affairs
  • Upcoming Events

Blog at WordPress.com.
healthcarereimagined
Blog at WordPress.com.
  • Subscribe Subscribed
    healthcarereimagined
    Join 149 other subscribers

    Have a WordPress.com account? Log in now.

  • healthcarereimagined
    View site in Reader
    Manage subscriptionsSign upLog in
    Report this content
    Collapse this bar
Loading Comments...